Merge branch 'develop' into feat/fe/statuspage-3
This commit is contained in:
 Shemy Gan committed
commit
d8da182f60
48 files changed
+2777
-2333
No files matched your search
Generated
+543
-379
File diff suppressed because it is too large.
Load diff
+4
-4
@@ -14,11 +14,11 @@
|
|||||||
"@emotion/react": "^11.13.3",
|
"@emotion/react": "^11.13.3",
|
||||||
"@emotion/styled": "^11.13.0",
|
"@emotion/styled": "^11.13.0",
|
||||||
"@fontsource/roboto": "^5.0.13",
|
"@fontsource/roboto": "^5.0.13",
|
||||||
"@mui/icons-material": "6.2.1",
|
"@mui/icons-material": "6.3.0",
|
||||||
"@mui/lab": "6.0.0-beta.20",
|
"@mui/lab": "6.0.0-beta.21",
|
||||||
"@mui/material": "6.2.1",
|
"@mui/material": "6.3.0",
|
||||||
"@mui/x-charts": "^7.5.1",
|
"@mui/x-charts": "^7.5.1",
|
||||||
"@mui/x-data-grid": "7.23.3",
|
"@mui/x-data-grid": "7.23.5",
|
||||||
"@mui/x-date-pickers": "7.23.3",
|
"@mui/x-date-pickers": "7.23.3",
|
||||||
"@reduxjs/toolkit": "2.5.0",
|
"@reduxjs/toolkit": "2.5.0",
|
||||||
"axios": "^1.7.4",
|
"axios": "^1.7.4",
|
||||||
|
|||||||
@@ -100,7 +100,7 @@ const PATH_MAP = {
|
|||||||
pagespeed: "Dashboard",
|
pagespeed: "Dashboard",
|
||||||
infrastructure: "Dashboard",
|
infrastructure: "Dashboard",
|
||||||
account: "Account",
|
account: "Account",
|
||||||
settings: "Other",
|
settings: "Settings",
|
||||||
};
|
};
|
||||||
|
|
||||||
/**
|
/**
|
||||||
|
|||||||
@@ -86,7 +86,7 @@ export const getUptimeMonitorsByTeamId = createAsyncThunk(
|
|||||||
const res = await networkService.getMonitorsAndSummaryByTeamId({
|
const res = await networkService.getMonitorsAndSummaryByTeamId({
|
||||||
authToken: token,
|
authToken: token,
|
||||||
teamId: user.teamId,
|
teamId: user.teamId,
|
||||||
types: ["http", "ping", "docker"],
|
types: ["http", "ping", "docker", "port"],
|
||||||
});
|
});
|
||||||
return res.data;
|
return res.data;
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
|
|||||||
@@ -50,6 +50,11 @@ const CreateMonitor = () => {
|
|||||||
placeholder: "abc123",
|
placeholder: "abc123",
|
||||||
namePlaceholder: "My Container",
|
namePlaceholder: "My Container",
|
||||||
},
|
},
|
||||||
|
port: {
|
||||||
|
label: "URL to monitor",
|
||||||
|
placeholder: "localhost",
|
||||||
|
namePlaceholder: "Localhost:5173",
|
||||||
|
},
|
||||||
};
|
};
|
||||||
|
|
||||||
const { user, authToken } = useSelector((state) => state.auth);
|
const { user, authToken } = useSelector((state) => state.auth);
|
||||||
@@ -82,6 +87,7 @@ const CreateMonitor = () => {
|
|||||||
monitor.type === "http"
|
monitor.type === "http"
|
||||||
? `http${https ? "s" : ""}://` + monitor.url
|
? `http${https ? "s" : ""}://` + monitor.url
|
||||||
: monitor.url,
|
: monitor.url,
|
||||||
|
port: monitor.type === "port" ? monitor.port : undefined,
|
||||||
name: monitor.name === "" ? monitor.url : monitor.name,
|
name: monitor.name === "" ? monitor.url : monitor.name,
|
||||||
type: monitor.type,
|
type: monitor.type,
|
||||||
interval: monitor.interval * MS_PER_MINUTE,
|
interval: monitor.interval * MS_PER_MINUTE,
|
||||||
@@ -252,11 +258,23 @@ const CreateMonitor = () => {
|
|||||||
error={errors["url"] ? true : false}
|
error={errors["url"] ? true : false}
|
||||||
helperText={errors["url"]}
|
helperText={errors["url"]}
|
||||||
/>
|
/>
|
||||||
|
<TextInput
|
||||||
|
type="number"
|
||||||
|
id="monitor-port"
|
||||||
|
label="Port to monitor"
|
||||||
|
placeholder="5173"
|
||||||
|
value={monitor.port}
|
||||||
|
onChange={(event) => handleChange(event, "port")}
|
||||||
|
error={errors["port"] ? true : false}
|
||||||
|
helperText={errors["port"]}
|
||||||
|
hidden={monitor.type !== "port"}
|
||||||
|
/>
|
||||||
<TextInput
|
<TextInput
|
||||||
type="text"
|
type="text"
|
||||||
id="monitor-name"
|
id="monitor-name"
|
||||||
label="Display name"
|
label="Display name"
|
||||||
isOptional={true}
|
isOptional={true}
|
||||||
|
placeholder={monitorTypeMaps[monitor.type].namePlaceholder || ""}
|
||||||
value={monitor.name}
|
value={monitor.name}
|
||||||
onChange={(event) => handleChange(event, "name")}
|
onChange={(event) => handleChange(event, "name")}
|
||||||
error={errors["name"] ? true : false}
|
error={errors["name"] ? true : false}
|
||||||
@@ -321,6 +339,15 @@ const CreateMonitor = () => {
|
|||||||
checked={monitor.type === "docker"}
|
checked={monitor.type === "docker"}
|
||||||
onChange={(event) => handleChange(event, "type")}
|
onChange={(event) => handleChange(event, "type")}
|
||||||
/>
|
/>
|
||||||
|
<Radio
|
||||||
|
id="monitor-checks-port"
|
||||||
|
title="Port monitoring"
|
||||||
|
desc="Check whether your port is open or not."
|
||||||
|
size="small"
|
||||||
|
value="port"
|
||||||
|
checked={monitor.type === "port"}
|
||||||
|
onChange={(event) => handleChange(event, "type")}
|
||||||
|
/>
|
||||||
{errors["type"] ? (
|
{errors["type"] ? (
|
||||||
<Box className="error-container">
|
<Box className="error-container">
|
||||||
<Typography
|
<Typography
|
||||||
|
|||||||
@@ -1,14 +1,6 @@
|
|||||||
import PropTypes from "prop-types";
|
import PropTypes from "prop-types";
|
||||||
import { useEffect, useState, useCallback } from "react";
|
import { useEffect, useState, useCallback } from "react";
|
||||||
import {
|
import { Box, Button, Stack, Tooltip, Typography, useTheme } from "@mui/material";
|
||||||
Box,
|
|
||||||
Button,
|
|
||||||
Popover,
|
|
||||||
Stack,
|
|
||||||
Tooltip,
|
|
||||||
Typography,
|
|
||||||
useTheme,
|
|
||||||
} from "@mui/material";
|
|
||||||
import { useSelector } from "react-redux";
|
import { useSelector } from "react-redux";
|
||||||
import { useNavigate, useParams } from "react-router-dom";
|
import { useNavigate, useParams } from "react-router-dom";
|
||||||
import { networkService } from "../../../main";
|
import { networkService } from "../../../main";
|
||||||
@@ -17,7 +9,6 @@ import { formatDurationRounded, formatDurationSplit } from "../../../Utils/timeU
|
|||||||
import MonitorDetailsAreaChart from "../../../Components/Charts/MonitorDetailsAreaChart";
|
import MonitorDetailsAreaChart from "../../../Components/Charts/MonitorDetailsAreaChart";
|
||||||
import ButtonGroup from "@mui/material/ButtonGroup";
|
import ButtonGroup from "@mui/material/ButtonGroup";
|
||||||
import SettingsIcon from "../../../assets/icons/settings-bold.svg?react";
|
import SettingsIcon from "../../../assets/icons/settings-bold.svg?react";
|
||||||
import CertificateIcon from "../../../assets/icons/certificate.svg?react";
|
|
||||||
import UptimeIcon from "../../../assets/icons/uptime-icon.svg?react";
|
import UptimeIcon from "../../../assets/icons/uptime-icon.svg?react";
|
||||||
import ResponseTimeIcon from "../../../assets/icons/response-time-icon.svg?react";
|
import ResponseTimeIcon from "../../../assets/icons/response-time-icon.svg?react";
|
||||||
import AverageResponseIcon from "../../../assets/icons/average-response-icon.svg?react";
|
import AverageResponseIcon from "../../../assets/icons/average-response-icon.svg?react";
|
||||||
@@ -50,14 +41,7 @@ const DetailsPage = () => {
|
|||||||
const [certificateExpiry, setCertificateExpiry] = useState("N/A");
|
const [certificateExpiry, setCertificateExpiry] = useState("N/A");
|
||||||
const navigate = useNavigate();
|
const navigate = useNavigate();
|
||||||
|
|
||||||
const [anchorEl, setAnchorEl] = useState(null);
|
const certificateDateFormat = "MMM D, YYYY h A";
|
||||||
const openCertificate = (event) => {
|
|
||||||
setAnchorEl(event.currentTarget);
|
|
||||||
};
|
|
||||||
const closeCertificate = () => {
|
|
||||||
setAnchorEl(null);
|
|
||||||
};
|
|
||||||
|
|
||||||
const dateFormat = dateRange === "day" ? "MMM D, h A" : "MMM D";
|
const dateFormat = dateRange === "day" ? "MMM D, h A" : "MMM D";
|
||||||
const uiTimezone = useSelector((state) => state.ui.timezone);
|
const uiTimezone = useSelector((state) => state.ui.timezone);
|
||||||
|
|
||||||
@@ -72,6 +56,7 @@ const DetailsPage = () => {
|
|||||||
numToDisplay: 50,
|
numToDisplay: 50,
|
||||||
normalize: true,
|
normalize: true,
|
||||||
});
|
});
|
||||||
|
console.log(res?.data?.data);
|
||||||
setMonitor(res?.data?.data ?? {});
|
setMonitor(res?.data?.data ?? {});
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
logger.error(error);
|
logger.error(error);
|
||||||
@@ -95,7 +80,9 @@ const DetailsPage = () => {
|
|||||||
});
|
});
|
||||||
if (res?.data?.data?.certificateDate) {
|
if (res?.data?.data?.certificateDate) {
|
||||||
const date = res.data.data.certificateDate;
|
const date = res.data.data.certificateDate;
|
||||||
setCertificateExpiry(formatDateWithTz(date, dateFormat, uiTimezone) ?? "N/A");
|
setCertificateExpiry(
|
||||||
|
formatDateWithTz(date, certificateDateFormat, uiTimezone) ?? "N/A"
|
||||||
|
);
|
||||||
}
|
}
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
setCertificateExpiry("N/A");
|
setCertificateExpiry("N/A");
|
||||||
@@ -210,56 +197,6 @@ const DetailsPage = () => {
|
|||||||
alignSelf: "flex-end",
|
alignSelf: "flex-end",
|
||||||
}}
|
}}
|
||||||
>
|
>
|
||||||
<IconBox
|
|
||||||
mr={theme.spacing(4)}
|
|
||||||
onClick={openCertificate}
|
|
||||||
sx={{
|
|
||||||
cursor: "pointer",
|
|
||||||
"& svg": {
|
|
||||||
width: 23,
|
|
||||||
height: 23,
|
|
||||||
top: "52%",
|
|
||||||
},
|
|
||||||
}}
|
|
||||||
>
|
|
||||||
<CertificateIcon />
|
|
||||||
</IconBox>
|
|
||||||
<Popover
|
|
||||||
id="certificate-dropdown"
|
|
||||||
anchorEl={anchorEl}
|
|
||||||
open={Boolean(anchorEl)}
|
|
||||||
onClose={closeCertificate}
|
|
||||||
disableScrollLock
|
|
||||||
marginThreshold={null}
|
|
||||||
anchorOrigin={{
|
|
||||||
vertical: "bottom",
|
|
||||||
horizontal: "center",
|
|
||||||
}}
|
|
||||||
transformOrigin={{
|
|
||||||
vertical: "top",
|
|
||||||
horizontal: "center",
|
|
||||||
}}
|
|
||||||
slotProps={{
|
|
||||||
paper: {
|
|
||||||
sx: {
|
|
||||||
mt: theme.spacing(4),
|
|
||||||
py: theme.spacing(2),
|
|
||||||
px: theme.spacing(4),
|
|
||||||
width: 140,
|
|
||||||
backgroundColor: theme.palette.background.accent,
|
|
||||||
},
|
|
||||||
},
|
|
||||||
}}
|
|
||||||
>
|
|
||||||
<Typography variant="body2">Certificate Expiry</Typography>
|
|
||||||
<Typography
|
|
||||||
component="span"
|
|
||||||
fontSize={13}
|
|
||||||
color={theme.palette.text.primary}
|
|
||||||
>
|
|
||||||
{certificateExpiry}
|
|
||||||
</Typography>
|
|
||||||
</Popover>
|
|
||||||
{isAdmin && (
|
{isAdmin && (
|
||||||
<Button
|
<Button
|
||||||
variant="contained"
|
variant="contained"
|
||||||
@@ -302,6 +239,18 @@ const DetailsPage = () => {
|
|||||||
</>
|
</>
|
||||||
}
|
}
|
||||||
/>
|
/>
|
||||||
|
<StatBox
|
||||||
|
heading="certificate expiry"
|
||||||
|
subHeading={
|
||||||
|
<Typography
|
||||||
|
component="span"
|
||||||
|
fontSize={13}
|
||||||
|
color={theme.palette.text.primary}
|
||||||
|
>
|
||||||
|
{certificateExpiry}
|
||||||
|
</Typography>
|
||||||
|
}
|
||||||
|
/>
|
||||||
</Stack>
|
</Stack>
|
||||||
<Box>
|
<Box>
|
||||||
<Stack
|
<Stack
|
||||||
|
|||||||
@@ -74,7 +74,7 @@ const MonitorTable = ({ isAdmin, filter, setIsSearching, isSearching, handlePaus
|
|||||||
authToken,
|
authToken,
|
||||||
teamId: user.teamId,
|
teamId: user.teamId,
|
||||||
limit: 25,
|
limit: 25,
|
||||||
types: ["http", "ping", "docker"],
|
types: ["http", "ping", "docker", "port"],
|
||||||
status: null,
|
status: null,
|
||||||
checkOrder: "desc",
|
checkOrder: "desc",
|
||||||
normalize: true,
|
normalize: true,
|
||||||
|
|||||||
@@ -54,7 +54,7 @@ const paletteColors = {
|
|||||||
red200: "#F04438",
|
red200: "#F04438",
|
||||||
red300: "#D32F2F",
|
red300: "#D32F2F",
|
||||||
red700: "#542426",
|
red700: "#542426",
|
||||||
red800: "#301A1F",
|
red800: "#912018",
|
||||||
orange50: "#FEF8EA",
|
orange50: "#FEF8EA",
|
||||||
orange100: "#FFECBC",
|
orange100: "#FFECBC",
|
||||||
orange300: "#FDB022",
|
orange300: "#FDB022",
|
||||||
@@ -128,7 +128,7 @@ const semanticColors = {
|
|||||||
dark: paletteColors.red700,
|
dark: paletteColors.red700,
|
||||||
},
|
},
|
||||||
dark: {
|
dark: {
|
||||||
light: paletteColors.red50,
|
light: paletteColors.red800,
|
||||||
dark: paletteColors.red800,
|
dark: paletteColors.red800,
|
||||||
},
|
},
|
||||||
},
|
},
|
||||||
|
|||||||
@@ -109,6 +109,7 @@ const monitorValidation = joi.object({
|
|||||||
"string.uri": "The URL you provided is not valid.",
|
"string.uri": "The URL you provided is not valid.",
|
||||||
"string.invalidUrl": "Please enter a valid URL with optional port",
|
"string.invalidUrl": "Please enter a valid URL with optional port",
|
||||||
}),
|
}),
|
||||||
|
port: joi.number(),
|
||||||
name: joi.string().trim().max(50).allow("").messages({
|
name: joi.string().trim().max(50).allow("").messages({
|
||||||
"string.max": "This field should not exceed the 50 characters limit.",
|
"string.max": "This field should not exceed the 50 characters limit.",
|
||||||
}),
|
}),
|
||||||
|
|||||||
@@ -1,6 +1,7 @@
|
|||||||
services:
|
services:
|
||||||
client:
|
client:
|
||||||
image: uptime_client:latest
|
image: uptime_client:latest
|
||||||
|
restart: always
|
||||||
ports:
|
ports:
|
||||||
- "5173:5173"
|
- "5173:5173"
|
||||||
|
|
||||||
@@ -8,6 +9,7 @@ services:
|
|||||||
- server
|
- server
|
||||||
server:
|
server:
|
||||||
image: uptime_server:latest
|
image: uptime_server:latest
|
||||||
|
restart: always
|
||||||
ports:
|
ports:
|
||||||
- "5000:5000"
|
- "5000:5000"
|
||||||
env_file:
|
env_file:
|
||||||
@@ -17,12 +19,14 @@ services:
|
|||||||
- mongodb
|
- mongodb
|
||||||
redis:
|
redis:
|
||||||
image: uptime_redis:latest
|
image: uptime_redis:latest
|
||||||
|
restart: always
|
||||||
ports:
|
ports:
|
||||||
- "6379:6379"
|
- "6379:6379"
|
||||||
volumes:
|
volumes:
|
||||||
- ./redis/data:/data
|
- ./redis/data:/data
|
||||||
mongodb:
|
mongodb:
|
||||||
image: uptime_database_mongo:latest
|
image: uptime_database_mongo:latest
|
||||||
|
restart: always
|
||||||
command: ["mongod", "--quiet"]
|
command: ["mongod", "--quiet"]
|
||||||
ports:
|
ports:
|
||||||
- "27017:27017"
|
- "27017:27017"
|
||||||
|
|||||||
Vendored
+4
@@ -1,6 +1,7 @@
|
|||||||
services:
|
services:
|
||||||
client:
|
client:
|
||||||
image: bluewaveuptime/uptime_client:latest
|
image: bluewaveuptime/uptime_client:latest
|
||||||
|
restart: always
|
||||||
environment:
|
environment:
|
||||||
UPTIME_APP_API_BASE_URL: "http://localhost:5000/api/v1"
|
UPTIME_APP_API_BASE_URL: "http://localhost:5000/api/v1"
|
||||||
ports:
|
ports:
|
||||||
@@ -10,6 +11,7 @@ services:
|
|||||||
- server
|
- server
|
||||||
server:
|
server:
|
||||||
image: bluewaveuptime/uptime_server:latest
|
image: bluewaveuptime/uptime_server:latest
|
||||||
|
restart: always
|
||||||
ports:
|
ports:
|
||||||
- "5000:5000"
|
- "5000:5000"
|
||||||
depends_on:
|
depends_on:
|
||||||
@@ -22,12 +24,14 @@ services:
|
|||||||
# - /var/run/docker.sock:/var/run/docker.sock:ro
|
# - /var/run/docker.sock:/var/run/docker.sock:ro
|
||||||
redis:
|
redis:
|
||||||
image: bluewaveuptime/uptime_redis:latest
|
image: bluewaveuptime/uptime_redis:latest
|
||||||
|
restart: always
|
||||||
ports:
|
ports:
|
||||||
- "6379:6379"
|
- "6379:6379"
|
||||||
volumes:
|
volumes:
|
||||||
- ./redis/data:/data
|
- ./redis/data:/data
|
||||||
mongodb:
|
mongodb:
|
||||||
image: bluewaveuptime/uptime_database_mongo:latest
|
image: bluewaveuptime/uptime_database_mongo:latest
|
||||||
|
restart: always
|
||||||
volumes:
|
volumes:
|
||||||
- ./mongo/data:/data/db
|
- ./mongo/data:/data/db
|
||||||
command: ["mongod", "--quiet"]
|
command: ["mongod", "--quiet"]
|
||||||
|
|||||||
@@ -1,6 +1,7 @@
|
|||||||
services:
|
services:
|
||||||
client:
|
client:
|
||||||
image: uptime_client:latest
|
image: uptime_client:latest
|
||||||
|
restart: always
|
||||||
environment:
|
environment:
|
||||||
UPTIME_APP_API_BASE_URL: "https://checkmate-demo.bluewavelabs.ca/api/v1"
|
UPTIME_APP_API_BASE_URL: "https://checkmate-demo.bluewavelabs.ca/api/v1"
|
||||||
ports:
|
ports:
|
||||||
@@ -15,11 +16,13 @@ services:
|
|||||||
|
|
||||||
certbot:
|
certbot:
|
||||||
image: certbot/certbot:latest
|
image: certbot/certbot:latest
|
||||||
|
restart: always
|
||||||
volumes:
|
volumes:
|
||||||
- ./certbot/www/:/var/www/certbot/:rw
|
- ./certbot/www/:/var/www/certbot/:rw
|
||||||
- ./certbot/conf/:/etc/letsencrypt/:rw
|
- ./certbot/conf/:/etc/letsencrypt/:rw
|
||||||
server:
|
server:
|
||||||
image: uptime_server:latest
|
image: uptime_server:latest
|
||||||
|
restart: always
|
||||||
ports:
|
ports:
|
||||||
- "5000:5000"
|
- "5000:5000"
|
||||||
env_file:
|
env_file:
|
||||||
@@ -29,12 +32,14 @@ services:
|
|||||||
- mongodb
|
- mongodb
|
||||||
redis:
|
redis:
|
||||||
image: uptime_redis:latest
|
image: uptime_redis:latest
|
||||||
|
restart: always
|
||||||
ports:
|
ports:
|
||||||
- "6379:6379"
|
- "6379:6379"
|
||||||
volumes:
|
volumes:
|
||||||
- ./redis/data:/data
|
- ./redis/data:/data
|
||||||
mongodb:
|
mongodb:
|
||||||
image: uptime_database_mongo:latest
|
image: uptime_database_mongo:latest
|
||||||
|
restart: always
|
||||||
command: ["mongod", "--quiet", "--auth"]
|
command: ["mongod", "--quiet", "--auth"]
|
||||||
ports:
|
ports:
|
||||||
- "27017:27017"
|
- "27017:27017"
|
||||||
|
|||||||
@@ -1,8 +1,9 @@
|
|||||||
services:
|
services:
|
||||||
client:
|
client:
|
||||||
image: uptime_client:latest
|
image: uptime_client:latest
|
||||||
|
restart: always
|
||||||
environment:
|
environment:
|
||||||
UPTIME_APP_API_BASE_URL: "https://checkmate-demo.bluewavelabs.ca/api/v1"
|
UPTIME_APP_API_BASE_URL: "https://checkmate-test.bluewavelabs.ca/api/v1"
|
||||||
ports:
|
ports:
|
||||||
- "80:80"
|
- "80:80"
|
||||||
- "443:443"
|
- "443:443"
|
||||||
@@ -15,11 +16,13 @@ services:
|
|||||||
|
|
||||||
certbot:
|
certbot:
|
||||||
image: certbot/certbot:latest
|
image: certbot/certbot:latest
|
||||||
|
restart: always
|
||||||
volumes:
|
volumes:
|
||||||
- ./certbot/www/:/var/www/certbot/:rw
|
- ./certbot/www/:/var/www/certbot/:rw
|
||||||
- ./certbot/conf/:/etc/letsencrypt/:rw
|
- ./certbot/conf/:/etc/letsencrypt/:rw
|
||||||
server:
|
server:
|
||||||
image: uptime_server:latest
|
image: uptime_server:latest
|
||||||
|
restart: always
|
||||||
ports:
|
ports:
|
||||||
- "5000:5000"
|
- "5000:5000"
|
||||||
env_file:
|
env_file:
|
||||||
@@ -29,6 +32,7 @@ services:
|
|||||||
- mongodb
|
- mongodb
|
||||||
redis:
|
redis:
|
||||||
image: uptime_redis:latest
|
image: uptime_redis:latest
|
||||||
|
restart: always
|
||||||
ports:
|
ports:
|
||||||
- "6379:6379"
|
- "6379:6379"
|
||||||
volumes:
|
volumes:
|
||||||
|
|||||||
@@ -98,15 +98,16 @@ Here's how you can contribute:
|
|||||||
5. Check for good-first-issue's if you are a newcomer.
|
5. Check for good-first-issue's if you are a newcomer.
|
||||||
6. Make a pull request to add new features/make quality-of-life improvements/fix bugs.
|
6. Make a pull request to add new features/make quality-of-life improvements/fix bugs.
|
||||||
|
|
||||||
<!-- <a href="https://github.com/bluewave-labs/checkmate/graphs/contributors">
|
<a href="https://github.com/bluewave-labs/checkmate/graphs/contributors">
|
||||||
<img src="https://contrib.rocks/image?repo=bluewave-labs/checkmate" />
|
<img src="https://contrib.rocks/image?repo=bluewave-labs/checkmate" />
|
||||||
</a>
|
</a>
|
||||||
|
|
||||||
Made with [contrib.rocks](https://contrib.rocks).
|
<!--
|
||||||
-->
|
|
||||||
|
|
||||||

|

|
||||||
|
|
||||||
|
-->
|
||||||
|
|
||||||
[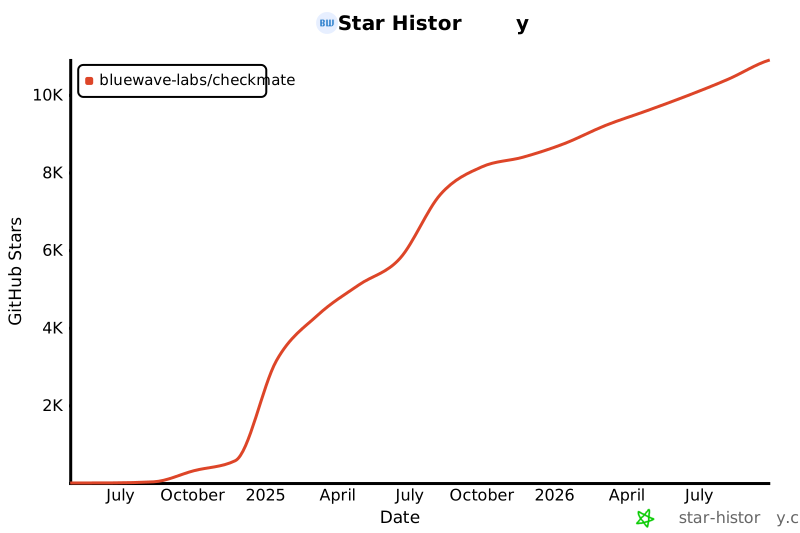](https://star-history.com/#bluewave-labs/bluewave-uptime&Date)
|
[](https://star-history.com/#bluewave-labs/bluewave-uptime&Date)
|
||||||
|
|
||||||
Also check other developer and contributor-friendly projects of BlueWave:
|
Also check other developer and contributor-friendly projects of BlueWave:
|
||||||
|
|||||||
@@ -17,500 +17,501 @@ import { handleValidationError, handleError } from "./controllerUtils.js";
|
|||||||
const SERVICE_NAME = "authController";
|
const SERVICE_NAME = "authController";
|
||||||
dotenv.config();
|
dotenv.config();
|
||||||
|
|
||||||
/**
|
class AuthController {
|
||||||
* Creates and returns JWT token with an arbitrary payload
|
constructor(db, settingsService, emailService, jobQueue) {
|
||||||
* @function
|
this.db = db;
|
||||||
* @param {Object} payload
|
this.settingsService = settingsService;
|
||||||
* @param {tokenType} typeOfToken - Whether to generate refresh token with long TTL or access token with short TTL.
|
this.emailService = emailService;
|
||||||
* @param {Object} appSettings
|
this.jobQueue = jobQueue;
|
||||||
* @returns {String}
|
|
||||||
* @throws {Error}
|
|
||||||
*/
|
|
||||||
const issueToken = (payload, typeOfToken, appSettings) => {
|
|
||||||
try {
|
|
||||||
const tokenTTL =
|
|
||||||
typeOfToken === tokenType.REFRESH_TOKEN
|
|
||||||
? (appSettings?.refreshTokenTTL ?? "7d")
|
|
||||||
: (appSettings?.jwtTTL ?? "2h");
|
|
||||||
const tokenSecret =
|
|
||||||
typeOfToken === tokenType.REFRESH_TOKEN
|
|
||||||
? appSettings?.refreshTokenSecret
|
|
||||||
: appSettings?.jwtSecret;
|
|
||||||
const payloadData = typeOfToken === tokenType.REFRESH_TOKEN ? {} : payload;
|
|
||||||
|
|
||||||
return jwt.sign(payloadData, tokenSecret, { expiresIn: tokenTTL });
|
|
||||||
} catch (error) {
|
|
||||||
throw handleError(error, SERVICE_NAME, "issueToken");
|
|
||||||
}
|
}
|
||||||
};
|
|
||||||
|
|
||||||
/**
|
/**
|
||||||
* Registers a new user. If the user is the first account, a JWT secret is created. If not, an invite token is required.
|
* Creates and returns JWT token with an arbitrary payload
|
||||||
* @async
|
* @function
|
||||||
* @param {Object} req - The Express request object.
|
* @param {Object} payload
|
||||||
* @property {Object} req.body - The body of the request.
|
* @param {tokenType} typeOfToken - Whether to generate refresh token with long TTL or access token with short TTL.
|
||||||
* @property {string} req.body.inviteToken - The invite token for registration.
|
* @param {Object} appSettings
|
||||||
* @property {Object} req.file - The file object for the user's profile image.
|
* @returns {String}
|
||||||
* @param {Object} res - The Express response object.
|
* @throws {Error}
|
||||||
* @param {function} next - The next middleware function.
|
*/
|
||||||
* @returns {Object} The response object with a success status, a message indicating the creation of the user, the created user data, and a JWT token.
|
issueToken = (payload, typeOfToken, appSettings) => {
|
||||||
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
try {
|
||||||
*/
|
const tokenTTL =
|
||||||
const registerUser = async (req, res, next) => {
|
typeOfToken === tokenType.REFRESH_TOKEN
|
||||||
// joi validation
|
? (appSettings?.refreshTokenTTL ?? "7d")
|
||||||
try {
|
: (appSettings?.jwtTTL ?? "2h");
|
||||||
await registrationBodyValidation.validateAsync(req.body);
|
const tokenSecret =
|
||||||
} catch (error) {
|
typeOfToken === tokenType.REFRESH_TOKEN
|
||||||
const validationError = handleValidationError(error, SERVICE_NAME);
|
? appSettings?.refreshTokenSecret
|
||||||
next(validationError);
|
: appSettings?.jwtSecret;
|
||||||
return;
|
const payloadData = typeOfToken === tokenType.REFRESH_TOKEN ? {} : payload;
|
||||||
}
|
|
||||||
// Create a new user
|
return jwt.sign(payloadData, tokenSecret, { expiresIn: tokenTTL });
|
||||||
try {
|
} catch (error) {
|
||||||
const { inviteToken } = req.body;
|
throw handleError(error, SERVICE_NAME, "issueToken");
|
||||||
// If superAdmin exists, a token should be attached to all further register requests
|
|
||||||
const superAdminExists = await req.db.checkSuperadmin(req, res);
|
|
||||||
if (superAdminExists) {
|
|
||||||
await req.db.getInviteTokenAndDelete(inviteToken);
|
|
||||||
} else {
|
|
||||||
// This is the first account, create JWT secret to use if one is not supplied by env
|
|
||||||
const jwtSecret = crypto.randomBytes(64).toString("hex");
|
|
||||||
await req.db.updateAppSettings({ jwtSecret });
|
|
||||||
}
|
}
|
||||||
|
};
|
||||||
|
|
||||||
const newUser = await req.db.insertUser({ ...req.body }, req.file);
|
/**
|
||||||
logger.info({
|
* Registers a new user. If the user is the first account, a JWT secret is created. If not, an invite token is required.
|
||||||
message: successMessages.AUTH_CREATE_USER,
|
* @async
|
||||||
service: SERVICE_NAME,
|
* @param {Object} req - The Express request object.
|
||||||
details: newUser._id,
|
* @property {Object} req.body - The body of the request.
|
||||||
});
|
* @property {string} req.body.inviteToken - The invite token for registration.
|
||||||
|
* @property {Object} req.file - The file object for the user's profile image.
|
||||||
|
* @param {Object} res - The Express response object.
|
||||||
|
* @param {function} next - The next middleware function.
|
||||||
|
* @returns {Object} The response object with a success status, a message indicating the creation of the user, the created user data, and a JWT token.
|
||||||
|
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
||||||
|
*/
|
||||||
|
registerUser = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await registrationBodyValidation.validateAsync(req.body);
|
||||||
|
} catch (error) {
|
||||||
|
const validationError = handleValidationError(error, SERVICE_NAME);
|
||||||
|
next(validationError);
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
// Create a new user
|
||||||
|
try {
|
||||||
|
const { inviteToken } = req.body;
|
||||||
|
// If superAdmin exists, a token should be attached to all further register requests
|
||||||
|
const superAdminExists = await this.db.checkSuperadmin(req, res);
|
||||||
|
if (superAdminExists) {
|
||||||
|
await this.db.getInviteTokenAndDelete(inviteToken);
|
||||||
|
} else {
|
||||||
|
// This is the first account, create JWT secret to use if one is not supplied by env
|
||||||
|
const jwtSecret = crypto.randomBytes(64).toString("hex");
|
||||||
|
await this.db.updateAppSettings({ jwtSecret });
|
||||||
|
}
|
||||||
|
|
||||||
const userForToken = { ...newUser._doc };
|
const newUser = await this.db.insertUser({ ...req.body }, req.file);
|
||||||
delete userForToken.profileImage;
|
logger.info({
|
||||||
delete userForToken.avatarImage;
|
message: successMessages.AUTH_CREATE_USER,
|
||||||
|
service: SERVICE_NAME,
|
||||||
const appSettings = await req.settingsService.getSettings();
|
details: newUser._id,
|
||||||
|
|
||||||
const token = issueToken(userForToken, tokenType.ACCESS_TOKEN, appSettings);
|
|
||||||
const refreshToken = issueToken({}, tokenType.REFRESH_TOKEN, appSettings);
|
|
||||||
|
|
||||||
req.emailService
|
|
||||||
.buildAndSendEmail(
|
|
||||||
"welcomeEmailTemplate",
|
|
||||||
{ name: newUser.firstName },
|
|
||||||
newUser.email,
|
|
||||||
"Welcome to Uptime Monitor"
|
|
||||||
)
|
|
||||||
.catch((error) => {
|
|
||||||
logger.error({
|
|
||||||
message: error.message,
|
|
||||||
service: SERVICE_NAME,
|
|
||||||
method: "registerUser",
|
|
||||||
stack: error.stack,
|
|
||||||
});
|
|
||||||
});
|
});
|
||||||
|
|
||||||
return res.status(200).json({
|
const userForToken = { ...newUser._doc };
|
||||||
success: true,
|
delete userForToken.profileImage;
|
||||||
msg: successMessages.AUTH_CREATE_USER,
|
delete userForToken.avatarImage;
|
||||||
data: { user: newUser, token: token, refreshToken: refreshToken },
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "registerController"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
/**
|
const appSettings = await this.settingsService.getSettings();
|
||||||
* Logs in a user by validating the user's credentials and issuing a JWT token.
|
|
||||||
* @async
|
|
||||||
* @param {Object} req - The Express request object.
|
|
||||||
* @property {Object} req.body - The body of the request.
|
|
||||||
* @property {string} req.body.email - The email of the user.
|
|
||||||
* @property {string} req.body.password - The password of the user.
|
|
||||||
* @param {Object} res - The Express response object.
|
|
||||||
* @param {function} next - The next middleware function.
|
|
||||||
* @returns {Object} The response object with a success status, a message indicating the login of the user, the user data (without password and avatar image), and a JWT token.
|
|
||||||
* @throws {Error} If there is an error during the process, especially if there is a validation error (422) or the password is incorrect.
|
|
||||||
*/
|
|
||||||
const loginUser = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
await loginValidation.validateAsync(req.body);
|
|
||||||
} catch (error) {
|
|
||||||
const validationError = handleValidationError(error, SERVICE_NAME);
|
|
||||||
next(validationError);
|
|
||||||
return;
|
|
||||||
}
|
|
||||||
try {
|
|
||||||
const { email, password } = req.body;
|
|
||||||
|
|
||||||
// Check if user exists
|
const token = this.issueToken(userForToken, tokenType.ACCESS_TOKEN, appSettings);
|
||||||
const user = await req.db.getUserByEmail(email);
|
const refreshToken = this.issueToken({}, tokenType.REFRESH_TOKEN, appSettings);
|
||||||
|
|
||||||
// Compare password
|
this.emailService
|
||||||
const match = await user.comparePassword(password);
|
.buildAndSendEmail(
|
||||||
if (match !== true) {
|
"welcomeEmailTemplate",
|
||||||
next(new Error(errorMessages.AUTH_INCORRECT_PASSWORD));
|
{ name: newUser.firstName },
|
||||||
|
newUser.email,
|
||||||
|
"Welcome to Uptime Monitor"
|
||||||
|
)
|
||||||
|
.catch((error) => {
|
||||||
|
logger.error({
|
||||||
|
message: error.message,
|
||||||
|
service: SERVICE_NAME,
|
||||||
|
method: "registerUser",
|
||||||
|
stack: error.stack,
|
||||||
|
});
|
||||||
|
});
|
||||||
|
|
||||||
|
return res.status(200).json({
|
||||||
|
success: true,
|
||||||
|
msg: successMessages.AUTH_CREATE_USER,
|
||||||
|
data: { user: newUser, token: token, refreshToken: refreshToken },
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "registerController"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
|
/**
|
||||||
|
* Logs in a user by validating the user's credentials and issuing a JWT token.
|
||||||
|
* @async
|
||||||
|
* @param {Object} req - The Express request object.
|
||||||
|
* @property {Object} req.body - The body of the request.
|
||||||
|
* @property {string} req.body.email - The email of the user.
|
||||||
|
* @property {string} req.body.password - The password of the user.
|
||||||
|
* @param {Object} res - The Express response object.
|
||||||
|
* @param {function} next - The next middleware function.
|
||||||
|
* @returns {Object} The response object with a success status, a message indicating the login of the user, the user data (without password and avatar image), and a JWT token.
|
||||||
|
* @throws {Error} If there is an error during the process, especially if there is a validation error (422) or the password is incorrect.
|
||||||
|
*/
|
||||||
|
loginUser = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await loginValidation.validateAsync(req.body);
|
||||||
|
} catch (error) {
|
||||||
|
const validationError = handleValidationError(error, SERVICE_NAME);
|
||||||
|
next(validationError);
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
try {
|
||||||
|
const { email, password } = req.body;
|
||||||
|
|
||||||
|
// Check if user exists
|
||||||
|
const user = await this.db.getUserByEmail(email);
|
||||||
|
|
||||||
|
// Compare password
|
||||||
|
const match = await user.comparePassword(password);
|
||||||
|
if (match !== true) {
|
||||||
|
next(new Error(errorMessages.AUTH_INCORRECT_PASSWORD));
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
|
||||||
|
// Remove password from user object. Should this be abstracted to DB layer?
|
||||||
|
const userWithoutPassword = { ...user._doc };
|
||||||
|
delete userWithoutPassword.password;
|
||||||
|
delete userWithoutPassword.avatarImage;
|
||||||
|
|
||||||
|
// Happy path, return token
|
||||||
|
const appSettings = await this.settingsService.getSettings();
|
||||||
|
const token = this.issueToken(
|
||||||
|
userWithoutPassword,
|
||||||
|
tokenType.ACCESS_TOKEN,
|
||||||
|
appSettings
|
||||||
|
);
|
||||||
|
const refreshToken = this.issueToken({}, tokenType.REFRESH_TOKEN, appSettings);
|
||||||
|
// reset avatar image
|
||||||
|
userWithoutPassword.avatarImage = user.avatarImage;
|
||||||
|
|
||||||
|
return res.status(200).json({
|
||||||
|
success: true,
|
||||||
|
msg: successMessages.AUTH_LOGIN_USER,
|
||||||
|
data: { user: userWithoutPassword, token: token, refreshToken: refreshToken },
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "loginUser"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
|
/**
|
||||||
|
* Generates new auth token if the refresh token is valid
|
||||||
|
* @async
|
||||||
|
* @param {Express.Request} req - The Express request object.
|
||||||
|
* @property {Object} req.headers - The parameter of the request.
|
||||||
|
* @param {Express.Response} res - The Express response object.
|
||||||
|
* @param {function} next - The next middleware function.
|
||||||
|
* @returns {Object} The response object with a success status, a message indicating new auth token is generated.
|
||||||
|
* @throws {Error} If there is an error during the process such as any of the token is not received
|
||||||
|
*/
|
||||||
|
refreshAuthToken = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
// check for refreshToken
|
||||||
|
const refreshToken = req.headers["x-refresh-token"];
|
||||||
|
|
||||||
|
if (!refreshToken) {
|
||||||
|
// No refresh token provided
|
||||||
|
const error = new Error(errorMessages.NO_REFRESH_TOKEN);
|
||||||
|
error.status = 401;
|
||||||
|
error.service = SERVICE_NAME;
|
||||||
|
error.method = "refreshAuthToken";
|
||||||
|
return next(error);
|
||||||
|
}
|
||||||
|
|
||||||
|
// Verify refresh token
|
||||||
|
const appSettings = await this.settingsService.getSettings();
|
||||||
|
const { refreshTokenSecret } = appSettings;
|
||||||
|
jwt.verify(refreshToken, refreshTokenSecret, async (refreshErr, refreshDecoded) => {
|
||||||
|
if (refreshErr) {
|
||||||
|
// Invalid or expired refresh token, trigger logout
|
||||||
|
const errorMessage =
|
||||||
|
refreshErr.name === "TokenExpiredError"
|
||||||
|
? errorMessages.EXPIRED_REFRESH_TOKEN
|
||||||
|
: errorMessages.INVALID_REFRESH_TOKEN;
|
||||||
|
const error = new Error(errorMessage);
|
||||||
|
error.status = 401;
|
||||||
|
error.service = SERVICE_NAME;
|
||||||
|
return next(error);
|
||||||
|
}
|
||||||
|
});
|
||||||
|
// Refresh token is valid and unexpired, generate new access token
|
||||||
|
const oldAuthToken = getTokenFromHeaders(req.headers);
|
||||||
|
const { jwtSecret } = await this.settingsService.getSettings();
|
||||||
|
const payloadData = jwt.verify(oldAuthToken, jwtSecret, { ignoreExpiration: true });
|
||||||
|
// delete old token related data
|
||||||
|
delete payloadData.iat;
|
||||||
|
delete payloadData.exp;
|
||||||
|
const newAuthToken = this.issueToken(
|
||||||
|
payloadData,
|
||||||
|
tokenType.ACCESS_TOKEN,
|
||||||
|
appSettings
|
||||||
|
);
|
||||||
|
|
||||||
|
return res.status(200).json({
|
||||||
|
success: true,
|
||||||
|
msg: successMessages.AUTH_TOKEN_REFRESHED,
|
||||||
|
data: { user: payloadData, token: newAuthToken, refreshToken: refreshToken },
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "refreshAuthToken"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
/**
|
||||||
|
* Edits a user's information. If the user wants to change their password, the current password is checked before updating to the new password.
|
||||||
|
* @async
|
||||||
|
* @param {Object} req - The Express request object.
|
||||||
|
* @property {Object} req.params - The parameters of the request.
|
||||||
|
* @property {string} req.params.userId - The ID of the user to be edited.
|
||||||
|
* @property {Object} req.body - The body of the request.
|
||||||
|
* @property {string} req.body.password - The current password of the user.
|
||||||
|
* @property {string} req.body.newPassword - The new password of the user.
|
||||||
|
* @param {Object} res - The Express response object.
|
||||||
|
* @param {function} next - The next middleware function.
|
||||||
|
* @returns {Object} The response object with a success status, a message indicating the update of the user, and the updated user data.
|
||||||
|
* @throws {Error} If there is an error during the process, especially if there is a validation error (422), the user is unauthorized (401), or the password is incorrect (403).
|
||||||
|
*/
|
||||||
|
editUser = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await editUserParamValidation.validateAsync(req.params);
|
||||||
|
await editUserBodyValidation.validateAsync(req.body);
|
||||||
|
} catch (error) {
|
||||||
|
const validationError = handleValidationError(error, SERVICE_NAME);
|
||||||
|
next(validationError);
|
||||||
return;
|
return;
|
||||||
}
|
}
|
||||||
|
|
||||||
// Remove password from user object. Should this be abstracted to DB layer?
|
// TODO is this neccessary any longer? Verify ownership middleware should handle this
|
||||||
const userWithoutPassword = { ...user._doc };
|
if (req.params.userId !== req.user._id.toString()) {
|
||||||
delete userWithoutPassword.password;
|
const error = new Error(errorMessages.AUTH_UNAUTHORIZED);
|
||||||
delete userWithoutPassword.avatarImage;
|
|
||||||
|
|
||||||
// Happy path, return token
|
|
||||||
const appSettings = await req.settingsService.getSettings();
|
|
||||||
const token = issueToken(userWithoutPassword, tokenType.ACCESS_TOKEN, appSettings);
|
|
||||||
const refreshToken = issueToken({}, tokenType.REFRESH_TOKEN, appSettings);
|
|
||||||
// reset avatar image
|
|
||||||
userWithoutPassword.avatarImage = user.avatarImage;
|
|
||||||
|
|
||||||
return res.status(200).json({
|
|
||||||
success: true,
|
|
||||||
msg: successMessages.AUTH_LOGIN_USER,
|
|
||||||
data: { user: userWithoutPassword, token: token, refreshToken: refreshToken },
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "loginUser"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
/**
|
|
||||||
* Generates new auth token if the refresh token is valid
|
|
||||||
* @async
|
|
||||||
* @param {Express.Request} req - The Express request object.
|
|
||||||
* @property {Object} req.headers - The parameter of the request.
|
|
||||||
* @param {Express.Response} res - The Express response object.
|
|
||||||
* @param {function} next - The next middleware function.
|
|
||||||
* @returns {Object} The response object with a success status, a message indicating new auth token is generated.
|
|
||||||
* @throws {Error} If there is an error during the process such as any of the token is not received
|
|
||||||
*/
|
|
||||||
const refreshAuthToken = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
// check for refreshToken
|
|
||||||
const refreshToken = req.headers["x-refresh-token"];
|
|
||||||
|
|
||||||
if (!refreshToken) {
|
|
||||||
// No refresh token provided
|
|
||||||
const error = new Error(errorMessages.NO_REFRESH_TOKEN);
|
|
||||||
error.status = 401;
|
error.status = 401;
|
||||||
error.service = SERVICE_NAME;
|
error.service = SERVICE_NAME;
|
||||||
error.method = "refreshAuthToken";
|
next(error);
|
||||||
return next(error);
|
return;
|
||||||
}
|
}
|
||||||
|
|
||||||
// Verify refresh token
|
try {
|
||||||
const appSettings = await req.settingsService.getSettings();
|
// Change Password check
|
||||||
const { refreshTokenSecret } = appSettings;
|
if (req.body.password && req.body.newPassword) {
|
||||||
jwt.verify(refreshToken, refreshTokenSecret, async (refreshErr, refreshDecoded) => {
|
// Get token from headers
|
||||||
if (refreshErr) {
|
const token = getTokenFromHeaders(req.headers);
|
||||||
// Invalid or expired refresh token, trigger logout
|
// Get email from token
|
||||||
const errorMessage =
|
const { jwtSecret } = this.settingsService.getSettings();
|
||||||
refreshErr.name === "TokenExpiredError"
|
const { email } = jwt.verify(token, jwtSecret);
|
||||||
? errorMessages.EXPIRED_REFRESH_TOKEN
|
// Add user email to body for DB operation
|
||||||
: errorMessages.INVALID_REFRESH_TOKEN;
|
req.body.email = email;
|
||||||
const error = new Error(errorMessage);
|
// Get user
|
||||||
error.status = 401;
|
const user = await this.db.getUserByEmail(email);
|
||||||
error.service = SERVICE_NAME;
|
// Compare passwords
|
||||||
return next(error);
|
const match = await user.comparePassword(req.body.password);
|
||||||
|
// If not a match, throw a 403
|
||||||
|
// 403 instead of 401 to avoid triggering axios interceptor
|
||||||
|
if (!match) {
|
||||||
|
const error = new Error(errorMessages.AUTH_INCORRECT_PASSWORD);
|
||||||
|
error.status = 403;
|
||||||
|
next(error);
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
// If a match, update the password
|
||||||
|
req.body.password = req.body.newPassword;
|
||||||
}
|
}
|
||||||
});
|
|
||||||
// Refresh token is valid and unexpired, generate new access token
|
|
||||||
const oldAuthToken = getTokenFromHeaders(req.headers);
|
|
||||||
const { jwtSecret } = await req.settingsService.getSettings();
|
|
||||||
const payloadData = jwt.verify(oldAuthToken, jwtSecret, { ignoreExpiration: true });
|
|
||||||
// delete old token related data
|
|
||||||
delete payloadData.iat;
|
|
||||||
delete payloadData.exp;
|
|
||||||
const newAuthToken = issueToken(payloadData, tokenType.ACCESS_TOKEN, appSettings);
|
|
||||||
|
|
||||||
return res.status(200).json({
|
const updatedUser = await this.db.updateUser(req, res);
|
||||||
success: true,
|
return res.status(200).json({
|
||||||
msg: successMessages.AUTH_TOKEN_REFRESHED,
|
success: true,
|
||||||
data: { user: payloadData, token: newAuthToken, refreshToken: refreshToken },
|
msg: successMessages.AUTH_UPDATE_USER,
|
||||||
});
|
data: updatedUser,
|
||||||
} catch (error) {
|
});
|
||||||
next(handleError(error, SERVICE_NAME, "refreshAuthToken"));
|
} catch (error) {
|
||||||
}
|
next(handleError(error, SERVICE_NAME, "userEditController"));
|
||||||
};
|
}
|
||||||
|
};
|
||||||
|
|
||||||
/**
|
/**
|
||||||
* Edits a user's information. If the user wants to change their password, the current password is checked before updating to the new password.
|
* Checks if a superadmin account exists in the database.
|
||||||
* @async
|
* @async
|
||||||
* @param {Object} req - The Express request object.
|
* @param {Object} req - The Express request object.
|
||||||
* @property {Object} req.params - The parameters of the request.
|
* @param {Object} res - The Express response object.
|
||||||
* @property {string} req.params.userId - The ID of the user to be edited.
|
* @param {function} next - The next middleware function.
|
||||||
* @property {Object} req.body - The body of the request.
|
* @returns {Object} The response object with a success status, a message indicating the existence of a superadmin, and a boolean indicating the existence of a superadmin.
|
||||||
* @property {string} req.body.password - The current password of the user.
|
* @throws {Error} If there is an error during the process.
|
||||||
* @property {string} req.body.newPassword - The new password of the user.
|
*/
|
||||||
* @param {Object} res - The Express response object.
|
checkSuperadminExists = async (req, res, next) => {
|
||||||
* @param {function} next - The next middleware function.
|
try {
|
||||||
* @returns {Object} The response object with a success status, a message indicating the update of the user, and the updated user data.
|
const superAdminExists = await this.db.checkSuperadmin(req, res);
|
||||||
* @throws {Error} If there is an error during the process, especially if there is a validation error (422), the user is unauthorized (401), or the password is incorrect (403).
|
return res.status(200).json({
|
||||||
*/
|
success: true,
|
||||||
const editUser = async (req, res, next) => {
|
msg: successMessages.AUTH_ADMIN_EXISTS,
|
||||||
try {
|
data: superAdminExists,
|
||||||
await editUserParamValidation.validateAsync(req.params);
|
});
|
||||||
await editUserBodyValidation.validateAsync(req.body);
|
} catch (error) {
|
||||||
} catch (error) {
|
next(handleError(error, SERVICE_NAME, "checkSuperadminController"));
|
||||||
const validationError = handleValidationError(error, SERVICE_NAME);
|
}
|
||||||
next(validationError);
|
};
|
||||||
return;
|
/**
|
||||||
}
|
* Requests a recovery token for a user. The user's email is validated and a recovery token is created and sent via email.
|
||||||
|
* @async
|
||||||
// TODO is this neccessary any longer? Verify ownership middleware should handle this
|
* @param {Object} req - The Express request object.
|
||||||
if (req.params.userId !== req.user._id.toString()) {
|
* @property {Object} req.body - The body of the request.
|
||||||
const error = new Error(errorMessages.AUTH_UNAUTHORIZED);
|
* @property {string} req.body.email - The email of the user requesting recovery.
|
||||||
error.status = 401;
|
* @param {Object} res - The Express response object.
|
||||||
error.service = SERVICE_NAME;
|
* @param {function} next - The next middleware function.
|
||||||
next(error);
|
* @returns {Object} The response object with a success status, a message indicating the creation of the recovery token, and the message ID of the sent email.
|
||||||
return;
|
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
||||||
}
|
*/
|
||||||
|
requestRecovery = async (req, res, next) => {
|
||||||
try {
|
try {
|
||||||
// Change Password check
|
await recoveryValidation.validateAsync(req.body);
|
||||||
if (req.body.password && req.body.newPassword) {
|
} catch (error) {
|
||||||
// Get token from headers
|
const validationError = handleValidationError(error, SERVICE_NAME);
|
||||||
const token = getTokenFromHeaders(req.headers);
|
next(validationError);
|
||||||
// Get email from token
|
return;
|
||||||
const { jwtSecret } = req.settingsService.getSettings();
|
|
||||||
const { email } = jwt.verify(token, jwtSecret);
|
|
||||||
// Add user email to body for DB operation
|
|
||||||
req.body.email = email;
|
|
||||||
// Get user
|
|
||||||
const user = await req.db.getUserByEmail(email);
|
|
||||||
// Compare passwords
|
|
||||||
const match = await user.comparePassword(req.body.password);
|
|
||||||
// If not a match, throw a 403
|
|
||||||
// 403 instead of 401 to avoid triggering axios interceptor
|
|
||||||
if (!match) {
|
|
||||||
const error = new Error(errorMessages.AUTH_INCORRECT_PASSWORD);
|
|
||||||
error.status = 403;
|
|
||||||
next(error);
|
|
||||||
return;
|
|
||||||
}
|
|
||||||
// If a match, update the password
|
|
||||||
req.body.password = req.body.newPassword;
|
|
||||||
}
|
}
|
||||||
|
|
||||||
const updatedUser = await req.db.updateUser(req, res);
|
try {
|
||||||
return res.status(200).json({
|
const { email } = req.body;
|
||||||
success: true,
|
const user = await this.db.getUserByEmail(email);
|
||||||
msg: successMessages.AUTH_UPDATE_USER,
|
const recoveryToken = await this.db.requestRecoveryToken(req, res);
|
||||||
data: updatedUser,
|
const name = user.firstName;
|
||||||
});
|
const { clientHost } = this.settingsService.getSettings();
|
||||||
} catch (error) {
|
const url = `${clientHost}/set-new-password/${recoveryToken.token}`;
|
||||||
next(handleError(error, SERVICE_NAME, "userEditController"));
|
const msgId = await this.emailService.buildAndSendEmail(
|
||||||
}
|
"passwordResetTemplate",
|
||||||
};
|
{
|
||||||
|
name,
|
||||||
/**
|
email,
|
||||||
* Checks if a superadmin account exists in the database.
|
url,
|
||||||
* @async
|
},
|
||||||
* @param {Object} req - The Express request object.
|
|
||||||
* @param {Object} res - The Express response object.
|
|
||||||
* @param {function} next - The next middleware function.
|
|
||||||
* @returns {Object} The response object with a success status, a message indicating the existence of a superadmin, and a boolean indicating the existence of a superadmin.
|
|
||||||
* @throws {Error} If there is an error during the process.
|
|
||||||
*/
|
|
||||||
const checkSuperadminExists = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
const superAdminExists = await req.db.checkSuperadmin(req, res);
|
|
||||||
return res.status(200).json({
|
|
||||||
success: true,
|
|
||||||
msg: successMessages.AUTH_ADMIN_EXISTS,
|
|
||||||
data: superAdminExists,
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "checkSuperadminController"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
/**
|
|
||||||
* Requests a recovery token for a user. The user's email is validated and a recovery token is created and sent via email.
|
|
||||||
* @async
|
|
||||||
* @param {Object} req - The Express request object.
|
|
||||||
* @property {Object} req.body - The body of the request.
|
|
||||||
* @property {string} req.body.email - The email of the user requesting recovery.
|
|
||||||
* @param {Object} res - The Express response object.
|
|
||||||
* @param {function} next - The next middleware function.
|
|
||||||
* @returns {Object} The response object with a success status, a message indicating the creation of the recovery token, and the message ID of the sent email.
|
|
||||||
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
|
||||||
*/
|
|
||||||
const requestRecovery = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
await recoveryValidation.validateAsync(req.body);
|
|
||||||
} catch (error) {
|
|
||||||
const validationError = handleValidationError(error, SERVICE_NAME);
|
|
||||||
next(validationError);
|
|
||||||
return;
|
|
||||||
}
|
|
||||||
|
|
||||||
try {
|
|
||||||
const { email } = req.body;
|
|
||||||
const user = await req.db.getUserByEmail(email);
|
|
||||||
const recoveryToken = await req.db.requestRecoveryToken(req, res);
|
|
||||||
const name = user.firstName;
|
|
||||||
const { clientHost } = req.settingsService.getSettings();
|
|
||||||
const url = `${clientHost}/set-new-password/${recoveryToken.token}`;
|
|
||||||
const msgId = await req.emailService.buildAndSendEmail(
|
|
||||||
"passwordResetTemplate",
|
|
||||||
{
|
|
||||||
name,
|
|
||||||
email,
|
email,
|
||||||
url,
|
"Checkmate Password Reset"
|
||||||
},
|
);
|
||||||
email,
|
|
||||||
"Checkmate Password Reset"
|
|
||||||
);
|
|
||||||
|
|
||||||
return res.status(200).json({
|
return res.status(200).json({
|
||||||
success: true,
|
success: true,
|
||||||
msg: successMessages.AUTH_CREATE_RECOVERY_TOKEN,
|
msg: successMessages.AUTH_CREATE_RECOVERY_TOKEN,
|
||||||
data: msgId,
|
data: msgId,
|
||||||
});
|
});
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleError(error, SERVICE_NAME, "recoveryRequestController"));
|
next(handleError(error, SERVICE_NAME, "recoveryRequestController"));
|
||||||
}
|
}
|
||||||
};
|
};
|
||||||
|
/**
|
||||||
/**
|
* Validates a recovery token. The recovery token is validated and if valid, a success message is returned.
|
||||||
* Validates a recovery token. The recovery token is validated and if valid, a success message is returned.
|
* @async
|
||||||
* @async
|
* @param {Object} req - The Express request object.
|
||||||
* @param {Object} req - The Express request object.
|
* @property {Object} req.body - The body of the request.
|
||||||
* @property {Object} req.body - The body of the request.
|
* @property {string} req.body.token - The recovery token to be validated.
|
||||||
* @property {string} req.body.token - The recovery token to be validated.
|
* @param {Object} res - The Express response object.
|
||||||
* @param {Object} res - The Express response object.
|
* @param {function} next - The next middleware function.
|
||||||
* @param {function} next - The next middleware function.
|
* @returns {Object} The response object with a success status and a message indicating the validation of the recovery token.
|
||||||
* @returns {Object} The response object with a success status and a message indicating the validation of the recovery token.
|
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
||||||
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
*/
|
||||||
*/
|
validateRecovery = async (req, res, next) => {
|
||||||
const validateRecovery = async (req, res, next) => {
|
try {
|
||||||
try {
|
await recoveryTokenValidation.validateAsync(req.body);
|
||||||
await recoveryTokenValidation.validateAsync(req.body);
|
} catch (error) {
|
||||||
} catch (error) {
|
const validationError = handleValidationError(error, SERVICE_NAME);
|
||||||
const validationError = handleValidationError(error, SERVICE_NAME);
|
next(validationError);
|
||||||
next(validationError);
|
return;
|
||||||
return;
|
|
||||||
}
|
|
||||||
|
|
||||||
try {
|
|
||||||
await req.db.validateRecoveryToken(req, res);
|
|
||||||
return res.status(200).json({
|
|
||||||
success: true,
|
|
||||||
msg: successMessages.AUTH_VERIFY_RECOVERY_TOKEN,
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "validateRecoveryTokenController"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
/**
|
|
||||||
* Resets a user's password. The new password is validated and if valid, the user's password is updated in the database and a new JWT token is issued.
|
|
||||||
* @async
|
|
||||||
* @param {Object} req - The Express request object.
|
|
||||||
* @property {Object} req.body - The body of the request.
|
|
||||||
* @property {string} req.body.token - The recovery token.
|
|
||||||
* @property {string} req.body.password - The new password of the user.
|
|
||||||
* @param {Object} res - The Express response object.
|
|
||||||
* @param {function} next - The next middleware function.
|
|
||||||
* @returns {Object} The response object with a success status, a message indicating the reset of the password, the updated user data (without password and avatar image), and a new JWT token.
|
|
||||||
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
|
||||||
*/
|
|
||||||
const resetPassword = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
await newPasswordValidation.validateAsync(req.body);
|
|
||||||
} catch (error) {
|
|
||||||
const validationError = handleValidationError(error, SERVICE_NAME);
|
|
||||||
next(validationError);
|
|
||||||
return;
|
|
||||||
}
|
|
||||||
try {
|
|
||||||
const user = await req.db.resetPassword(req, res);
|
|
||||||
const appSettings = await req.settingsService.getSettings();
|
|
||||||
const token = issueToken(user._doc, tokenType.ACCESS_TOKEN, appSettings);
|
|
||||||
res.status(200).json({
|
|
||||||
success: true,
|
|
||||||
msg: successMessages.AUTH_RESET_PASSWORD,
|
|
||||||
data: { user, token },
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "resetPasswordController"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
/**
|
|
||||||
* Deletes a user and all associated monitors, checks, and alerts.
|
|
||||||
*
|
|
||||||
* @param {Object} req - The request object.
|
|
||||||
* @param {Object} res - The response object.
|
|
||||||
* @param {Function} next - The next middleware function.
|
|
||||||
* @returns {Object} The response object with success status and message.
|
|
||||||
* @throws {Error} If user validation fails or user is not found in the database.
|
|
||||||
*/
|
|
||||||
const deleteUser = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
const token = getTokenFromHeaders(req.headers);
|
|
||||||
const decodedToken = jwt.decode(token);
|
|
||||||
const { email } = decodedToken;
|
|
||||||
|
|
||||||
// Check if the user exists
|
|
||||||
const user = await req.db.getUserByEmail(email);
|
|
||||||
// 1. Find all the monitors associated with the team ID if superadmin
|
|
||||||
|
|
||||||
const result = await req.db.getMonitorsByTeamId({
|
|
||||||
params: { teamId: user.teamId },
|
|
||||||
});
|
|
||||||
|
|
||||||
if (user.role.includes("superadmin")) {
|
|
||||||
//2. Remove all jobs, delete checks and alerts
|
|
||||||
result?.monitors.length > 0 &&
|
|
||||||
(await Promise.all(
|
|
||||||
result.monitors.map(async (monitor) => {
|
|
||||||
await req.jobQueue.deleteJob(monitor);
|
|
||||||
await req.db.deleteChecks(monitor._id);
|
|
||||||
await req.db.deletePageSpeedChecksByMonitorId(monitor._id);
|
|
||||||
await req.db.deleteNotificationsByMonitorId(monitor._id);
|
|
||||||
})
|
|
||||||
));
|
|
||||||
|
|
||||||
// 3. Delete team
|
|
||||||
await req.db.deleteTeam(user.teamId);
|
|
||||||
// 4. Delete all other team members
|
|
||||||
await req.db.deleteAllOtherUsers();
|
|
||||||
// 5. Delete each monitor
|
|
||||||
await req.db.deleteMonitorsByUserId(user._id);
|
|
||||||
}
|
}
|
||||||
// 6. Delete the user by id
|
|
||||||
await req.db.deleteUser(user._id);
|
|
||||||
return res.status(200).json({
|
|
||||||
success: true,
|
|
||||||
msg: successMessages.AUTH_DELETE_USER,
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "deleteUserController"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
const getAllUsers = async (req, res, next) => {
|
try {
|
||||||
try {
|
await this.db.validateRecoveryToken(req, res);
|
||||||
const allUsers = await req.db.getAllUsers(req, res);
|
return res.status(200).json({
|
||||||
res.status(200).json({ success: true, msg: "Got all users", data: allUsers });
|
success: true,
|
||||||
} catch (error) {
|
msg: successMessages.AUTH_VERIFY_RECOVERY_TOKEN,
|
||||||
next(handleError(error, SERVICE_NAME, "getAllUsersController"));
|
});
|
||||||
}
|
} catch (error) {
|
||||||
};
|
next(handleError(error, SERVICE_NAME, "validateRecoveryTokenController"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
export {
|
/**
|
||||||
issueToken,
|
* Resets a user's password. The new password is validated and if valid, the user's password is updated in the database and a new JWT token is issued.
|
||||||
registerUser,
|
* @async
|
||||||
loginUser,
|
* @param {Object} req - The Express request object.
|
||||||
refreshAuthToken,
|
* @property {Object} req.body - The body of the request.
|
||||||
editUser,
|
* @property {string} req.body.token - The recovery token.
|
||||||
checkSuperadminExists,
|
* @property {string} req.body.password - The new password of the user.
|
||||||
requestRecovery,
|
* @param {Object} res - The Express response object.
|
||||||
validateRecovery,
|
* @param {function} next - The next middleware function.
|
||||||
resetPassword,
|
* @returns {Object} The response object with a success status, a message indicating the reset of the password, the updated user data (without password and avatar image), and a new JWT token.
|
||||||
deleteUser,
|
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
||||||
getAllUsers,
|
*/
|
||||||
};
|
resetPassword = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await newPasswordValidation.validateAsync(req.body);
|
||||||
|
} catch (error) {
|
||||||
|
const validationError = handleValidationError(error, SERVICE_NAME);
|
||||||
|
next(validationError);
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
try {
|
||||||
|
const user = await this.db.resetPassword(req, res);
|
||||||
|
const appSettings = await this.settingsService.getSettings();
|
||||||
|
const token = this.issueToken(user._doc, tokenType.ACCESS_TOKEN, appSettings);
|
||||||
|
res.status(200).json({
|
||||||
|
success: true,
|
||||||
|
msg: successMessages.AUTH_RESET_PASSWORD,
|
||||||
|
data: { user, token },
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "resetPasswordController"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
|
/**
|
||||||
|
* Deletes a user and all associated monitors, checks, and alerts.
|
||||||
|
*
|
||||||
|
* @param {Object} req - The request object.
|
||||||
|
* @param {Object} res - The response object.
|
||||||
|
* @param {Function} next - The next middleware function.
|
||||||
|
* @returns {Object} The response object with success status and message.
|
||||||
|
* @throws {Error} If user validation fails or user is not found in the database.
|
||||||
|
*/
|
||||||
|
deleteUser = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
const token = getTokenFromHeaders(req.headers);
|
||||||
|
const decodedToken = jwt.decode(token);
|
||||||
|
const { email } = decodedToken;
|
||||||
|
|
||||||
|
// Check if the user exists
|
||||||
|
const user = await this.db.getUserByEmail(email);
|
||||||
|
// 1. Find all the monitors associated with the team ID if superadmin
|
||||||
|
|
||||||
|
const result = await this.db.getMonitorsByTeamId({
|
||||||
|
params: { teamId: user.teamId },
|
||||||
|
});
|
||||||
|
|
||||||
|
if (user.role.includes("superadmin")) {
|
||||||
|
//2. Remove all jobs, delete checks and alerts
|
||||||
|
result?.monitors.length > 0 &&
|
||||||
|
(await Promise.all(
|
||||||
|
result.monitors.map(async (monitor) => {
|
||||||
|
await this.jobQueue.deleteJob(monitor);
|
||||||
|
await this.db.deleteChecks(monitor._id);
|
||||||
|
await this.db.deletePageSpeedChecksByMonitorId(monitor._id);
|
||||||
|
await this.db.deleteNotificationsByMonitorId(monitor._id);
|
||||||
|
})
|
||||||
|
));
|
||||||
|
|
||||||
|
// 3. Delete team
|
||||||
|
await this.db.deleteTeam(user.teamId);
|
||||||
|
// 4. Delete all other team members
|
||||||
|
await this.db.deleteAllOtherUsers();
|
||||||
|
// 5. Delete each monitor
|
||||||
|
await this.db.deleteMonitorsByUserId(user._id);
|
||||||
|
}
|
||||||
|
// 6. Delete the user by id
|
||||||
|
await this.db.deleteUser(user._id);
|
||||||
|
return res.status(200).json({
|
||||||
|
success: true,
|
||||||
|
msg: successMessages.AUTH_DELETE_USER,
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "deleteUserController"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
|
getAllUsers = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
const allUsers = await this.db.getAllUsers(req, res);
|
||||||
|
res.status(200).json({ success: true, msg: "Got all users", data: allUsers });
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "getAllUsersController"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
}
|
||||||
|
|
||||||
|
export default AuthController;
|
||||||
@@ -16,139 +16,138 @@ import { handleValidationError, handleError } from "./controllerUtils.js";
|
|||||||
|
|
||||||
const SERVICE_NAME = "checkController";
|
const SERVICE_NAME = "checkController";
|
||||||
|
|
||||||
const createCheck = async (req, res, next) => {
|
class CheckController {
|
||||||
try {
|
constructor(db, settingsService) {
|
||||||
await createCheckParamValidation.validateAsync(req.params);
|
this.db = db;
|
||||||
await createCheckBodyValidation.validateAsync(req.body);
|
this.settingsService = settingsService;
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
}
|
||||||
|
|
||||||
try {
|
createCheck = async (req, res, next) => {
|
||||||
const checkData = { ...req.body };
|
try {
|
||||||
const check = await req.db.createCheck(checkData);
|
await createCheckParamValidation.validateAsync(req.params);
|
||||||
return res
|
await createCheckBodyValidation.validateAsync(req.body);
|
||||||
.status(200)
|
} catch (error) {
|
||||||
.json({ success: true, msg: successMessages.CHECK_CREATE, data: check });
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
} catch (error) {
|
return;
|
||||||
next(handleError(error, SERVICE_NAME, "createCheck"));
|
}
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
const getChecks = async (req, res, next) => {
|
try {
|
||||||
try {
|
const checkData = { ...req.body };
|
||||||
await getChecksParamValidation.validateAsync(req.params);
|
const check = await this.db.createCheck(checkData);
|
||||||
await getChecksQueryValidation.validateAsync(req.query);
|
return res
|
||||||
} catch (error) {
|
.status(200)
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
.json({ success: true, msg: successMessages.CHECK_CREATE, data: check });
|
||||||
return;
|
} catch (error) {
|
||||||
}
|
next(handleError(error, SERVICE_NAME, "createCheck"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
try {
|
getChecks = async (req, res, next) => {
|
||||||
const checks = await req.db.getChecks(req);
|
try {
|
||||||
const checksCount = await req.db.getChecksCount(req);
|
await getChecksParamValidation.validateAsync(req.params);
|
||||||
return res.status(200).json({
|
await getChecksQueryValidation.validateAsync(req.query);
|
||||||
success: true,
|
} catch (error) {
|
||||||
msg: successMessages.CHECK_GET,
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
data: { checksCount, checks },
|
return;
|
||||||
});
|
}
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "getChecks"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
const getTeamChecks = async (req, res, next) => {
|
try {
|
||||||
try {
|
const checks = await this.db.getChecks(req);
|
||||||
await getTeamChecksParamValidation.validateAsync(req.params);
|
const checksCount = await this.db.getChecksCount(req);
|
||||||
await getTeamChecksQueryValidation.validateAsync(req.query);
|
return res.status(200).json({
|
||||||
} catch (error) {
|
success: true,
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
msg: successMessages.CHECK_GET,
|
||||||
return;
|
data: { checksCount, checks },
|
||||||
}
|
});
|
||||||
try {
|
} catch (error) {
|
||||||
const checkData = await req.db.getTeamChecks(req);
|
next(handleError(error, SERVICE_NAME, "getChecks"));
|
||||||
return res.status(200).json({
|
}
|
||||||
success: true,
|
};
|
||||||
msg: successMessages.CHECK_GET,
|
|
||||||
data: checkData,
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "getTeamChecks"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
const deleteChecks = async (req, res, next) => {
|
getTeamChecks = async (req, res, next) => {
|
||||||
try {
|
try {
|
||||||
await deleteChecksParamValidation.validateAsync(req.params);
|
await getTeamChecksParamValidation.validateAsync(req.params);
|
||||||
} catch (error) {
|
await getTeamChecksQueryValidation.validateAsync(req.query);
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
} catch (error) {
|
||||||
return;
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
}
|
return;
|
||||||
|
}
|
||||||
|
try {
|
||||||
|
const checkData = await this.db.getTeamChecks(req);
|
||||||
|
return res.status(200).json({
|
||||||
|
success: true,
|
||||||
|
msg: successMessages.CHECK_GET,
|
||||||
|
data: checkData,
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "getTeamChecks"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
try {
|
deleteChecks = async (req, res, next) => {
|
||||||
const deletedCount = await req.db.deleteChecks(req.params.monitorId);
|
try {
|
||||||
return res.status(200).json({
|
await deleteChecksParamValidation.validateAsync(req.params);
|
||||||
success: true,
|
} catch (error) {
|
||||||
msg: successMessages.CHECK_DELETE,
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
data: { deletedCount },
|
return;
|
||||||
});
|
}
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "deleteChecks"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
const deleteChecksByTeamId = async (req, res, next) => {
|
try {
|
||||||
try {
|
const deletedCount = await this.db.deleteChecks(req.params.monitorId);
|
||||||
await deleteChecksByTeamIdParamValidation.validateAsync(req.params);
|
return res.status(200).json({
|
||||||
} catch (error) {
|
success: true,
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
msg: successMessages.CHECK_DELETE,
|
||||||
return;
|
data: { deletedCount },
|
||||||
}
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "deleteChecks"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
try {
|
deleteChecksByTeamId = async (req, res, next) => {
|
||||||
const deletedCount = await req.db.deleteChecksByTeamId(req.params.teamId);
|
try {
|
||||||
return res.status(200).json({
|
await deleteChecksByTeamIdParamValidation.validateAsync(req.params);
|
||||||
success: true,
|
} catch (error) {
|
||||||
msg: successMessages.CHECK_DELETE,
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
data: { deletedCount },
|
return;
|
||||||
});
|
}
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "deleteChecksByTeamId"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
const updateChecksTTL = async (req, res, next) => {
|
try {
|
||||||
const SECONDS_PER_DAY = 86400;
|
const deletedCount = await this.db.deleteChecksByTeamId(req.params.teamId);
|
||||||
|
return res.status(200).json({
|
||||||
|
success: true,
|
||||||
|
msg: successMessages.CHECK_DELETE,
|
||||||
|
data: { deletedCount },
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "deleteChecksByTeamId"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
try {
|
updateChecksTTL = async (req, res, next) => {
|
||||||
await updateChecksTTLBodyValidation.validateAsync(req.body);
|
const SECONDS_PER_DAY = 86400;
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
|
||||||
|
|
||||||
try {
|
try {
|
||||||
// Get user's teamId
|
await updateChecksTTLBodyValidation.validateAsync(req.body);
|
||||||
const token = getTokenFromHeaders(req.headers);
|
} catch (error) {
|
||||||
const { jwtSecret } = req.settingsService.getSettings();
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
const { teamId } = jwt.verify(token, jwtSecret);
|
return;
|
||||||
const ttl = parseInt(req.body.ttl, 10) * SECONDS_PER_DAY;
|
}
|
||||||
await req.db.updateChecksTTL(teamId, ttl);
|
|
||||||
return res.status(200).json({
|
|
||||||
success: true,
|
|
||||||
msg: successMessages.CHECK_UPDATE_TTL,
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "updateTTL"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
export {
|
try {
|
||||||
createCheck,
|
// Get user's teamId
|
||||||
getChecks,
|
const token = getTokenFromHeaders(req.headers);
|
||||||
getTeamChecks,
|
const { jwtSecret } = this.settingsService.getSettings();
|
||||||
deleteChecks,
|
const { teamId } = jwt.verify(token, jwtSecret);
|
||||||
deleteChecksByTeamId,
|
const ttl = parseInt(req.body.ttl, 10) * SECONDS_PER_DAY;
|
||||||
updateChecksTTL,
|
await this.db.updateChecksTTL(teamId, ttl);
|
||||||
};
|
return res.status(200).json({
|
||||||
|
success: true,
|
||||||
|
msg: successMessages.CHECK_UPDATE_TTL,
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "updateTTL"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
}
|
||||||
|
export default CheckController;
|
||||||
@@ -4,83 +4,90 @@ import {
|
|||||||
inviteVerificationBodyValidation,
|
inviteVerificationBodyValidation,
|
||||||
} from "../validation/joi.js";
|
} from "../validation/joi.js";
|
||||||
import logger from "../utils/logger.js";
|
import logger from "../utils/logger.js";
|
||||||
import dotenv from "dotenv";
|
|
||||||
import jwt from "jsonwebtoken";
|
import jwt from "jsonwebtoken";
|
||||||
import { handleError, handleValidationError } from "./controllerUtils.js";
|
import { handleError, handleValidationError } from "./controllerUtils.js";
|
||||||
import { getTokenFromHeaders } from "../utils/utils.js";
|
import { getTokenFromHeaders } from "../utils/utils.js";
|
||||||
|
|
||||||
dotenv.config();
|
|
||||||
|
|
||||||
const SERVICE_NAME = "inviteController";
|
const SERVICE_NAME = "inviteController";
|
||||||
|
|
||||||
/**
|
class InviteController {
|
||||||
* Issues an invitation to a new user. Only admins can invite new users. An invitation token is created and sent via email.
|
constructor(db, settingsService, emailService) {
|
||||||
* @async
|
this.db = db;
|
||||||
* @param {Object} req - The Express request object.
|
this.settingsService = settingsService;
|
||||||
* @property {Object} req.headers - The headers of the request.
|
this.emailService = emailService;
|
||||||
* @property {string} req.headers.authorization - The authorization header containing the JWT token.
|
}
|
||||||
* @property {Object} req.body - The body of the request.
|
|
||||||
* @property {string} req.body.email - The email of the user to be invited.
|
/**
|
||||||
* @param {Object} res - The Express response object.
|
* Issues an invitation to a new user. Only admins can invite new users. An invitation token is created and sent via email.
|
||||||
* @param {function} next - The next middleware function.
|
* @async
|
||||||
* @returns {Object} The response object with a success status, a message indicating the sending of the invitation, and the invitation token.
|
* @param {Object} req - The Express request object.
|
||||||
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
* @property {Object} req.headers - The headers of the request.
|
||||||
*/
|
* @property {string} req.headers.authorization - The authorization header containing the JWT token.
|
||||||
const issueInvitation = async (req, res, next) => {
|
* @property {Object} req.body - The body of the request.
|
||||||
try {
|
* @property {string} req.body.email - The email of the user to be invited.
|
||||||
// Only admins can invite
|
* @param {Object} res - The Express response object.
|
||||||
const token = getTokenFromHeaders(req.headers);
|
* @param {function} next - The next middleware function.
|
||||||
const { role, firstname, teamId } = jwt.decode(token);
|
* @returns {Object} The response object with a success status, a message indicating the sending of the invitation, and the invitation token.
|
||||||
req.body.teamId = teamId;
|
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
||||||
|
*/
|
||||||
|
issueInvitation = async (req, res, next) => {
|
||||||
try {
|
try {
|
||||||
await inviteRoleValidation.validateAsync({ roles: role });
|
// Only admins can invite
|
||||||
await inviteBodyValidation.validateAsync(req.body);
|
const token = getTokenFromHeaders(req.headers);
|
||||||
|
const { role, firstname, teamId } = jwt.decode(token);
|
||||||
|
req.body.teamId = teamId;
|
||||||
|
try {
|
||||||
|
await inviteRoleValidation.validateAsync({ roles: role });
|
||||||
|
await inviteBodyValidation.validateAsync(req.body);
|
||||||
|
} catch (error) {
|
||||||
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
|
||||||
|
const inviteToken = await this.db.requestInviteToken({ ...req.body });
|
||||||
|
const { clientHost } = this.settingsService.getSettings();
|
||||||
|
this.emailService
|
||||||
|
.buildAndSendEmail(
|
||||||
|
"employeeActivationTemplate",
|
||||||
|
{
|
||||||
|
name: firstname,
|
||||||
|
link: `${clientHost}/register/${inviteToken.token}`,
|
||||||
|
},
|
||||||
|
req.body.email,
|
||||||
|
"Welcome to Uptime Monitor"
|
||||||
|
)
|
||||||
|
.catch((error) => {
|
||||||
|
logger.error({
|
||||||
|
message: error.message,
|
||||||
|
service: SERVICE_NAME,
|
||||||
|
method: "issueInvitation",
|
||||||
|
stack: error.stack,
|
||||||
|
});
|
||||||
|
});
|
||||||
|
|
||||||
|
return res
|
||||||
|
.status(200)
|
||||||
|
.json({ success: true, msg: "Invite sent", data: inviteToken });
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "inviteController"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
|
inviteVerifyController = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await inviteVerificationBodyValidation.validateAsync(req.body);
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
return;
|
return;
|
||||||
}
|
}
|
||||||
|
|
||||||
const inviteToken = await req.db.requestInviteToken({ ...req.body });
|
try {
|
||||||
const { clientHost } = req.settingsService.getSettings();
|
const invite = await this.db.getInviteToken(req.body.token);
|
||||||
req.emailService
|
res.status(200).json({ status: "success", msg: "Invite verified", data: invite });
|
||||||
.buildAndSendEmail(
|
} catch (error) {
|
||||||
"employeeActivationTemplate",
|
next(handleError(error, SERVICE_NAME, "inviteVerifyController"));
|
||||||
{
|
}
|
||||||
name: firstname,
|
};
|
||||||
link: `${clientHost}/register/${inviteToken.token}`,
|
}
|
||||||
},
|
|
||||||
req.body.email,
|
|
||||||
"Welcome to Uptime Monitor"
|
|
||||||
)
|
|
||||||
.catch((error) => {
|
|
||||||
logger.error({
|
|
||||||
message: error.message,
|
|
||||||
service: SERVICE_NAME,
|
|
||||||
method: "issueInvitation",
|
|
||||||
stack: error.stack,
|
|
||||||
});
|
|
||||||
});
|
|
||||||
|
|
||||||
return res.status(200).json({ success: true, msg: "Invite sent", data: inviteToken });
|
export default InviteController;
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "inviteController"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
const inviteVerifyController = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
await inviteVerificationBodyValidation.validateAsync(req.body);
|
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
|
||||||
|
|
||||||
try {
|
|
||||||
const invite = await req.db.getInviteToken(req.body.token);
|
|
||||||
res.status(200).json({ status: "success", msg: "Invite verified", data: invite });
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "inviteVerifyController"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
export { issueInvitation, inviteVerifyController };
|
|
||||||
@@ -11,157 +11,156 @@ import jwt from "jsonwebtoken";
|
|||||||
import { getTokenFromHeaders } from "../utils/utils.js";
|
import { getTokenFromHeaders } from "../utils/utils.js";
|
||||||
import { successMessages } from "../utils/messages.js";
|
import { successMessages } from "../utils/messages.js";
|
||||||
import { handleValidationError, handleError } from "./controllerUtils.js";
|
import { handleValidationError, handleError } from "./controllerUtils.js";
|
||||||
|
|
||||||
const SERVICE_NAME = "maintenanceWindowController";
|
const SERVICE_NAME = "maintenanceWindowController";
|
||||||
|
|
||||||
const createMaintenanceWindows = async (req, res, next) => {
|
class MaintenanceWindowController {
|
||||||
try {
|
constructor(db, settingsService) {
|
||||||
await createMaintenanceWindowBodyValidation.validateAsync(req.body);
|
this.db = db;
|
||||||
} catch (error) {
|
this.settingsService = settingsService;
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
}
|
||||||
try {
|
|
||||||
const token = getTokenFromHeaders(req.headers);
|
createMaintenanceWindows = async (req, res, next) => {
|
||||||
const { jwtSecret } = req.settingsService.getSettings();
|
try {
|
||||||
const { teamId } = jwt.verify(token, jwtSecret);
|
await createMaintenanceWindowBodyValidation.validateAsync(req.body);
|
||||||
const monitorIds = req.body.monitors;
|
} catch (error) {
|
||||||
const dbTransactions = monitorIds.map((monitorId) => {
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
return req.db.createMaintenanceWindow({
|
return;
|
||||||
teamId,
|
}
|
||||||
monitorId,
|
try {
|
||||||
name: req.body.name,
|
const token = getTokenFromHeaders(req.headers);
|
||||||
active: req.body.active ? req.body.active : true,
|
const { jwtSecret } = this.settingsService.getSettings();
|
||||||
repeat: req.body.repeat,
|
const { teamId } = jwt.verify(token, jwtSecret);
|
||||||
start: req.body.start,
|
const monitorIds = req.body.monitors;
|
||||||
end: req.body.end,
|
const dbTransactions = monitorIds.map((monitorId) => {
|
||||||
|
return this.db.createMaintenanceWindow({
|
||||||
|
teamId,
|
||||||
|
monitorId,
|
||||||
|
name: req.body.name,
|
||||||
|
active: req.body.active ? req.body.active : true,
|
||||||
|
repeat: req.body.repeat,
|
||||||
|
start: req.body.start,
|
||||||
|
end: req.body.end,
|
||||||
|
});
|
||||||
});
|
});
|
||||||
});
|
await Promise.all(dbTransactions);
|
||||||
await Promise.all(dbTransactions);
|
return res.status(201).json({
|
||||||
return res.status(201).json({
|
success: true,
|
||||||
success: true,
|
msg: successMessages.MAINTENANCE_WINDOW_CREATE,
|
||||||
msg: successMessages.MAINTENANCE_WINDOW_CREATE,
|
});
|
||||||
});
|
} catch (error) {
|
||||||
} catch (error) {
|
next(handleError(error, SERVICE_NAME, "createMaintenanceWindow"));
|
||||||
next(handleError(error, SERVICE_NAME, "createMaintenanceWindow"));
|
}
|
||||||
}
|
};
|
||||||
};
|
|
||||||
|
|
||||||
const getMaintenanceWindowById = async (req, res, next) => {
|
getMaintenanceWindowById = async (req, res, next) => {
|
||||||
try {
|
try {
|
||||||
await getMaintenanceWindowByIdParamValidation.validateAsync(req.params);
|
await getMaintenanceWindowByIdParamValidation.validateAsync(req.params);
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
return;
|
return;
|
||||||
}
|
}
|
||||||
try {
|
try {
|
||||||
const maintenanceWindow = await req.db.getMaintenanceWindowById(req.params.id);
|
const maintenanceWindow = await this.db.getMaintenanceWindowById(req.params.id);
|
||||||
return res.status(200).json({
|
return res.status(200).json({
|
||||||
success: true,
|
success: true,
|
||||||
msg: successMessages.MAINTENANCE_WINDOW_GET_BY_ID,
|
msg: successMessages.MAINTENANCE_WINDOW_GET_BY_ID,
|
||||||
data: maintenanceWindow,
|
data: maintenanceWindow,
|
||||||
});
|
});
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleError(error, SERVICE_NAME, "getMaintenanceWindowById"));
|
next(handleError(error, SERVICE_NAME, "getMaintenanceWindowById"));
|
||||||
}
|
}
|
||||||
};
|
};
|
||||||
|
|
||||||
const getMaintenanceWindowsByTeamId = async (req, res, next) => {
|
getMaintenanceWindowsByTeamId = async (req, res, next) => {
|
||||||
try {
|
try {
|
||||||
await getMaintenanceWindowsByTeamIdQueryValidation.validateAsync(req.query);
|
await getMaintenanceWindowsByTeamIdQueryValidation.validateAsync(req.query);
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
return;
|
return;
|
||||||
}
|
}
|
||||||
|
|
||||||
try {
|
try {
|
||||||
const token = getTokenFromHeaders(req.headers);
|
const token = getTokenFromHeaders(req.headers);
|
||||||
const { jwtSecret } = req.settingsService.getSettings();
|
const { jwtSecret } = this.settingsService.getSettings();
|
||||||
const { teamId } = jwt.verify(token, jwtSecret);
|
const { teamId } = jwt.verify(token, jwtSecret);
|
||||||
const maintenanceWindows = await req.db.getMaintenanceWindowsByTeamId(
|
const maintenanceWindows = await this.db.getMaintenanceWindowsByTeamId(
|
||||||
teamId,
|
teamId,
|
||||||
req.query
|
req.query
|
||||||
);
|
);
|
||||||
|
|
||||||
return res.status(200).json({
|
return res.status(200).json({
|
||||||
success: true,
|
success: true,
|
||||||
msg: successMessages.MAINTENANCE_WINDOW_GET_BY_TEAM,
|
msg: successMessages.MAINTENANCE_WINDOW_GET_BY_TEAM,
|
||||||
data: maintenanceWindows,
|
data: maintenanceWindows,
|
||||||
});
|
});
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleError(error, SERVICE_NAME, "getMaintenanceWindowsByUserId"));
|
next(handleError(error, SERVICE_NAME, "getMaintenanceWindowsByUserId"));
|
||||||
}
|
}
|
||||||
};
|
};
|
||||||
|
|
||||||
const getMaintenanceWindowsByMonitorId = async (req, res, next) => {
|
getMaintenanceWindowsByMonitorId = async (req, res, next) => {
|
||||||
try {
|
try {
|
||||||
await getMaintenanceWindowsByMonitorIdParamValidation.validateAsync(req.params);
|
await getMaintenanceWindowsByMonitorIdParamValidation.validateAsync(req.params);
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
return;
|
return;
|
||||||
}
|
}
|
||||||
|
|
||||||
try {
|
try {
|
||||||
const maintenanceWindows = await req.db.getMaintenanceWindowsByMonitorId(
|
const maintenanceWindows = await this.db.getMaintenanceWindowsByMonitorId(
|
||||||
req.params.monitorId
|
req.params.monitorId
|
||||||
);
|
);
|
||||||
|
|
||||||
return res.status(200).json({
|
return res.status(200).json({
|
||||||
success: true,
|
success: true,
|
||||||
msg: successMessages.MAINTENANCE_WINDOW_GET_BY_USER,
|
msg: successMessages.MAINTENANCE_WINDOW_GET_BY_USER,
|
||||||
data: maintenanceWindows,
|
data: maintenanceWindows,
|
||||||
});
|
});
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleError(error, SERVICE_NAME, "getMaintenanceWindowsByMonitorId"));
|
next(handleError(error, SERVICE_NAME, "getMaintenanceWindowsByMonitorId"));
|
||||||
}
|
}
|
||||||
};
|
};
|
||||||
|
|
||||||
const deleteMaintenanceWindow = async (req, res, next) => {
|
deleteMaintenanceWindow = async (req, res, next) => {
|
||||||
try {
|
try {
|
||||||
await deleteMaintenanceWindowByIdParamValidation.validateAsync(req.params);
|
await deleteMaintenanceWindowByIdParamValidation.validateAsync(req.params);
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
return;
|
return;
|
||||||
}
|
}
|
||||||
try {
|
try {
|
||||||
await req.db.deleteMaintenanceWindowById(req.params.id);
|
await this.db.deleteMaintenanceWindowById(req.params.id);
|
||||||
return res.status(200).json({
|
return res.status(200).json({
|
||||||
success: true,
|
success: true,
|
||||||
msg: successMessages.MAINTENANCE_WINDOW_DELETE,
|
msg: successMessages.MAINTENANCE_WINDOW_DELETE,
|
||||||
});
|
});
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleError(error, SERVICE_NAME, "deleteMaintenanceWindow"));
|
next(handleError(error, SERVICE_NAME, "deleteMaintenanceWindow"));
|
||||||
}
|
}
|
||||||
};
|
};
|
||||||
|
|
||||||
const editMaintenanceWindow = async (req, res, next) => {
|
editMaintenanceWindow = async (req, res, next) => {
|
||||||
try {
|
try {
|
||||||
await editMaintenanceWindowByIdParamValidation.validateAsync(req.params);
|
await editMaintenanceWindowByIdParamValidation.validateAsync(req.params);
|
||||||
await editMaintenanceByIdWindowBodyValidation.validateAsync(req.body);
|
await editMaintenanceByIdWindowBodyValidation.validateAsync(req.body);
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
return;
|
return;
|
||||||
}
|
}
|
||||||
try {
|
try {
|
||||||
const editedMaintenanceWindow = await req.db.editMaintenanceWindowById(
|
const editedMaintenanceWindow = await this.db.editMaintenanceWindowById(
|
||||||
req.params.id,
|
req.params.id,
|
||||||
req.body
|
req.body
|
||||||
);
|
);
|
||||||
return res.status(200).json({
|
return res.status(200).json({
|
||||||
success: true,
|
success: true,
|
||||||
msg: successMessages.MAINTENANCE_WINDOW_EDIT,
|
msg: successMessages.MAINTENANCE_WINDOW_EDIT,
|
||||||
data: editedMaintenanceWindow,
|
data: editedMaintenanceWindow,
|
||||||
});
|
});
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleError(error, SERVICE_NAME, "editMaintenanceWindow"));
|
next(handleError(error, SERVICE_NAME, "editMaintenanceWindow"));
|
||||||
}
|
}
|
||||||
};
|
};
|
||||||
|
}
|
||||||
|
|
||||||
export {
|
export default MaintenanceWindowController;
|
||||||
createMaintenanceWindows,
|
|
||||||
getMaintenanceWindowById,
|
|
||||||
getMaintenanceWindowsByTeamId,
|
|
||||||
getMaintenanceWindowsByMonitorId,
|
|
||||||
deleteMaintenanceWindow,
|
|
||||||
editMaintenanceWindow,
|
|
||||||
};
|
|
||||||
@@ -14,7 +14,7 @@ import {
|
|||||||
getCertificateParamValidation,
|
getCertificateParamValidation,
|
||||||
} from "../validation/joi.js";
|
} from "../validation/joi.js";
|
||||||
import sslChecker from "ssl-checker";
|
import sslChecker from "ssl-checker";
|
||||||
import { errorMessages, successMessages } from "../utils/messages.js";
|
import { successMessages } from "../utils/messages.js";
|
||||||
import jwt from "jsonwebtoken";
|
import jwt from "jsonwebtoken";
|
||||||
import { getTokenFromHeaders } from "../utils/utils.js";
|
import { getTokenFromHeaders } from "../utils/utils.js";
|
||||||
import logger from "../utils/logger.js";
|
import logger from "../utils/logger.js";
|
||||||
@@ -23,510 +23,503 @@ import axios from "axios";
|
|||||||
|
|
||||||
const SERVICE_NAME = "monitorController";
|
const SERVICE_NAME = "monitorController";
|
||||||
|
|
||||||
/**
|
class MonitorController {
|
||||||
* Returns all monitors
|
constructor(db, settingsService, jobQueue) {
|
||||||
* @async
|
this.db = db;
|
||||||
* @param {Express.Request} req
|
this.settingsService = settingsService;
|
||||||
* @param {Express.Response} res
|
this.jobQueue = jobQueue;
|
||||||
* @param {function} next
|
|
||||||
* @returns {Promise<Express.Response>}
|
|
||||||
* @throws {Error}
|
|
||||||
*/
|
|
||||||
const getAllMonitors = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
const monitors = await req.db.getAllMonitors();
|
|
||||||
return res.status(200).json({
|
|
||||||
success: true,
|
|
||||||
msg: successMessages.MONITOR_GET_ALL,
|
|
||||||
data: monitors,
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "getAllMonitors"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
/**
|
|
||||||
* Returns all monitors with uptime stats for 1,7,30, and 90 days
|
|
||||||
* @async
|
|
||||||
* @param {Express.Request} req
|
|
||||||
* @param {Express.Response} res
|
|
||||||
* @param {function} next
|
|
||||||
* @returns {Promise<Express.Response>}
|
|
||||||
* @throws {Error}
|
|
||||||
*/
|
|
||||||
const getAllMonitorsWithUptimeStats = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
const monitors = await req.db.getAllMonitorsWithUptimeStats();
|
|
||||||
return res.status(200).json({
|
|
||||||
success: true,
|
|
||||||
msg: successMessages.MONITOR_GET_ALL,
|
|
||||||
data: monitors,
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "getAllMonitorsWithUptimeStats"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
/**
|
|
||||||
* Returns monitor stats for monitor with matching ID
|
|
||||||
* @async
|
|
||||||
* @param {Express.Request} req
|
|
||||||
* @param {Express.Response} res
|
|
||||||
* @param {function} next
|
|
||||||
* @returns {Promise<Express.Response>}
|
|
||||||
* @throws {Error}
|
|
||||||
*/
|
|
||||||
const getMonitorStatsById = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
await getMonitorStatsByIdParamValidation.validateAsync(req.params);
|
|
||||||
await getMonitorStatsByIdQueryValidation.validateAsync(req.query);
|
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
}
|
||||||
|
|
||||||
try {
|
/**
|
||||||
const monitorStats = await req.db.getMonitorStatsById(req);
|
* Returns all monitors
|
||||||
return res.status(200).json({
|
* @async
|
||||||
success: true,
|
* @param {Express.Request} req
|
||||||
msg: successMessages.MONITOR_STATS_BY_ID,
|
* @param {Express.Response} res
|
||||||
data: monitorStats,
|
* @param {function} next
|
||||||
});
|
* @returns {Promise<Express.Response>}
|
||||||
} catch (error) {
|
* @throws {Error}
|
||||||
next(handleError(error, SERVICE_NAME, "getMonitorStatsById"));
|
*/
|
||||||
}
|
getAllMonitors = async (req, res, next) => {
|
||||||
};
|
try {
|
||||||
|
const monitors = await this.db.getAllMonitors();
|
||||||
|
return res.status(200).json({
|
||||||
|
success: true,
|
||||||
|
msg: successMessages.MONITOR_GET_ALL,
|
||||||
|
data: monitors,
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "getAllMonitors"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
const getMonitorCertificate = async (req, res, next, fetchMonitorCertificate) => {
|
/**
|
||||||
try {
|
* Returns all monitors with uptime stats for 1,7,30, and 90 days
|
||||||
await getCertificateParamValidation.validateAsync(req.params);
|
* @async
|
||||||
} catch (error) {
|
* @param {Express.Request} req
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
* @param {Express.Response} res
|
||||||
}
|
* @param {function} next
|
||||||
|
* @returns {Promise<Express.Response>}
|
||||||
|
* @throws {Error}
|
||||||
|
*/
|
||||||
|
getAllMonitorsWithUptimeStats = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
const monitors = await this.db.getAllMonitorsWithUptimeStats();
|
||||||
|
return res.status(200).json({
|
||||||
|
success: true,
|
||||||
|
msg: successMessages.MONITOR_GET_ALL,
|
||||||
|
data: monitors,
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "getAllMonitorsWithUptimeStats"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
try {
|
/**
|
||||||
const { monitorId } = req.params;
|
* Returns monitor stats for monitor with matching ID
|
||||||
const monitor = await req.db.getMonitorById(monitorId);
|
* @async
|
||||||
const certificate = await fetchMonitorCertificate(sslChecker, monitor);
|
* @param {Express.Request} req
|
||||||
|
* @param {Express.Response} res
|
||||||
|
* @param {function} next
|
||||||
|
* @returns {Promise<Express.Response>}
|
||||||
|
* @throws {Error}
|
||||||
|
*/
|
||||||
|
getMonitorStatsById = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await getMonitorStatsByIdParamValidation.validateAsync(req.params);
|
||||||
|
await getMonitorStatsByIdQueryValidation.validateAsync(req.query);
|
||||||
|
} catch (error) {
|
||||||
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
|
||||||
return res.status(200).json({
|
try {
|
||||||
success: true,
|
const monitorStats = await this.db.getMonitorStatsById(req);
|
||||||
msg: successMessages.MONITOR_CERTIFICATE,
|
return res.status(200).json({
|
||||||
data: {
|
success: true,
|
||||||
certificateDate: new Date(certificate.validTo),
|
msg: successMessages.MONITOR_STATS_BY_ID,
|
||||||
},
|
data: monitorStats,
|
||||||
});
|
});
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleError(error, SERVICE_NAME, "getMonitorCertificate"));
|
next(handleError(error, SERVICE_NAME, "getMonitorStatsById"));
|
||||||
}
|
}
|
||||||
};
|
};
|
||||||
|
|
||||||
/**
|
getMonitorCertificate = async (req, res, next, fetchMonitorCertificate) => {
|
||||||
* Retrieves a monitor by its ID.
|
try {
|
||||||
* @async
|
await getCertificateParamValidation.validateAsync(req.params);
|
||||||
* @param {Object} req - The Express request object.
|
} catch (error) {
|
||||||
* @property {Object} req.params - The parameters of the request.
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
* @property {string} req.params.monitorId - The ID of the monitor to be retrieved.
|
}
|
||||||
* @param {Object} res - The Express response object.
|
|
||||||
* @param {function} next - The next middleware function.
|
|
||||||
* @returns {Object} The response object with a success status, a message, and the retrieved monitor data.
|
|
||||||
* @throws {Error} If there is an error during the process, especially if the monitor is not found (404) or if there is a validation error (422).
|
|
||||||
*/
|
|
||||||
const getMonitorById = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
await getMonitorByIdParamValidation.validateAsync(req.params);
|
|
||||||
await getMonitorByIdQueryValidation.validateAsync(req.query);
|
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
|
||||||
|
|
||||||
try {
|
try {
|
||||||
const monitor = await req.db.getMonitorById(req.params.monitorId);
|
const { monitorId } = req.params;
|
||||||
return res.status(200).json({
|
const monitor = await this.db.getMonitorById(monitorId);
|
||||||
success: true,
|
const certificate = await fetchMonitorCertificate(sslChecker, monitor);
|
||||||
msg: successMessages.MONITOR_GET_BY_ID,
|
|
||||||
data: monitor,
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "getMonitorById"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
/**
|
return res.status(200).json({
|
||||||
* Retrieves all monitors and a summary for a team based on the team ID.
|
success: true,
|
||||||
* @async
|
msg: successMessages.MONITOR_CERTIFICATE,
|
||||||
* @param {Object} req - The Express request object.
|
data: {
|
||||||
* @property {Object} req.params - The parameters of the request.
|
certificateDate: new Date(certificate.validTo),
|
||||||
* @property {string} req.params.teamId - The ID of the team.
|
},
|
||||||
* @property {Object} req.query - The query parameters of the request.
|
});
|
||||||
* @property {string} req.query.type - The type of the request.
|
} catch (error) {
|
||||||
* @param {Object} res - The Express response object.
|
next(handleError(error, SERVICE_NAME, "getMonitorCertificate"));
|
||||||
* @param {function} next - The next middleware function.
|
}
|
||||||
* @returns {Object} The response object with a success status, a message, and the data containing the monitors and summary for the team.
|
};
|
||||||
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
|
||||||
*/
|
|
||||||
const getMonitorsAndSummaryByTeamId = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
await getMonitorsAndSummaryByTeamIdParamValidation.validateAsync(req.params);
|
|
||||||
await getMonitorsAndSummaryByTeamIdQueryValidation.validateAsync(req.query);
|
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
|
||||||
|
|
||||||
try {
|
/**
|
||||||
const { teamId } = req.params;
|
* Retrieves a monitor by its ID.
|
||||||
const { type } = req.query;
|
* @async
|
||||||
const monitorsSummary = await req.db.getMonitorsAndSummaryByTeamId(teamId, type);
|
* @param {Object} req - The Express request object.
|
||||||
return res.status(200).json({
|
* @property {Object} req.params - The parameters of the request.
|
||||||
success: true,
|
* @property {string} req.params.monitorId - The ID of the monitor to be retrieved.
|
||||||
msg: successMessages.MONITOR_GET_BY_USER_ID(teamId),
|
* @param {Object} res - The Express response object.
|
||||||
data: monitorsSummary,
|
* @param {function} next - The next middleware function.
|
||||||
});
|
* @returns {Object} The response object with a success status, a message, and the retrieved monitor data.
|
||||||
} catch (error) {
|
* @throws {Error} If there is an error during the process, especially if the monitor is not found (404) or if there is a validation error (422).
|
||||||
next(handleError(error, SERVICE_NAME, "getMonitorsAndSummaryByTeamId"));
|
*/
|
||||||
}
|
getMonitorById = async (req, res, next) => {
|
||||||
};
|
try {
|
||||||
|
await getMonitorByIdParamValidation.validateAsync(req.params);
|
||||||
|
await getMonitorByIdQueryValidation.validateAsync(req.query);
|
||||||
|
} catch (error) {
|
||||||
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
|
||||||
/**
|
try {
|
||||||
* Retrieves all monitors associated with a team by the team's ID.
|
const monitor = await this.db.getMonitorById(req.params.monitorId);
|
||||||
* @async
|
return res.status(200).json({
|
||||||
* @param {Object} req - The Express request object.
|
success: true,
|
||||||
* @property {Object} req.params - The parameters of the request.
|
msg: successMessages.MONITOR_GET_BY_ID,
|
||||||
* @property {string} req.params.teamId - The ID of the team.
|
data: monitor,
|
||||||
* @property {Object} req.query - The query parameters of the request.
|
});
|
||||||
* @param {Object} res - The Express response object.
|
} catch (error) {
|
||||||
* @param {function} next - The next middleware function.
|
next(handleError(error, SERVICE_NAME, "getMonitorById"));
|
||||||
* @returns {Object} The response object with a success status, a message, and the data containing the monitors for the team.
|
}
|
||||||
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
};
|
||||||
*/
|
|
||||||
const getMonitorsByTeamId = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
await getMonitorsByTeamIdValidation.validateAsync(req.params);
|
|
||||||
await getMonitorsByTeamIdQueryValidation.validateAsync(req.query);
|
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
|
||||||
|
|
||||||
try {
|
/**
|
||||||
const teamId = req.params.teamId;
|
* Retrieves all monitors and a summary for a team based on the team ID.
|
||||||
const monitors = await req.db.getMonitorsByTeamId(req, res);
|
* @async
|
||||||
return res.status(200).json({
|
* @param {Object} req - The Express request object.
|
||||||
success: true,
|
* @property {Object} req.params - The parameters of the request.
|
||||||
msg: successMessages.MONITOR_GET_BY_USER_ID(teamId),
|
* @property {string} req.params.teamId - The ID of the team.
|
||||||
data: monitors,
|
* @property {Object} req.query - The query parameters of the request.
|
||||||
});
|
* @property {string} req.query.type - The type of the request.
|
||||||
} catch (error) {
|
* @param {Object} res - The Express response object.
|
||||||
next(handleError(error, SERVICE_NAME, "getMonitorsByTeamId"));
|
* @param {function} next - The next middleware function.
|
||||||
next(error);
|
* @returns {Object} The response object with a success status, a message, and the data containing the monitors and summary for the team.
|
||||||
}
|
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
||||||
};
|
*/
|
||||||
|
getMonitorsAndSummaryByTeamId = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await getMonitorsAndSummaryByTeamIdParamValidation.validateAsync(req.params);
|
||||||
|
await getMonitorsAndSummaryByTeamIdQueryValidation.validateAsync(req.query);
|
||||||
|
} catch (error) {
|
||||||
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
|
||||||
/**
|
try {
|
||||||
* Creates a new monitor and adds it to the job queue.
|
const { teamId } = req.params;
|
||||||
* @async
|
const { type } = req.query;
|
||||||
* @param {Object} req - The Express request object.
|
const monitorsSummary = await this.db.getMonitorsAndSummaryByTeamId(teamId, type);
|
||||||
* @property {Object} req.body - The body of the request.
|
return res.status(200).json({
|
||||||
* @property {Array} req.body.notifications - The notifications associated with the monitor.
|
success: true,
|
||||||
* @param {Object} res - The Express response object.
|
msg: successMessages.MONITOR_GET_BY_USER_ID(teamId),
|
||||||
* @param {function} next - The next middleware function.
|
data: monitorsSummary,
|
||||||
* @returns {Object} The response object with a success status, a message indicating the creation of the monitor, and the created monitor data.
|
});
|
||||||
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
} catch (error) {
|
||||||
*/
|
next(handleError(error, SERVICE_NAME, "getMonitorsAndSummaryByTeamId"));
|
||||||
const createMonitor = async (req, res, next) => {
|
}
|
||||||
try {
|
};
|
||||||
await createMonitorBodyValidation.validateAsync(req.body);
|
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
|
||||||
|
|
||||||
try {
|
/**
|
||||||
const notifications = req.body.notifications;
|
* Retrieves all monitors associated with a team by the team's ID.
|
||||||
const monitor = await req.db.createMonitor(req, res);
|
* @async
|
||||||
|
* @param {Object} req - The Express request object.
|
||||||
|
* @property {Object} req.params - The parameters of the request.
|
||||||
|
* @property {string} req.params.teamId - The ID of the team.
|
||||||
|
* @property {Object} req.query - The query parameters of the request.
|
||||||
|
* @param {Object} res - The Express response object.
|
||||||
|
* @param {function} next - The next middleware function.
|
||||||
|
* @returns {Object} The response object with a success status, a message, and the data containing the monitors for the team.
|
||||||
|
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
||||||
|
*/
|
||||||
|
getMonitorsByTeamId = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await getMonitorsByTeamIdValidation.validateAsync(req.params);
|
||||||
|
await getMonitorsByTeamIdQueryValidation.validateAsync(req.query);
|
||||||
|
} catch (error) {
|
||||||
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
|
||||||
if (notifications && notifications.length > 0) {
|
try {
|
||||||
monitor.notifications = await Promise.all(
|
const teamId = req.params.teamId;
|
||||||
notifications.map(async (notification) => {
|
const monitors = await this.db.getMonitorsByTeamId(req, res);
|
||||||
notification.monitorId = monitor._id;
|
return res.status(200).json({
|
||||||
return await req.db.createNotification(notification);
|
success: true,
|
||||||
|
msg: successMessages.MONITOR_GET_BY_USER_ID(teamId),
|
||||||
|
data: monitors,
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "getMonitorsByTeamId"));
|
||||||
|
next(error);
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
|
/**
|
||||||
|
* Creates a new monitor and adds it to the job queue.
|
||||||
|
* @async
|
||||||
|
* @param {Object} req - The Express request object.
|
||||||
|
* @property {Object} req.body - The body of the request.
|
||||||
|
* @property {Array} req.body.notifications - The notifications associated with the monitor.
|
||||||
|
* @param {Object} res - The Express response object.
|
||||||
|
* @param {function} next - The next middleware function.
|
||||||
|
* @returns {Object} The response object with a success status, a message indicating the creation of the monitor, and the created monitor data.
|
||||||
|
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
||||||
|
*/
|
||||||
|
createMonitor = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await createMonitorBodyValidation.validateAsync(req.body);
|
||||||
|
} catch (error) {
|
||||||
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
|
||||||
|
try {
|
||||||
|
const notifications = req.body.notifications;
|
||||||
|
const monitor = await this.db.createMonitor(req, res);
|
||||||
|
|
||||||
|
if (notifications && notifications.length > 0) {
|
||||||
|
monitor.notifications = await Promise.all(
|
||||||
|
notifications.map(async (notification) => {
|
||||||
|
notification.monitorId = monitor._id;
|
||||||
|
return await this.db.createNotification(notification);
|
||||||
|
})
|
||||||
|
);
|
||||||
|
}
|
||||||
|
|
||||||
|
await monitor.save();
|
||||||
|
// Add monitor to job queue
|
||||||
|
this.jobQueue.addJob(monitor._id, monitor);
|
||||||
|
return res.status(201).json({
|
||||||
|
success: true,
|
||||||
|
msg: successMessages.MONITOR_CREATE,
|
||||||
|
data: monitor,
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "createMonitor"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
|
/**
|
||||||
|
* Checks if the endpoint can be resolved
|
||||||
|
* @async
|
||||||
|
* @param {Object} req - The Express request object.
|
||||||
|
* @property {Object} req.query - The query parameters of the request.
|
||||||
|
* @param {Object} res - The Express response object.
|
||||||
|
* @param {function} next - The next middleware function.
|
||||||
|
* @returns {Object} The response object with a success status, a message, and the resolution result.
|
||||||
|
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
||||||
|
*/
|
||||||
|
checkEndpointResolution = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await getMonitorURLByQueryValidation.validateAsync(req.query);
|
||||||
|
} catch (error) {
|
||||||
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
|
||||||
|
try {
|
||||||
|
const { monitorURL } = req.query;
|
||||||
|
const parsedUrl = new URL(monitorURL);
|
||||||
|
const response = await axios.get(parsedUrl, {
|
||||||
|
timeout: 5000,
|
||||||
|
validateStatus: () => true,
|
||||||
|
});
|
||||||
|
return res.status(200).json({
|
||||||
|
success: true,
|
||||||
|
code: response.status,
|
||||||
|
statusText: response.statusText,
|
||||||
|
msg: `URL resolved successfully`,
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "checkEndpointResolution"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
|
/**
|
||||||
|
* Deletes a monitor by its ID and also deletes associated checks, alerts, and notifications.
|
||||||
|
* @async
|
||||||
|
* @param {Object} req - The Express request object.
|
||||||
|
* @property {Object} req.params - The parameters of the request.
|
||||||
|
* @property {string} req.params.monitorId - The ID of the monitor to be deleted.
|
||||||
|
* @param {Object} res - The Express response object.
|
||||||
|
* @param {function} next - The next middleware function.
|
||||||
|
* @returns {Object} The response object with a success status and a message indicating the deletion of the monitor.
|
||||||
|
* @throws {Error} If there is an error during the process, especially if there is a validation error (422) or an error in deleting associated records.
|
||||||
|
*/
|
||||||
|
deleteMonitor = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await getMonitorByIdParamValidation.validateAsync(req.params);
|
||||||
|
} catch (error) {
|
||||||
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
|
||||||
|
try {
|
||||||
|
const monitor = await this.db.deleteMonitor(req, res, next);
|
||||||
|
// Delete associated checks,alerts,and notifications
|
||||||
|
try {
|
||||||
|
await this.jobQueue.deleteJob(monitor);
|
||||||
|
await this.db.deleteChecks(monitor._id);
|
||||||
|
await this.db.deletePageSpeedChecksByMonitorId(monitor._id);
|
||||||
|
await this.db.deleteNotificationsByMonitorId(monitor._id);
|
||||||
|
await this.db.deleteHardwareChecksByMonitorId(monitor._id);
|
||||||
|
} catch (error) {
|
||||||
|
logger.error({
|
||||||
|
message: `Error deleting associated records for monitor ${monitor._id} with name ${monitor.name}`,
|
||||||
|
service: SERVICE_NAME,
|
||||||
|
method: "deleteMonitor",
|
||||||
|
stack: error.stack,
|
||||||
|
});
|
||||||
|
}
|
||||||
|
return res.status(200).json({ success: true, msg: successMessages.MONITOR_DELETE });
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "deleteMonitor"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
|
/**
|
||||||
|
* Deletes all monitors associated with a team.
|
||||||
|
* @async
|
||||||
|
* @param {Object} req - The Express request object.
|
||||||
|
* @property {Object} req.headers - The headers of the request.
|
||||||
|
* @property {string} req.headers.authorization - The authorization header containing the JWT token.
|
||||||
|
* @param {Object} res - The Express response object.
|
||||||
|
* @param {function} next
|
||||||
|
* @returns {Object} The response object with a success status and a message indicating the number of deleted monitors.
|
||||||
|
* @throws {Error} If there is an error during the deletion process.
|
||||||
|
*/
|
||||||
|
deleteAllMonitors = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
const token = getTokenFromHeaders(req.headers);
|
||||||
|
const { jwtSecret } = this.settingsService.getSettings();
|
||||||
|
const { teamId } = jwt.verify(token, jwtSecret);
|
||||||
|
const { monitors, deletedCount } = await this.db.deleteAllMonitors(teamId);
|
||||||
|
await Promise.all(
|
||||||
|
monitors.map(async (monitor) => {
|
||||||
|
try {
|
||||||
|
await this.jobQueue.deleteJob(monitor);
|
||||||
|
await this.db.deleteChecks(monitor._id);
|
||||||
|
await this.db.deletePageSpeedChecksByMonitorId(monitor._id);
|
||||||
|
await this.db.deleteNotificationsByMonitorId(monitor._id);
|
||||||
|
} catch (error) {
|
||||||
|
logger.error({
|
||||||
|
message: `Error deleting associated records for monitor ${monitor._id} with name ${monitor.name}`,
|
||||||
|
service: SERVICE_NAME,
|
||||||
|
method: "deleteAllMonitors",
|
||||||
|
stack: error.stack,
|
||||||
|
});
|
||||||
|
}
|
||||||
})
|
})
|
||||||
);
|
);
|
||||||
}
|
return res
|
||||||
|
.status(200)
|
||||||
await monitor.save();
|
.json({ success: true, msg: `Deleted ${deletedCount} monitors` });
|
||||||
// Add monitor to job queue
|
|
||||||
req.jobQueue.addJob(monitor._id, monitor);
|
|
||||||
return res.status(201).json({
|
|
||||||
success: true,
|
|
||||||
msg: successMessages.MONITOR_CREATE,
|
|
||||||
data: monitor,
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "createMonitor"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
/**
|
|
||||||
* Checks if the endpoint can be resolved
|
|
||||||
* @async
|
|
||||||
* @param {Object} req - The Express request object.
|
|
||||||
* @property {Object} req.query - The query parameters of the request.
|
|
||||||
* @param {Object} res - The Express response object.
|
|
||||||
* @param {function} next - The next middleware function.
|
|
||||||
* @returns {Object} The response object with a success status, a message, and the resolution result.
|
|
||||||
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
|
||||||
*/
|
|
||||||
const checkEndpointResolution = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
await getMonitorURLByQueryValidation.validateAsync(req.query);
|
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
|
||||||
|
|
||||||
try {
|
|
||||||
const { monitorURL } = req.query;
|
|
||||||
const parsedUrl = new URL(monitorURL);
|
|
||||||
const response = await axios.get(parsedUrl, {
|
|
||||||
timeout: 5000,
|
|
||||||
validateStatus: () => true,
|
|
||||||
});
|
|
||||||
return res.status(200).json({
|
|
||||||
success: true,
|
|
||||||
code: response.status,
|
|
||||||
statusText: response.statusText,
|
|
||||||
msg: `URL resolved successfully`,
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "checkEndpointResolution"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
/**
|
|
||||||
* Deletes a monitor by its ID and also deletes associated checks, alerts, and notifications.
|
|
||||||
* @async
|
|
||||||
* @param {Object} req - The Express request object.
|
|
||||||
* @property {Object} req.params - The parameters of the request.
|
|
||||||
* @property {string} req.params.monitorId - The ID of the monitor to be deleted.
|
|
||||||
* @param {Object} res - The Express response object.
|
|
||||||
* @param {function} next - The next middleware function.
|
|
||||||
* @returns {Object} The response object with a success status and a message indicating the deletion of the monitor.
|
|
||||||
* @throws {Error} If there is an error during the process, especially if there is a validation error (422) or an error in deleting associated records.
|
|
||||||
*/
|
|
||||||
const deleteMonitor = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
await getMonitorByIdParamValidation.validateAsync(req.params);
|
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
|
||||||
|
|
||||||
try {
|
|
||||||
const monitor = await req.db.deleteMonitor(req, res, next);
|
|
||||||
// Delete associated checks,alerts,and notifications
|
|
||||||
try {
|
|
||||||
await req.jobQueue.deleteJob(monitor);
|
|
||||||
await req.db.deleteChecks(monitor._id);
|
|
||||||
await req.db.deletePageSpeedChecksByMonitorId(monitor._id);
|
|
||||||
await req.db.deleteNotificationsByMonitorId(monitor._id);
|
|
||||||
await req.db.deleteHardwareChecksByMonitorId(monitor._id);
|
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
logger.error({
|
next(handleError(error, SERVICE_NAME, "deleteAllMonitors"));
|
||||||
message: `Error deleting associated records for monitor ${monitor._id} with name ${monitor.name}`,
|
|
||||||
service: SERVICE_NAME,
|
|
||||||
method: "deleteMonitor",
|
|
||||||
stack: error.stack,
|
|
||||||
});
|
|
||||||
}
|
}
|
||||||
return res.status(200).json({ success: true, msg: successMessages.MONITOR_DELETE });
|
};
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "deleteMonitor"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
/**
|
/**
|
||||||
* Deletes all monitors associated with a team.
|
* Edits a monitor by its ID, updates its notifications, and updates its job in the job queue.
|
||||||
* @async
|
* @async
|
||||||
* @param {Object} req - The Express request object.
|
* @param {Object} req - The Express request object.
|
||||||
* @property {Object} req.headers - The headers of the request.
|
* @property {Object} req.params - The parameters of the request.
|
||||||
* @property {string} req.headers.authorization - The authorization header containing the JWT token.
|
* @property {string} req.params.monitorId - The ID of the monitor to be edited.
|
||||||
* @param {Object} res - The Express response object.
|
* @property {Object} req.body - The body of the request.
|
||||||
* @param {function} next
|
* @property {Array} req.body.notifications - The notifications to be associated with the monitor.
|
||||||
* @returns {Object} The response object with a success status and a message indicating the number of deleted monitors.
|
* @param {Object} res - The Express response object.
|
||||||
* @throws {Error} If there is an error during the deletion process.
|
* @param {function} next - The next middleware function.
|
||||||
*/
|
* @returns {Object} The response object with a success status, a message indicating the editing of the monitor, and the edited monitor data.
|
||||||
const deleteAllMonitors = async (req, res, next) => {
|
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
||||||
try {
|
*/
|
||||||
const token = getTokenFromHeaders(req.headers);
|
editMonitor = async (req, res, next) => {
|
||||||
const { jwtSecret } = req.settingsService.getSettings();
|
try {
|
||||||
const { teamId } = jwt.verify(token, jwtSecret);
|
await getMonitorByIdParamValidation.validateAsync(req.params);
|
||||||
const { monitors, deletedCount } = await req.db.deleteAllMonitors(teamId);
|
await editMonitorBodyValidation.validateAsync(req.body);
|
||||||
await Promise.all(
|
} catch (error) {
|
||||||
monitors.map(async (monitor) => {
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
try {
|
return;
|
||||||
await req.jobQueue.deleteJob(monitor);
|
}
|
||||||
await req.db.deleteChecks(monitor._id);
|
|
||||||
await req.db.deletePageSpeedChecksByMonitorId(monitor._id);
|
|
||||||
await req.db.deleteNotificationsByMonitorId(monitor._id);
|
|
||||||
} catch (error) {
|
|
||||||
logger.error({
|
|
||||||
message: `Error deleting associated records for monitor ${monitor._id} with name ${monitor.name}`,
|
|
||||||
service: SERVICE_NAME,
|
|
||||||
method: "deleteAllMonitors",
|
|
||||||
stack: error.stack,
|
|
||||||
});
|
|
||||||
}
|
|
||||||
})
|
|
||||||
);
|
|
||||||
return res
|
|
||||||
.status(200)
|
|
||||||
.json({ success: true, msg: `Deleted ${deletedCount} monitors` });
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "deleteAllMonitors"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
/**
|
try {
|
||||||
* Edits a monitor by its ID, updates its notifications, and updates its job in the job queue.
|
const { monitorId } = req.params;
|
||||||
* @async
|
const monitorBeforeEdit = await this.db.getMonitorById(monitorId);
|
||||||
* @param {Object} req - The Express request object.
|
|
||||||
* @property {Object} req.params - The parameters of the request.
|
|
||||||
* @property {string} req.params.monitorId - The ID of the monitor to be edited.
|
|
||||||
* @property {Object} req.body - The body of the request.
|
|
||||||
* @property {Array} req.body.notifications - The notifications to be associated with the monitor.
|
|
||||||
* @param {Object} res - The Express response object.
|
|
||||||
* @param {function} next - The next middleware function.
|
|
||||||
* @returns {Object} The response object with a success status, a message indicating the editing of the monitor, and the edited monitor data.
|
|
||||||
* @throws {Error} If there is an error during the process, especially if there is a validation error (422).
|
|
||||||
*/
|
|
||||||
const editMonitor = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
await getMonitorByIdParamValidation.validateAsync(req.params);
|
|
||||||
await editMonitorBodyValidation.validateAsync(req.body);
|
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
|
||||||
|
|
||||||
try {
|
// Get notifications from the request body
|
||||||
const { monitorId } = req.params;
|
const notifications = req.body.notifications;
|
||||||
const monitorBeforeEdit = await req.db.getMonitorById(monitorId);
|
|
||||||
|
|
||||||
// Get notifications from the request body
|
const editedMonitor = await this.db.editMonitor(monitorId, req.body);
|
||||||
const notifications = req.body.notifications;
|
|
||||||
|
|
||||||
const editedMonitor = await req.db.editMonitor(monitorId, req.body);
|
await this.db.deleteNotificationsByMonitorId(editedMonitor._id);
|
||||||
|
|
||||||
await req.db.deleteNotificationsByMonitorId(editedMonitor._id);
|
await Promise.all(
|
||||||
|
notifications &&
|
||||||
|
notifications.map(async (notification) => {
|
||||||
|
notification.monitorId = editedMonitor._id;
|
||||||
|
await this.db.createNotification(notification);
|
||||||
|
})
|
||||||
|
);
|
||||||
|
|
||||||
await Promise.all(
|
// Delete the old job(editedMonitor has the same ID as the old monitor)
|
||||||
notifications &&
|
await this.jobQueue.deleteJob(monitorBeforeEdit);
|
||||||
notifications.map(async (notification) => {
|
// Add the new job back to the queue
|
||||||
notification.monitorId = editedMonitor._id;
|
await this.jobQueue.addJob(editedMonitor._id, editedMonitor);
|
||||||
await req.db.createNotification(notification);
|
return res.status(200).json({
|
||||||
})
|
success: true,
|
||||||
);
|
msg: successMessages.MONITOR_EDIT,
|
||||||
|
data: editedMonitor,
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "editMonitor"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
// Delete the old job(editedMonitor has the same ID as the old monitor)
|
/**
|
||||||
await req.jobQueue.deleteJob(monitorBeforeEdit);
|
* Pauses or resumes a monitor based on its current state.
|
||||||
// Add the new job back to the queue
|
* @async
|
||||||
await req.jobQueue.addJob(editedMonitor._id, editedMonitor);
|
* @param {Object} req - The Express request object.
|
||||||
return res.status(200).json({
|
* @property {Object} req.params - The parameters of the request.
|
||||||
success: true,
|
* @property {string} req.params.monitorId - The ID of the monitor to be paused or resumed.
|
||||||
msg: successMessages.MONITOR_EDIT,
|
* @param {Object} res - The Express response object.
|
||||||
data: editedMonitor,
|
* @param {function} next - The next middleware function.
|
||||||
});
|
* @returns {Object} The response object with a success status, a message indicating the new state of the monitor, and the updated monitor data.
|
||||||
} catch (error) {
|
* @throws {Error} If there is an error during the process.
|
||||||
next(handleError(error, SERVICE_NAME, "editMonitor"));
|
*/
|
||||||
}
|
pauseMonitor = async (req, res, next) => {
|
||||||
};
|
try {
|
||||||
|
await pauseMonitorParamValidation.validateAsync(req.params);
|
||||||
|
} catch (error) {
|
||||||
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
|
}
|
||||||
|
|
||||||
/**
|
try {
|
||||||
* Pauses or resumes a monitor based on its current state.
|
const monitor = await this.db.getMonitorById(req.params.monitorId);
|
||||||
* @async
|
monitor.isActive === true
|
||||||
* @param {Object} req - The Express request object.
|
? await this.jobQueue.deleteJob(monitor)
|
||||||
* @property {Object} req.params - The parameters of the request.
|
: await this.jobQueue.addJob(monitor._id, monitor);
|
||||||
* @property {string} req.params.monitorId - The ID of the monitor to be paused or resumed.
|
|
||||||
* @param {Object} res - The Express response object.
|
|
||||||
* @param {function} next - The next middleware function.
|
|
||||||
* @returns {Object} The response object with a success status, a message indicating the new state of the monitor, and the updated monitor data.
|
|
||||||
* @throws {Error} If there is an error during the process.
|
|
||||||
*/
|
|
||||||
const pauseMonitor = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
await pauseMonitorParamValidation.validateAsync(req.params);
|
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
}
|
|
||||||
|
|
||||||
try {
|
monitor.isActive = !monitor.isActive;
|
||||||
const monitor = await req.db.getMonitorById(req.params.monitorId);
|
monitor.status = undefined;
|
||||||
monitor.isActive === true
|
monitor.save();
|
||||||
? await req.jobQueue.deleteJob(monitor)
|
return res.status(200).json({
|
||||||
: await req.jobQueue.addJob(monitor._id, monitor);
|
success: true,
|
||||||
|
msg: monitor.isActive
|
||||||
|
? successMessages.MONITOR_RESUME
|
||||||
|
: successMessages.MONITOR_PAUSE,
|
||||||
|
data: monitor,
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "pauseMonitor"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
monitor.isActive = !monitor.isActive;
|
/**
|
||||||
monitor.status = undefined;
|
* Adds demo monitors for a team.
|
||||||
monitor.save();
|
* @async
|
||||||
return res.status(200).json({
|
* @param {Object} req - The Express request object.
|
||||||
success: true,
|
* @property {Object} req.headers - The headers of the request.
|
||||||
msg: monitor.isActive
|
* @property {string} req.headers.authorization - The authorization header containing the JWT token.
|
||||||
? successMessages.MONITOR_RESUME
|
* @param {Object} res - The Express response object.
|
||||||
: successMessages.MONITOR_PAUSE,
|
* @param {function} next - The next middleware function.
|
||||||
data: monitor,
|
* @returns {Object} The response object with a success status, a message indicating the addition of demo monitors, and the number of demo monitors added.
|
||||||
});
|
* @throws {Error} If there is an error during the process.
|
||||||
} catch (error) {
|
*/
|
||||||
next(handleError(error, SERVICE_NAME, "pauseMonitor"));
|
addDemoMonitors = async (req, res, next) => {
|
||||||
}
|
try {
|
||||||
};
|
const token = getTokenFromHeaders(req.headers);
|
||||||
|
const { jwtSecret } = this.settingsService.getSettings();
|
||||||
|
const { _id, teamId } = jwt.verify(token, jwtSecret);
|
||||||
|
const demoMonitors = await this.db.addDemoMonitors(_id, teamId);
|
||||||
|
await Promise.all(
|
||||||
|
demoMonitors.map((monitor) => this.jobQueue.addJob(monitor._id, monitor))
|
||||||
|
);
|
||||||
|
|
||||||
/**
|
return res.status(200).json({
|
||||||
* Adds demo monitors for a team.
|
success: true,
|
||||||
* @async
|
msg: successMessages.MONITOR_DEMO_ADDED,
|
||||||
* @param {Object} req - The Express request object.
|
data: demoMonitors.length,
|
||||||
* @property {Object} req.headers - The headers of the request.
|
});
|
||||||
* @property {string} req.headers.authorization - The authorization header containing the JWT token.
|
} catch (error) {
|
||||||
* @param {Object} res - The Express response object.
|
next(handleError(error, SERVICE_NAME, "addDemoMonitors"));
|
||||||
* @param {function} next - The next middleware function.
|
}
|
||||||
* @returns {Object} The response object with a success status, a message indicating the addition of demo monitors, and the number of demo monitors added.
|
};
|
||||||
* @throws {Error} If there is an error during the process.
|
}
|
||||||
*/
|
|
||||||
const addDemoMonitors = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
const token = getTokenFromHeaders(req.headers);
|
|
||||||
const { jwtSecret } = req.settingsService.getSettings();
|
|
||||||
const { _id, teamId } = jwt.verify(token, jwtSecret);
|
|
||||||
const demoMonitors = await req.db.addDemoMonitors(_id, teamId);
|
|
||||||
await Promise.all(
|
|
||||||
demoMonitors.map((monitor) => req.jobQueue.addJob(monitor._id, monitor))
|
|
||||||
);
|
|
||||||
|
|
||||||
return res.status(200).json({
|
export default MonitorController;
|
||||||
success: true,
|
|
||||||
msg: successMessages.MONITOR_DEMO_ADDED,
|
|
||||||
data: demoMonitors.length,
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "addDemoMonitors"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
export {
|
|
||||||
getAllMonitors,
|
|
||||||
getAllMonitorsWithUptimeStats,
|
|
||||||
getMonitorStatsById,
|
|
||||||
getMonitorCertificate,
|
|
||||||
getMonitorById,
|
|
||||||
getMonitorsAndSummaryByTeamId,
|
|
||||||
getMonitorsByTeamId,
|
|
||||||
createMonitor,
|
|
||||||
checkEndpointResolution,
|
|
||||||
deleteMonitor,
|
|
||||||
deleteAllMonitors,
|
|
||||||
editMonitor,
|
|
||||||
pauseMonitor,
|
|
||||||
addDemoMonitors,
|
|
||||||
};
|
|
||||||
@@ -1,57 +1,64 @@
|
|||||||
import { handleError } from "./controllerUtils.js";
|
import { handleError } from "./controllerUtils.js";
|
||||||
import { errorMessages, successMessages } from "../utils/messages.js";
|
import { successMessages } from "../utils/messages.js";
|
||||||
|
|
||||||
const SERVICE_NAME = "JobQueueController";
|
const SERVICE_NAME = "JobQueueController";
|
||||||
|
|
||||||
const getMetrics = async (req, res, next) => {
|
class JobQueueController {
|
||||||
try {
|
constructor(jobQueue) {
|
||||||
const metrics = await req.jobQueue.getMetrics();
|
this.jobQueue = jobQueue;
|
||||||
res.status(200).json({
|
|
||||||
success: true,
|
|
||||||
msg: successMessages.QUEUE_GET_METRICS,
|
|
||||||
data: metrics,
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "getMetrics"));
|
|
||||||
return;
|
|
||||||
}
|
}
|
||||||
};
|
|
||||||
|
|
||||||
const getJobs = async (req, res, next) => {
|
getMetrics = async (req, res, next) => {
|
||||||
try {
|
try {
|
||||||
const jobs = await req.jobQueue.getJobStats();
|
const metrics = await this.jobQueue.getMetrics();
|
||||||
return res.status(200).json({
|
res.status(200).json({
|
||||||
success: true,
|
success: true,
|
||||||
msg: successMessages.QUEUE_GET_METRICS,
|
msg: successMessages.QUEUE_GET_METRICS,
|
||||||
data: jobs,
|
data: metrics,
|
||||||
});
|
});
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleError(error, SERVICE_NAME, "getJobs"));
|
next(handleError(error, SERVICE_NAME, "getMetrics"));
|
||||||
return;
|
return;
|
||||||
}
|
}
|
||||||
};
|
};
|
||||||
|
|
||||||
const addJob = async (req, res, next) => {
|
getJobs = async (req, res, next) => {
|
||||||
try {
|
try {
|
||||||
await req.jobQueue.addJob(Math.random().toString(36).substring(7));
|
const jobs = await this.jobQueue.getJobStats();
|
||||||
return res.status(200).json({
|
return res.status(200).json({
|
||||||
success: true,
|
success: true,
|
||||||
msg: successMessages.QUEUE_ADD_JOB,
|
msg: successMessages.QUEUE_GET_METRICS,
|
||||||
});
|
data: jobs,
|
||||||
} catch (error) {
|
});
|
||||||
next(handleError(error, SERVICE_NAME, "addJob"));
|
} catch (error) {
|
||||||
return;
|
next(handleError(error, SERVICE_NAME, "getJobs"));
|
||||||
}
|
return;
|
||||||
};
|
}
|
||||||
|
};
|
||||||
|
|
||||||
const obliterateQueue = async (req, res, next) => {
|
addJob = async (req, res, next) => {
|
||||||
try {
|
try {
|
||||||
await req.jobQueue.obliterate();
|
await this.jobQueue.addJob(Math.random().toString(36).substring(7));
|
||||||
return res.status(200).json({ success: true, msg: successMessages.QUEUE_OBLITERATE });
|
return res.status(200).json({
|
||||||
} catch (error) {
|
success: true,
|
||||||
next(handleError(error, SERVICE_NAME, "obliterateQueue"));
|
msg: successMessages.QUEUE_ADD_JOB,
|
||||||
return;
|
});
|
||||||
}
|
} catch (error) {
|
||||||
};
|
next(handleError(error, SERVICE_NAME, "addJob"));
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
};
|
||||||
|
|
||||||
export { getMetrics, getJobs, addJob, obliterateQueue };
|
obliterateQueue = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await this.jobQueue.obliterate();
|
||||||
|
return res
|
||||||
|
.status(200)
|
||||||
|
.json({ success: true, msg: successMessages.QUEUE_OBLITERATE });
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "obliterateQueue"));
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
};
|
||||||
|
}
|
||||||
|
export default JobQueueController;
|
||||||
@@ -3,40 +3,47 @@ import { updateAppSettingsBodyValidation } from "../validation/joi.js";
|
|||||||
import { handleValidationError, handleError } from "./controllerUtils.js";
|
import { handleValidationError, handleError } from "./controllerUtils.js";
|
||||||
const SERVICE_NAME = "SettingsController";
|
const SERVICE_NAME = "SettingsController";
|
||||||
|
|
||||||
const getAppSettings = async (req, res, next) => {
|
class SettingsController {
|
||||||
try {
|
constructor(db, settingsService) {
|
||||||
const settings = { ...(await req.settingsService.getSettings()) };
|
this.db = db;
|
||||||
delete settings.jwtSecret;
|
this.settingsService = settingsService;
|
||||||
return res.status(200).json({
|
|
||||||
success: true,
|
|
||||||
msg: successMessages.GET_APP_SETTINGS,
|
|
||||||
data: settings,
|
|
||||||
});
|
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "getAppSettings"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
const updateAppSettings = async (req, res, next) => {
|
|
||||||
try {
|
|
||||||
await updateAppSettingsBodyValidation.validateAsync(req.body);
|
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
}
|
||||||
|
|
||||||
try {
|
getAppSettings = async (req, res, next) => {
|
||||||
await req.db.updateAppSettings(req.body);
|
try {
|
||||||
const updatedSettings = { ...(await req.settingsService.reloadSettings()) };
|
const settings = { ...(await this.settingsService.getSettings()) };
|
||||||
delete updatedSettings.jwtSecret;
|
delete settings.jwtSecret;
|
||||||
return res.status(200).json({
|
return res.status(200).json({
|
||||||
success: true,
|
success: true,
|
||||||
msg: successMessages.UPDATE_APP_SETTINGS,
|
msg: successMessages.GET_APP_SETTINGS,
|
||||||
data: updatedSettings,
|
data: settings,
|
||||||
});
|
});
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleError(error, SERVICE_NAME, "updateAppSettings"));
|
next(handleError(error, SERVICE_NAME, "getAppSettings"));
|
||||||
}
|
}
|
||||||
};
|
};
|
||||||
|
|
||||||
export { getAppSettings, updateAppSettings };
|
updateAppSettings = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await updateAppSettingsBodyValidation.validateAsync(req.body);
|
||||||
|
} catch (error) {
|
||||||
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
|
||||||
|
try {
|
||||||
|
await this.db.updateAppSettings(req.body);
|
||||||
|
const updatedSettings = { ...(await this.settingsService.reloadSettings()) };
|
||||||
|
delete updatedSettings.jwtSecret;
|
||||||
|
return res.status(200).json({
|
||||||
|
success: true,
|
||||||
|
msg: successMessages.UPDATE_APP_SETTINGS,
|
||||||
|
data: updatedSettings,
|
||||||
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "updateAppSettings"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
}
|
||||||
|
|
||||||
|
export default SettingsController;
|
||||||
@@ -7,45 +7,50 @@ import { successMessages } from "../utils/messages.js";
|
|||||||
|
|
||||||
const SERVICE_NAME = "statusPageController";
|
const SERVICE_NAME = "statusPageController";
|
||||||
|
|
||||||
const createStatusPage = async (req, res, next) => {
|
class StatusPageController {
|
||||||
try {
|
constructor(db) {
|
||||||
await createStatusPageBodyValidation.validateAsync(req.body);
|
this.db = db;
|
||||||
} catch (error) {
|
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
|
||||||
return;
|
|
||||||
}
|
}
|
||||||
|
|
||||||
try {
|
createStatusPage = async (req, res, next) => {
|
||||||
const statusPage = await req.db.createStatusPage(req.body);
|
try {
|
||||||
return res.status(200).json({
|
await createStatusPageBodyValidation.validateAsync(req.body);
|
||||||
success: true,
|
} catch (error) {
|
||||||
msg: successMessages.STATUS_PAGE_CREATE,
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
data: statusPage,
|
return;
|
||||||
});
|
}
|
||||||
} catch (error) {
|
|
||||||
next(handleError(error, SERVICE_NAME, "createStatusPage"));
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
const getStatusPageByUrl = async (req, res, next) => {
|
try {
|
||||||
try {
|
const statusPage = await this.db.createStatusPage(req.body);
|
||||||
await getStatusPageParamValidation.validateAsync(req.params);
|
return res.status(200).json({
|
||||||
} catch (error) {
|
success: true,
|
||||||
next(handleValidationError(error, SERVICE_NAME));
|
msg: successMessages.STATUS_PAGE_CREATE,
|
||||||
return;
|
data: statusPage,
|
||||||
}
|
});
|
||||||
|
} catch (error) {
|
||||||
|
next(handleError(error, SERVICE_NAME, "createStatusPage"));
|
||||||
|
}
|
||||||
|
};
|
||||||
|
getStatusPageByUrl = async (req, res, next) => {
|
||||||
|
try {
|
||||||
|
await getStatusPageParamValidation.validateAsync(req.params);
|
||||||
|
} catch (error) {
|
||||||
|
next(handleValidationError(error, SERVICE_NAME));
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
|
||||||
try {
|
try {
|
||||||
const { url } = req.params;
|
const { url } = req.params;
|
||||||
const statusPage = await req.db.getStatusPageByUrl(url);
|
const statusPage = await this.db.getStatusPageByUrl(url);
|
||||||
return res.status(200).json({
|
return res.status(200).json({
|
||||||
success: true,
|
success: true,
|
||||||
msg: successMessages.STATUS_PAGE_BY_URL,
|
msg: successMessages.STATUS_PAGE_BY_URL,
|
||||||
data: statusPage,
|
data: statusPage,
|
||||||
});
|
});
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
next(handleError(error, SERVICE_NAME, "getStatusPage"));
|
next(handleError(error, SERVICE_NAME, "getStatusPage"));
|
||||||
}
|
}
|
||||||
};
|
};
|
||||||
|
}
|
||||||
|
|
||||||
export { createStatusPage, getStatusPageByUrl };
|
export default StatusPageController;
|
||||||
@@ -28,12 +28,15 @@ const MonitorSchema = mongoose.Schema(
|
|||||||
type: {
|
type: {
|
||||||
type: String,
|
type: String,
|
||||||
required: true,
|
required: true,
|
||||||
enum: ["http", "ping", "pagespeed", "hardware", "docker"],
|
enum: ["http", "ping", "pagespeed", "hardware", "docker", "port"],
|
||||||
},
|
},
|
||||||
url: {
|
url: {
|
||||||
type: String,
|
type: String,
|
||||||
required: true,
|
required: true,
|
||||||
},
|
},
|
||||||
|
port: {
|
||||||
|
type: Number,
|
||||||
|
},
|
||||||
isActive: {
|
isActive: {
|
||||||
type: Boolean,
|
type: Boolean,
|
||||||
default: true,
|
default: true,
|
||||||
|
|||||||
+76
-181
@@ -2,234 +2,129 @@ import mongoose from "mongoose";
|
|||||||
import UserModel from "../models/User.js";
|
import UserModel from "../models/User.js";
|
||||||
import AppSettings from "../models/AppSettings.js";
|
import AppSettings from "../models/AppSettings.js";
|
||||||
import logger from "../../utils/logger.js";
|
import logger from "../../utils/logger.js";
|
||||||
const SERVICE_NAME = "MongoDB";
|
|
||||||
|
|
||||||
//****************************************
|
|
||||||
// DB Connection
|
|
||||||
//****************************************
|
|
||||||
|
|
||||||
const connect = async () => {
|
|
||||||
try {
|
|
||||||
const connectionString =
|
|
||||||
process.env.DB_CONNECTION_STRING || "mongodb://localhost:27017/uptime_db";
|
|
||||||
await mongoose.connect(connectionString);
|
|
||||||
// If there are no AppSettings, create one
|
|
||||||
let appSettings = await AppSettings.find();
|
|
||||||
if (appSettings.length === 0) {
|
|
||||||
appSettings = new AppSettings({});
|
|
||||||
await appSettings.save();
|
|
||||||
}
|
|
||||||
logger.info({ message: "Connected to MongoDB" });
|
|
||||||
} catch (error) {
|
|
||||||
logger.error({
|
|
||||||
message: error.message,
|
|
||||||
service: SERVICE_NAME,
|
|
||||||
method: "connect",
|
|
||||||
stack: error.stack,
|
|
||||||
});
|
|
||||||
throw error;
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
const disconnect = async () => {
|
|
||||||
try {
|
|
||||||
logger.info({ message: "Disconnecting from MongoDB" });
|
|
||||||
await mongoose.disconnect();
|
|
||||||
logger.info({ message: "Disconnected from MongoDB" });
|
|
||||||
return;
|
|
||||||
} catch (error) {
|
|
||||||
logger.error({
|
|
||||||
message: error.message,
|
|
||||||
service: SERVICE_NAME,
|
|
||||||
method: "disconnect",
|
|
||||||
stack: error.stack,
|
|
||||||
});
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
const checkSuperadmin = async (req, res) => {
|
|
||||||
try {
|
|
||||||
const superAdmin = await UserModel.findOne({ role: "superadmin" });
|
|
||||||
if (superAdmin !== null) {
|
|
||||||
return true;
|
|
||||||
}
|
|
||||||
return false;
|
|
||||||
} catch (error) {
|
|
||||||
throw error;
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
//****************************************
|
//****************************************
|
||||||
// User Operations
|
// User Operations
|
||||||
//****************************************
|
//****************************************
|
||||||
|
|
||||||
import {
|
import * as userModule from "./modules/userModule.js";
|
||||||
insertUser,
|
|
||||||
getUserByEmail,
|
|
||||||
updateUser,
|
|
||||||
deleteUser,
|
|
||||||
deleteTeam,
|
|
||||||
deleteAllOtherUsers,
|
|
||||||
getAllUsers,
|
|
||||||
logoutUser,
|
|
||||||
} from "./modules/userModule.js";
|
|
||||||
|
|
||||||
//****************************************
|
//****************************************
|
||||||
// Invite Token Operations
|
// Invite Token Operations
|
||||||
//****************************************
|
//****************************************
|
||||||
|
|
||||||
import {
|
import * as inviteModule from "./modules/inviteModule.js";
|
||||||
requestInviteToken,
|
|
||||||
getInviteToken,
|
|
||||||
getInviteTokenAndDelete,
|
|
||||||
} from "./modules/inviteModule.js";
|
|
||||||
|
|
||||||
//****************************************
|
//****************************************
|
||||||
// Recovery Operations
|
// Recovery Operations
|
||||||
//****************************************
|
//****************************************
|
||||||
import {
|
import * as recoveryModule from "./modules/recoveryModule.js";
|
||||||
requestRecoveryToken,
|
|
||||||
validateRecoveryToken,
|
|
||||||
resetPassword,
|
|
||||||
} from "./modules/recoveryModule.js";
|
|
||||||
|
|
||||||
//****************************************
|
//****************************************
|
||||||
// Monitors
|
// Monitors
|
||||||
//****************************************
|
//****************************************
|
||||||
|
|
||||||
import {
|
import * as monitorModule from "./modules/monitorModule.js";
|
||||||
getAllMonitors,
|
|
||||||
getAllMonitorsWithUptimeStats,
|
|
||||||
getMonitorStatsById,
|
|
||||||
getMonitorById,
|
|
||||||
getMonitorsAndSummaryByTeamId,
|
|
||||||
getMonitorsByTeamId,
|
|
||||||
createMonitor,
|
|
||||||
deleteMonitor,
|
|
||||||
deleteAllMonitors,
|
|
||||||
deleteMonitorsByUserId,
|
|
||||||
editMonitor,
|
|
||||||
addDemoMonitors,
|
|
||||||
} from "./modules/monitorModule.js";
|
|
||||||
|
|
||||||
//****************************************
|
//****************************************
|
||||||
// Page Speed Checks
|
// Page Speed Checks
|
||||||
//****************************************
|
//****************************************
|
||||||
|
|
||||||
import {
|
import * as pageSpeedCheckModule from "./modules/pageSpeedCheckModule.js";
|
||||||
createPageSpeedCheck,
|
|
||||||
deletePageSpeedChecksByMonitorId,
|
|
||||||
} from "./modules/pageSpeedCheckModule.js";
|
|
||||||
|
|
||||||
//****************************************
|
//****************************************
|
||||||
// Hardware Checks
|
// Hardware Checks
|
||||||
//****************************************
|
//****************************************
|
||||||
import {
|
import * as hardwareCheckModule from "./modules/hardwareCheckModule.js";
|
||||||
createHardwareCheck,
|
|
||||||
deleteHardwareChecksByMonitorId,
|
|
||||||
} from "./modules/hardwareCheckModule.js";
|
|
||||||
|
|
||||||
//****************************************
|
//****************************************
|
||||||
// Checks
|
// Checks
|
||||||
//****************************************
|
//****************************************
|
||||||
|
|
||||||
import {
|
import * as checkModule from "./modules/checkModule.js";
|
||||||
createCheck,
|
|
||||||
getChecksCount,
|
|
||||||
getChecks,
|
|
||||||
getTeamChecks,
|
|
||||||
deleteChecks,
|
|
||||||
deleteChecksByTeamId,
|
|
||||||
updateChecksTTL,
|
|
||||||
} from "./modules/checkModule.js";
|
|
||||||
|
|
||||||
//****************************************
|
//****************************************
|
||||||
// Maintenance Window
|
// Maintenance Window
|
||||||
//****************************************
|
//****************************************
|
||||||
import {
|
import * as maintenanceWindowModule from "./modules/maintenanceWindowModule.js";
|
||||||
createMaintenanceWindow,
|
|
||||||
getMaintenanceWindowById,
|
|
||||||
getMaintenanceWindowsByTeamId,
|
|
||||||
getMaintenanceWindowsByMonitorId,
|
|
||||||
deleteMaintenanceWindowById,
|
|
||||||
deleteMaintenanceWindowByMonitorId,
|
|
||||||
deleteMaintenanceWindowByUserId,
|
|
||||||
editMaintenanceWindowById,
|
|
||||||
} from "./modules/maintenanceWindowModule.js";
|
|
||||||
|
|
||||||
//****************************************
|
//****************************************
|
||||||
// Notifications
|
// Notifications
|
||||||
//****************************************
|
//****************************************
|
||||||
import {
|
import * as notificationModule from "./modules/notificationModule.js";
|
||||||
createNotification,
|
|
||||||
getNotificationsByMonitorId,
|
|
||||||
deleteNotificationsByMonitorId,
|
|
||||||
} from "./modules/notificationModule.js";
|
|
||||||
|
|
||||||
//****************************************
|
//****************************************
|
||||||
// AppSettings
|
// AppSettings
|
||||||
//****************************************
|
//****************************************
|
||||||
import { getAppSettings, updateAppSettings } from "./modules/settingsModule.js";
|
import * as settingsModule from "./modules/settingsModule.js";
|
||||||
|
|
||||||
//****************************************
|
//****************************************
|
||||||
// Status Page
|
// Status Page
|
||||||
//****************************************
|
//****************************************
|
||||||
import { createStatusPage, getStatusPageByUrl } from "./modules/statusPageModule.js";
|
import * as statusPageModule from "./modules/statusPageModule.js";
|
||||||
|
|
||||||
export default {
|
class MongoDB {
|
||||||
connect,
|
static SERVICE_NAME = "MongoDB";
|
||||||
disconnect,
|
|
||||||
insertUser,
|
constructor() {
|
||||||
getUserByEmail,
|
Object.assign(this, userModule);
|
||||||
updateUser,
|
Object.assign(this, inviteModule);
|
||||||
deleteUser,
|
Object.assign(this, recoveryModule);
|
||||||
deleteTeam,
|
Object.assign(this, monitorModule);
|
||||||
deleteAllOtherUsers,
|
Object.assign(this, pageSpeedCheckModule);
|
||||||
getAllUsers,
|
Object.assign(this, hardwareCheckModule);
|
||||||
logoutUser,
|
Object.assign(this, checkModule);
|
||||||
requestInviteToken,
|
Object.assign(this, maintenanceWindowModule);
|
||||||
getInviteToken,
|
Object.assign(this, notificationModule);
|
||||||
getInviteTokenAndDelete,
|
Object.assign(this, settingsModule);
|
||||||
requestRecoveryToken,
|
Object.assign(this, statusPageModule);
|
||||||
validateRecoveryToken,
|
}
|
||||||
resetPassword,
|
|
||||||
checkSuperadmin,
|
connect = async () => {
|
||||||
getAllMonitors,
|
try {
|
||||||
getAllMonitorsWithUptimeStats,
|
const connectionString =
|
||||||
getMonitorStatsById,
|
process.env.DB_CONNECTION_STRING || "mongodb://localhost:27017/uptime_db";
|
||||||
getMonitorById,
|
await mongoose.connect(connectionString);
|
||||||
getMonitorsAndSummaryByTeamId,
|
// If there are no AppSettings, create one
|
||||||
getMonitorsByTeamId,
|
let appSettings = await AppSettings.find();
|
||||||
createMonitor,
|
if (appSettings.length === 0) {
|
||||||
deleteMonitor,
|
appSettings = new AppSettings({});
|
||||||
deleteAllMonitors,
|
await appSettings.save();
|
||||||
editMonitor,
|
}
|
||||||
addDemoMonitors,
|
logger.info({ message: "Connected to MongoDB" });
|
||||||
createCheck,
|
} catch (error) {
|
||||||
getChecksCount,
|
logger.error({
|
||||||
getChecks,
|
message: error.message,
|
||||||
getTeamChecks,
|
service: this.SERVICE_NAME,
|
||||||
deleteChecks,
|
method: "connect",
|
||||||
deleteChecksByTeamId,
|
stack: error.stack,
|
||||||
updateChecksTTL,
|
});
|
||||||
deleteMonitorsByUserId,
|
throw error;
|
||||||
createPageSpeedCheck,
|
}
|
||||||
deletePageSpeedChecksByMonitorId,
|
};
|
||||||
createHardwareCheck,
|
|
||||||
deleteHardwareChecksByMonitorId,
|
disconnect = async () => {
|
||||||
createMaintenanceWindow,
|
try {
|
||||||
getMaintenanceWindowsByTeamId,
|
logger.info({ message: "Disconnecting from MongoDB" });
|
||||||
getMaintenanceWindowById,
|
await mongoose.disconnect();
|
||||||
getMaintenanceWindowsByMonitorId,
|
logger.info({ message: "Disconnected from MongoDB" });
|
||||||
deleteMaintenanceWindowById,
|
return;
|
||||||
deleteMaintenanceWindowByMonitorId,
|
} catch (error) {
|
||||||
deleteMaintenanceWindowByUserId,
|
logger.error({
|
||||||
editMaintenanceWindowById,
|
message: error.message,
|
||||||
createNotification,
|
service: this.SERVICE_NAME,
|
||||||
getNotificationsByMonitorId,
|
method: "disconnect",
|
||||||
deleteNotificationsByMonitorId,
|
stack: error.stack,
|
||||||
getAppSettings,
|
});
|
||||||
updateAppSettings,
|
}
|
||||||
createStatusPage,
|
};
|
||||||
getStatusPageByUrl,
|
checkSuperadmin = async (req, res) => {
|
||||||
};
|
const superAdmin = await UserModel.findOne({ role: "superadmin" });
|
||||||
|
if (superAdmin !== null) {
|
||||||
|
return true;
|
||||||
|
}
|
||||||
|
return false;
|
||||||
|
};
|
||||||
|
}
|
||||||
|
|
||||||
|
export default MongoDB;
|
||||||
@@ -21,6 +21,7 @@ const CHECK_MODEL_LOOKUP = {
|
|||||||
http: Check,
|
http: Check,
|
||||||
ping: Check,
|
ping: Check,
|
||||||
docker: Check,
|
docker: Check,
|
||||||
|
port: Check,
|
||||||
pagespeed: PageSpeedCheck,
|
pagespeed: PageSpeedCheck,
|
||||||
hardware: HardwareCheck,
|
hardware: HardwareCheck,
|
||||||
};
|
};
|
||||||
@@ -351,7 +352,12 @@ const getMonitorStatsById = async (req) => {
|
|||||||
),
|
),
|
||||||
};
|
};
|
||||||
|
|
||||||
if (monitor.type === "http" || monitor.type === "ping" || monitor.type === "docker") {
|
if (
|
||||||
|
monitor.type === "http" ||
|
||||||
|
monitor.type === "ping" ||
|
||||||
|
monitor.type === "docker" ||
|
||||||
|
monitor.type === "port"
|
||||||
|
) {
|
||||||
// HTTP/PING Specific stats
|
// HTTP/PING Specific stats
|
||||||
monitorStats.periodAvgResponseTime = getAverageResponseTime(checksForDateRange);
|
monitorStats.periodAvgResponseTime = getAverageResponseTime(checksForDateRange);
|
||||||
monitorStats.periodUptime = getUptimePercentage(checksForDateRange);
|
monitorStats.periodUptime = getUptimePercentage(checksForDateRange);
|
||||||
|
|||||||
+151
-114
@@ -8,16 +8,31 @@ import cors from "cors";
|
|||||||
import logger from "./utils/logger.js";
|
import logger from "./utils/logger.js";
|
||||||
import { verifyJWT } from "./middleware/verifyJWT.js";
|
import { verifyJWT } from "./middleware/verifyJWT.js";
|
||||||
import { handleErrors } from "./middleware/handleErrors.js";
|
import { handleErrors } from "./middleware/handleErrors.js";
|
||||||
import authRouter from "./routes/authRoute.js";
|
|
||||||
import inviteRouter from "./routes/inviteRoute.js";
|
|
||||||
import monitorRouter from "./routes/monitorRoute.js";
|
|
||||||
import checkRouter from "./routes/checkRoute.js";
|
|
||||||
import maintenanceWindowRouter from "./routes/maintenanceWindowRoute.js";
|
|
||||||
import settingsRouter from "./routes/settingsRoute.js";
|
|
||||||
import statusPageRouter from "./routes/statusPageRoute.js";
|
|
||||||
import { fileURLToPath } from "url";
|
import { fileURLToPath } from "url";
|
||||||
|
|
||||||
import queueRouter from "./routes/queueRoute.js";
|
import AuthRoutes from "./routes/authRoute.js";
|
||||||
|
import AuthController from "./controllers/authController.js";
|
||||||
|
|
||||||
|
import InviteRoutes from "./routes/inviteRoute.js";
|
||||||
|
import InviteController from "./controllers/inviteController.js";
|
||||||
|
|
||||||
|
import MonitorRoutes from "./routes/monitorRoute.js";
|
||||||
|
import MonitorController from "./controllers/monitorController.js";
|
||||||
|
|
||||||
|
import CheckRoutes from "./routes/checkRoute.js";
|
||||||
|
import CheckController from "./controllers/checkController.js";
|
||||||
|
|
||||||
|
import MaintenanceWindowRoutes from "./routes/maintenanceWindowRoute.js";
|
||||||
|
import MaintenanceWindowController from "./controllers/maintenanceWindowController.js";
|
||||||
|
|
||||||
|
import SettingsRoutes from "./routes/settingsRoute.js";
|
||||||
|
import SettingsController from "./controllers/settingsController.js";
|
||||||
|
|
||||||
|
import StatusPageRoutes from "./routes/statusPageRoute.js";
|
||||||
|
import StatusPageController from "./controllers/statusPageController.js";
|
||||||
|
|
||||||
|
import QueueRoutes from "./routes/queueRoute.js";
|
||||||
|
import QueueController from "./controllers/queueController.js";
|
||||||
|
|
||||||
//JobQueue service and dependencies
|
//JobQueue service and dependencies
|
||||||
import JobQueue from "./service/jobQueue.js";
|
import JobQueue from "./service/jobQueue.js";
|
||||||
@@ -29,6 +44,7 @@ import axios from "axios";
|
|||||||
import ping from "ping";
|
import ping from "ping";
|
||||||
import http from "http";
|
import http from "http";
|
||||||
import Docker from "dockerode";
|
import Docker from "dockerode";
|
||||||
|
import net from "net";
|
||||||
|
|
||||||
// Email service and dependencies
|
// Email service and dependencies
|
||||||
import EmailService from "./service/emailService.js";
|
import EmailService from "./service/emailService.js";
|
||||||
@@ -41,102 +57,68 @@ import mjml2html from "mjml";
|
|||||||
import SettingsService from "./service/settingsService.js";
|
import SettingsService from "./service/settingsService.js";
|
||||||
import AppSettings from "./db/models/AppSettings.js";
|
import AppSettings from "./db/models/AppSettings.js";
|
||||||
|
|
||||||
|
// Status Service and dependencies
|
||||||
import StatusService from "./service/statusService.js";
|
import StatusService from "./service/statusService.js";
|
||||||
|
|
||||||
|
// Notification Service and dependencies
|
||||||
import NotificationService from "./service/notificationService.js";
|
import NotificationService from "./service/notificationService.js";
|
||||||
|
|
||||||
import db from "./db/mongo/MongoDB.js";
|
// Service Registry
|
||||||
|
import ServiceRegistry from "./service/serviceRegistry.js";
|
||||||
|
|
||||||
|
import MongoDB from "./db/mongo/MongoDB.js";
|
||||||
|
|
||||||
const SERVICE_NAME = "Server";
|
const SERVICE_NAME = "Server";
|
||||||
const SHUTDOWN_TIMEOUT = 1000;
|
const SHUTDOWN_TIMEOUT = 1000;
|
||||||
|
|
||||||
let isShuttingDown = false;
|
let isShuttingDown = false;
|
||||||
const __filename = fileURLToPath(import.meta.url);
|
const __filename = fileURLToPath(import.meta.url);
|
||||||
const __dirname = path.dirname(__filename);
|
const __dirname = path.dirname(__filename);
|
||||||
|
|
||||||
const openApiSpec = JSON.parse(
|
const openApiSpec = JSON.parse(
|
||||||
fs.readFileSync(path.join(__dirname, "openapi.json"), "utf8")
|
fs.readFileSync(path.join(__dirname, "openapi.json"), "utf8")
|
||||||
);
|
);
|
||||||
|
|
||||||
|
let server;
|
||||||
|
|
||||||
const PORT = 5000;
|
const PORT = 5000;
|
||||||
|
|
||||||
|
const shutdown = async () => {
|
||||||
|
if (isShuttingDown) {
|
||||||
|
return;
|
||||||
|
}
|
||||||
|
isShuttingDown = true;
|
||||||
|
logger.info({ message: "Attempting graceful shutdown" });
|
||||||
|
setTimeout(() => {
|
||||||
|
logger.error({
|
||||||
|
message: "Could not shut down in time, forcing shutdown",
|
||||||
|
service: SERVICE_NAME,
|
||||||
|
method: "shutdown",
|
||||||
|
});
|
||||||
|
process.exit(1);
|
||||||
|
}, SHUTDOWN_TIMEOUT);
|
||||||
|
try {
|
||||||
|
server.close();
|
||||||
|
await ServiceRegistry.get(JobQueue.SERVICE_NAME).obliterate();
|
||||||
|
await ServiceRegistry.get(MongoDB.SERVICE_NAME).disconnect();
|
||||||
|
logger.info({ message: "Graceful shutdown complete" });
|
||||||
|
process.exit(0);
|
||||||
|
} catch (error) {
|
||||||
|
logger.error({
|
||||||
|
message: error.message,
|
||||||
|
service: SERVICE_NAME,
|
||||||
|
method: "shutdown",
|
||||||
|
stack: error.stack,
|
||||||
|
});
|
||||||
|
}
|
||||||
|
};
|
||||||
// Need to wrap server setup in a function to handle async nature of JobQueue
|
// Need to wrap server setup in a function to handle async nature of JobQueue
|
||||||
const startApp = async () => {
|
const startApp = async () => {
|
||||||
const app = express();
|
const app = express();
|
||||||
|
|
||||||
// middlewares
|
// Create DB
|
||||||
app.use(
|
const db = new MongoDB();
|
||||||
cors()
|
await db.connect();
|
||||||
//We will add configuration later
|
|
||||||
);
|
|
||||||
app.use(express.json());
|
|
||||||
app.use(helmet());
|
|
||||||
|
|
||||||
// Add db, jobQueue, emailService, and settingsService to request object for easy access
|
|
||||||
app.use((req, res, next) => {
|
|
||||||
req.db = db;
|
|
||||||
req.jobQueue = jobQueue;
|
|
||||||
req.emailService = emailService;
|
|
||||||
req.settingsService = settingsService;
|
|
||||||
next();
|
|
||||||
});
|
|
||||||
|
|
||||||
// Swagger UI
|
|
||||||
app.use("/api-docs", swaggerUi.serve, swaggerUi.setup(openApiSpec));
|
|
||||||
|
|
||||||
//routes
|
|
||||||
app.use("/api/v1/auth", authRouter);
|
|
||||||
app.use("/api/v1/settings", verifyJWT, settingsRouter);
|
|
||||||
app.use("/api/v1/invite", inviteRouter);
|
|
||||||
app.use("/api/v1/monitors", verifyJWT, monitorRouter);
|
|
||||||
app.use("/api/v1/checks", verifyJWT, checkRouter);
|
|
||||||
app.use("/api/v1/maintenance-window", verifyJWT, maintenanceWindowRouter);
|
|
||||||
app.use("/api/v1/queue", verifyJWT, queueRouter);
|
|
||||||
app.use("/api/v1/status-page", statusPageRouter);
|
|
||||||
|
|
||||||
app.use("/api/v1/dummy-data", async (req, res) => {
|
|
||||||
try {
|
|
||||||
const response = await axios.get(
|
|
||||||
"https://gist.githubusercontent.com/ajhollid/9afa39410c7bbf52cc905f285a2225bf/raw/429a231a3559ebc95f6f488ed2c766bd7d6f46e5/dummyData.json",
|
|
||||||
{
|
|
||||||
headers: {
|
|
||||||
"Content-Type": "application/json",
|
|
||||||
"Cache-Control": "no-cache",
|
|
||||||
},
|
|
||||||
}
|
|
||||||
);
|
|
||||||
return res.status(200).json(response.data);
|
|
||||||
} catch (error) {
|
|
||||||
return res.status(500).json({ message: error.message });
|
|
||||||
}
|
|
||||||
});
|
|
||||||
|
|
||||||
//health check
|
|
||||||
app.use("/api/v1/healthy", (req, res) => {
|
|
||||||
try {
|
|
||||||
logger.info({ message: "Checking Health of the server." });
|
|
||||||
return res.status(200).json({ message: "Healthy" });
|
|
||||||
} catch (error) {
|
|
||||||
logger.error({
|
|
||||||
message: error.message,
|
|
||||||
service: SERVICE_NAME,
|
|
||||||
method: "healthCheck",
|
|
||||||
stack: error.stack,
|
|
||||||
});
|
|
||||||
return res.status(500).json({ message: error.message });
|
|
||||||
}
|
|
||||||
});
|
|
||||||
|
|
||||||
/**
|
|
||||||
* Error handler middleware
|
|
||||||
* Should be called last
|
|
||||||
*/
|
|
||||||
app.use(handleErrors);
|
|
||||||
|
|
||||||
// Create services
|
// Create services
|
||||||
await db.connect();
|
|
||||||
const server = app.listen(PORT, () => {
|
|
||||||
logger.info({ message: `server started on port:${PORT}` });
|
|
||||||
});
|
|
||||||
|
|
||||||
const settingsService = new SettingsService(AppSettings);
|
const settingsService = new SettingsService(AppSettings);
|
||||||
await settingsService.loadSettings();
|
await settingsService.loadSettings();
|
||||||
const emailService = new EmailService(
|
const emailService = new EmailService(
|
||||||
@@ -148,7 +130,7 @@ const startApp = async () => {
|
|||||||
nodemailer,
|
nodemailer,
|
||||||
logger
|
logger
|
||||||
);
|
);
|
||||||
const networkService = new NetworkService(axios, ping, logger, http, Docker);
|
const networkService = new NetworkService(axios, ping, logger, http, Docker, net);
|
||||||
const statusService = new StatusService(db, logger);
|
const statusService = new StatusService(db, logger);
|
||||||
const notificationService = new NotificationService(emailService, db, logger);
|
const notificationService = new NotificationService(emailService, db, logger);
|
||||||
const jobQueue = await JobQueue.createJobQueue(
|
const jobQueue = await JobQueue.createJobQueue(
|
||||||
@@ -162,39 +144,94 @@ const startApp = async () => {
|
|||||||
Worker
|
Worker
|
||||||
);
|
);
|
||||||
|
|
||||||
const shutdown = async () => {
|
// Register services
|
||||||
if (isShuttingDown) {
|
ServiceRegistry.register(JobQueue.SERVICE_NAME, jobQueue);
|
||||||
return;
|
ServiceRegistry.register(MongoDB.SERVICE_NAME, db);
|
||||||
}
|
ServiceRegistry.register(SettingsService.SERVICE_NAME, settingsService);
|
||||||
isShuttingDown = true;
|
ServiceRegistry.register(EmailService.SERVICE_NAME, emailService);
|
||||||
logger.info({ message: "Attempting graceful shutdown" });
|
ServiceRegistry.register(NetworkService.SERVICE_NAME, networkService);
|
||||||
setTimeout(() => {
|
ServiceRegistry.register(StatusService.SERVICE_NAME, statusService);
|
||||||
logger.error({
|
ServiceRegistry.register(NotificationService.SERVICE_NAME, notificationService);
|
||||||
message: "Could not shut down in time, forcing shutdown",
|
server = app.listen(PORT, () => {
|
||||||
service: SERVICE_NAME,
|
logger.info({ message: `server started on port:${PORT}` });
|
||||||
method: "shutdown",
|
});
|
||||||
});
|
|
||||||
process.exit(1);
|
|
||||||
}, SHUTDOWN_TIMEOUT);
|
|
||||||
try {
|
|
||||||
server.close();
|
|
||||||
await jobQueue.obliterate();
|
|
||||||
await db.disconnect();
|
|
||||||
logger.info({ message: "Graceful shutdown complete" });
|
|
||||||
process.exit(0);
|
|
||||||
} catch (error) {
|
|
||||||
logger.error({
|
|
||||||
message: error.message,
|
|
||||||
service: SERVICE_NAME,
|
|
||||||
method: "shutdown",
|
|
||||||
stack: error.stack,
|
|
||||||
});
|
|
||||||
}
|
|
||||||
};
|
|
||||||
|
|
||||||
process.on("SIGUSR2", shutdown);
|
process.on("SIGUSR2", shutdown);
|
||||||
process.on("SIGINT", shutdown);
|
process.on("SIGINT", shutdown);
|
||||||
process.on("SIGTERM", shutdown);
|
process.on("SIGTERM", shutdown);
|
||||||
|
|
||||||
|
//Create controllers
|
||||||
|
const authController = new AuthController(
|
||||||
|
ServiceRegistry.get(MongoDB.SERVICE_NAME),
|
||||||
|
ServiceRegistry.get(SettingsService.SERVICE_NAME),
|
||||||
|
ServiceRegistry.get(EmailService.SERVICE_NAME),
|
||||||
|
ServiceRegistry.get(JobQueue.SERVICE_NAME)
|
||||||
|
);
|
||||||
|
|
||||||
|
const monitorController = new MonitorController(
|
||||||
|
ServiceRegistry.get(MongoDB.SERVICE_NAME),
|
||||||
|
ServiceRegistry.get(SettingsService.SERVICE_NAME),
|
||||||
|
ServiceRegistry.get(JobQueue.SERVICE_NAME)
|
||||||
|
);
|
||||||
|
|
||||||
|
const settingsController = new SettingsController(
|
||||||
|
ServiceRegistry.get(MongoDB.SERVICE_NAME),
|
||||||
|
ServiceRegistry.get(SettingsService.SERVICE_NAME)
|
||||||
|
);
|
||||||
|
|
||||||
|
const checkController = new CheckController(
|
||||||
|
ServiceRegistry.get(MongoDB.SERVICE_NAME),
|
||||||
|
ServiceRegistry.get(SettingsService.SERVICE_NAME)
|
||||||
|
);
|
||||||
|
|
||||||
|
const inviteController = new InviteController(
|
||||||
|
ServiceRegistry.get(MongoDB.SERVICE_NAME),
|
||||||
|
ServiceRegistry.get(SettingsService.SERVICE_NAME),
|
||||||
|
ServiceRegistry.get(EmailService.SERVICE_NAME)
|
||||||
|
);
|
||||||
|
|
||||||
|
const maintenanceWindowController = new MaintenanceWindowController(
|
||||||
|
ServiceRegistry.get(MongoDB.SERVICE_NAME),
|
||||||
|
ServiceRegistry.get(SettingsService.SERVICE_NAME)
|
||||||
|
);
|
||||||
|
|
||||||
|
const queueController = new QueueController(ServiceRegistry.get(JobQueue.SERVICE_NAME));
|
||||||
|
|
||||||
|
const statusPageController = new StatusPageController(
|
||||||
|
ServiceRegistry.get(MongoDB.SERVICE_NAME)
|
||||||
|
);
|
||||||
|
|
||||||
|
//Create routes
|
||||||
|
const authRoutes = new AuthRoutes(authController);
|
||||||
|
const monitorRoutes = new MonitorRoutes(monitorController);
|
||||||
|
const settingsRoutes = new SettingsRoutes(settingsController);
|
||||||
|
const checkRoutes = new CheckRoutes(checkController);
|
||||||
|
const inviteRoutes = new InviteRoutes(inviteController);
|
||||||
|
const maintenanceWindowRoutes = new MaintenanceWindowRoutes(
|
||||||
|
maintenanceWindowController
|
||||||
|
);
|
||||||
|
const queueRoutes = new QueueRoutes(queueController);
|
||||||
|
const statusPageRoutes = new StatusPageRoutes(statusPageController);
|
||||||
|
// Middleware
|
||||||
|
app.use(
|
||||||
|
cors()
|
||||||
|
//We will add configuration later
|
||||||
|
);
|
||||||
|
app.use(express.json());
|
||||||
|
app.use(helmet());
|
||||||
|
// Swagger UI
|
||||||
|
app.use("/api-docs", swaggerUi.serve, swaggerUi.setup(openApiSpec));
|
||||||
|
|
||||||
|
//routes
|
||||||
|
app.use("/api/v1/auth", authRoutes.getRouter());
|
||||||
|
app.use("/api/v1/settings", verifyJWT, settingsRoutes.getRouter());
|
||||||
|
app.use("/api/v1/invite", inviteRoutes.getRouter());
|
||||||
|
app.use("/api/v1/monitors", verifyJWT, monitorRoutes.getRouter());
|
||||||
|
app.use("/api/v1/checks", verifyJWT, checkRoutes.getRouter());
|
||||||
|
app.use("/api/v1/maintenance-window", verifyJWT, maintenanceWindowRoutes.getRouter());
|
||||||
|
app.use("/api/v1/queue", verifyJWT, queueRoutes.getRouter());
|
||||||
|
app.use("/api/v1/status-page", statusPageRoutes.getRouter());
|
||||||
|
app.use(handleErrors);
|
||||||
};
|
};
|
||||||
|
|
||||||
startApp().catch((error) => {
|
startApp().catch((error) => {
|
||||||
|
|||||||
@@ -1,6 +1,9 @@
|
|||||||
import jwt from "jsonwebtoken";
|
import jwt from "jsonwebtoken";
|
||||||
const TOKEN_PREFIX = "Bearer ";
|
const TOKEN_PREFIX = "Bearer ";
|
||||||
const SERVICE_NAME = "allowedRoles";
|
const SERVICE_NAME = "allowedRoles";
|
||||||
|
import ServiceRegistry from "../service/serviceRegistry.js";
|
||||||
|
import SettingsService from "../service/settingsService.js";
|
||||||
|
|
||||||
import { errorMessages } from "../utils/messages.js";
|
import { errorMessages } from "../utils/messages.js";
|
||||||
|
|
||||||
const isAllowed = (allowedRoles) => {
|
const isAllowed = (allowedRoles) => {
|
||||||
@@ -27,7 +30,9 @@ const isAllowed = (allowedRoles) => {
|
|||||||
// Parse the token
|
// Parse the token
|
||||||
try {
|
try {
|
||||||
const parsedToken = token.slice(TOKEN_PREFIX.length, token.length);
|
const parsedToken = token.slice(TOKEN_PREFIX.length, token.length);
|
||||||
const { jwtSecret } = req.settingsService.getSettings();
|
const { jwtSecret } = ServiceRegistry.get(
|
||||||
|
SettingsService.SERVICE_NAME
|
||||||
|
).getSettings();
|
||||||
var decoded = jwt.verify(parsedToken, jwtSecret);
|
var decoded = jwt.verify(parsedToken, jwtSecret);
|
||||||
const userRoles = decoded.role;
|
const userRoles = decoded.role;
|
||||||
|
|
||||||
|
|||||||
@@ -1,6 +1,7 @@
|
|||||||
import jwt from "jsonwebtoken";
|
import jwt from "jsonwebtoken";
|
||||||
import { errorMessages } from "../utils/messages.js";
|
import { errorMessages } from "../utils/messages.js";
|
||||||
|
import ServiceRegistry from "../service/serviceRegistry.js";
|
||||||
|
import SettingsService from "../service/settingsService.js";
|
||||||
const SERVICE_NAME = "verifyJWT";
|
const SERVICE_NAME = "verifyJWT";
|
||||||
const TOKEN_PREFIX = "Bearer ";
|
const TOKEN_PREFIX = "Bearer ";
|
||||||
|
|
||||||
@@ -34,7 +35,7 @@ const verifyJWT = (req, res, next) => {
|
|||||||
|
|
||||||
const parsedToken = token.slice(TOKEN_PREFIX.length, token.length);
|
const parsedToken = token.slice(TOKEN_PREFIX.length, token.length);
|
||||||
// Verify the token's authenticity
|
// Verify the token's authenticity
|
||||||
const { jwtSecret } = req.settingsService.getSettings();
|
const { jwtSecret } = ServiceRegistry.get(SettingsService.SERVICE_NAME).getSettings();
|
||||||
jwt.verify(parsedToken, jwtSecret, (err, decoded) => {
|
jwt.verify(parsedToken, jwtSecret, (err, decoded) => {
|
||||||
if (err) {
|
if (err) {
|
||||||
if (err.name === "TokenExpiredError") {
|
if (err.name === "TokenExpiredError") {
|
||||||
@@ -67,7 +68,9 @@ function handleExpiredJwtToken(req, res, next) {
|
|||||||
}
|
}
|
||||||
|
|
||||||
// Verify refresh token
|
// Verify refresh token
|
||||||
const { refreshTokenSecret } = req.settingsService.getSettings();
|
const { refreshTokenSecret } = ServiceRegistry.get(
|
||||||
|
SettingsService.SERVICE_NAME
|
||||||
|
).getSettings();
|
||||||
jwt.verify(refreshToken, refreshTokenSecret, (refreshErr, refreshDecoded) => {
|
jwt.verify(refreshToken, refreshTokenSecret, (refreshErr, refreshDecoded) => {
|
||||||
if (refreshErr) {
|
if (refreshErr) {
|
||||||
// Invalid or expired refresh token, trigger logout
|
// Invalid or expired refresh token, trigger logout
|
||||||
|
|||||||
@@ -3,6 +3,8 @@ const logger = require("../utils/logger");
|
|||||||
const SERVICE_NAME = "verifyAdmin";
|
const SERVICE_NAME = "verifyAdmin";
|
||||||
const TOKEN_PREFIX = "Bearer ";
|
const TOKEN_PREFIX = "Bearer ";
|
||||||
const { errorMessages } = require("../utils/messages");
|
const { errorMessages } = require("../utils/messages");
|
||||||
|
import ServiceRegistry from "../service/serviceRegistry.js";
|
||||||
|
import SettingsService from "../service/settingsService.js";
|
||||||
/**
|
/**
|
||||||
* Verifies the JWT token
|
* Verifies the JWT token
|
||||||
* @function
|
* @function
|
||||||
@@ -33,7 +35,7 @@ const verifySuperAdmin = (req, res, next) => {
|
|||||||
|
|
||||||
const parsedToken = token.slice(TOKEN_PREFIX.length, token.length);
|
const parsedToken = token.slice(TOKEN_PREFIX.length, token.length);
|
||||||
// verify admin role is present
|
// verify admin role is present
|
||||||
const { jwtSecret } = req.settingsService.getSettings();
|
const { jwtSecret } = ServiceRegistry.get(SettingsService.SERVICE_NAME).getSettings();
|
||||||
|
|
||||||
jwt.verify(parsedToken, jwtSecret, (err, decoded) => {
|
jwt.verify(parsedToken, jwtSecret, (err, decoded) => {
|
||||||
if (err) {
|
if (err) {
|
||||||
|
|||||||
Generated
+83
-21
@@ -11,7 +11,7 @@
|
|||||||
"dependencies": {
|
"dependencies": {
|
||||||
"axios": "^1.7.2",
|
"axios": "^1.7.2",
|
||||||
"bcrypt": "5.1.1",
|
"bcrypt": "5.1.1",
|
||||||
"bullmq": "5.34.4",
|
"bullmq": "5.34.5",
|
||||||
"cors": "^2.8.5",
|
"cors": "^2.8.5",
|
||||||
"dockerode": "4.0.2",
|
"dockerode": "4.0.2",
|
||||||
"dotenv": "^16.4.5",
|
"dotenv": "^16.4.5",
|
||||||
@@ -179,6 +179,17 @@
|
|||||||
"node": "^18.18.0 || ^20.9.0 || >=21.1.0"
|
"node": "^18.18.0 || ^20.9.0 || >=21.1.0"
|
||||||
}
|
}
|
||||||
},
|
},
|
||||||
|
"node_modules/@eslint/config-array/node_modules/brace-expansion": {
|
||||||
|
"version": "1.1.11",
|
||||||
|
"resolved": "https://registry.npmjs.org/brace-expansion/-/brace-expansion-1.1.11.tgz",
|
||||||
|
"integrity": "sha512-iCuPHDFgrHX7H2vEI/5xpz07zSHB00TpugqhmYtVmMO6518mCuRMoOYFldEBl0g187ufozdaHgWKcYFb61qGiA==",
|
||||||
|
"dev": true,
|
||||||
|
"license": "MIT",
|
||||||
|
"dependencies": {
|
||||||
|
"balanced-match": "^1.0.0",
|
||||||
|
"concat-map": "0.0.1"
|
||||||
|
}
|
||||||
|
},
|
||||||
"node_modules/@eslint/config-array/node_modules/debug": {
|
"node_modules/@eslint/config-array/node_modules/debug": {
|
||||||
"version": "4.4.0",
|
"version": "4.4.0",
|
||||||
"resolved": "https://registry.npmjs.org/debug/-/debug-4.4.0.tgz",
|
"resolved": "https://registry.npmjs.org/debug/-/debug-4.4.0.tgz",
|
||||||
@@ -196,6 +207,19 @@
|
|||||||
}
|
}
|
||||||
}
|
}
|
||||||
},
|
},
|
||||||
|
"node_modules/@eslint/config-array/node_modules/minimatch": {
|
||||||
|
"version": "3.1.2",
|
||||||
|
"resolved": "https://registry.npmjs.org/minimatch/-/minimatch-3.1.2.tgz",
|
||||||
|
"integrity": "sha512-J7p63hRiAjw1NDEww1W7i37+ByIrOWO5XQQAzZ3VOcL0PNybwpfmV/N05zFAzwQ9USyEcX6t3UO+K5aqBQOIHw==",
|
||||||
|
"dev": true,
|
||||||
|
"license": "ISC",
|
||||||
|
"dependencies": {
|
||||||
|
"brace-expansion": "^1.1.7"
|
||||||
|
},
|
||||||
|
"engines": {
|
||||||
|
"node": "*"
|
||||||
|
}
|
||||||
|
},
|
||||||
"node_modules/@eslint/config-array/node_modules/ms": {
|
"node_modules/@eslint/config-array/node_modules/ms": {
|
||||||
"version": "2.1.3",
|
"version": "2.1.3",
|
||||||
"resolved": "https://registry.npmjs.org/ms/-/ms-2.1.3.tgz",
|
"resolved": "https://registry.npmjs.org/ms/-/ms-2.1.3.tgz",
|
||||||
@@ -237,6 +261,17 @@
|
|||||||
"url": "https://opencollective.com/eslint"
|
"url": "https://opencollective.com/eslint"
|
||||||
}
|
}
|
||||||
},
|
},
|
||||||
|
"node_modules/@eslint/eslintrc/node_modules/brace-expansion": {
|
||||||
|
"version": "1.1.11",
|
||||||
|
"resolved": "https://registry.npmjs.org/brace-expansion/-/brace-expansion-1.1.11.tgz",
|
||||||
|
"integrity": "sha512-iCuPHDFgrHX7H2vEI/5xpz07zSHB00TpugqhmYtVmMO6518mCuRMoOYFldEBl0g187ufozdaHgWKcYFb61qGiA==",
|
||||||
|
"dev": true,
|
||||||
|
"license": "MIT",
|
||||||
|
"dependencies": {
|
||||||
|
"balanced-match": "^1.0.0",
|
||||||
|
"concat-map": "0.0.1"
|
||||||
|
}
|
||||||
|
},
|
||||||
"node_modules/@eslint/eslintrc/node_modules/debug": {
|
"node_modules/@eslint/eslintrc/node_modules/debug": {
|
||||||
"version": "4.4.0",
|
"version": "4.4.0",
|
||||||
"resolved": "https://registry.npmjs.org/debug/-/debug-4.4.0.tgz",
|
"resolved": "https://registry.npmjs.org/debug/-/debug-4.4.0.tgz",
|
||||||
@@ -266,6 +301,19 @@
|
|||||||
"url": "https://github.com/sponsors/sindresorhus"
|
"url": "https://github.com/sponsors/sindresorhus"
|
||||||
}
|
}
|
||||||
},
|
},
|
||||||
|
"node_modules/@eslint/eslintrc/node_modules/minimatch": {
|
||||||
|
"version": "3.1.2",
|
||||||
|
"resolved": "https://registry.npmjs.org/minimatch/-/minimatch-3.1.2.tgz",
|
||||||
|
"integrity": "sha512-J7p63hRiAjw1NDEww1W7i37+ByIrOWO5XQQAzZ3VOcL0PNybwpfmV/N05zFAzwQ9USyEcX6t3UO+K5aqBQOIHw==",
|
||||||
|
"dev": true,
|
||||||
|
"license": "ISC",
|
||||||
|
"dependencies": {
|
||||||
|
"brace-expansion": "^1.1.7"
|
||||||
|
},
|
||||||
|
"engines": {
|
||||||
|
"node": "*"
|
||||||
|
}
|
||||||
|
},
|
||||||
"node_modules/@eslint/eslintrc/node_modules/ms": {
|
"node_modules/@eslint/eslintrc/node_modules/ms": {
|
||||||
"version": "2.1.3",
|
"version": "2.1.3",
|
||||||
"resolved": "https://registry.npmjs.org/ms/-/ms-2.1.3.tgz",
|
"resolved": "https://registry.npmjs.org/ms/-/ms-2.1.3.tgz",
|
||||||
@@ -1493,12 +1541,12 @@
|
|||||||
}
|
}
|
||||||
},
|
},
|
||||||
"node_modules/bullmq": {
|
"node_modules/bullmq": {
|
||||||
"version": "5.34.4",
|
"version": "5.34.5",
|
||||||
"resolved": "https://registry.npmjs.org/bullmq/-/bullmq-5.34.4.tgz",
|
"resolved": "https://registry.npmjs.org/bullmq/-/bullmq-5.34.5.tgz",
|
||||||
"integrity": "sha512-FPTN5eqsYO5/Blm6vh/bVJ0eADrVLjTBDjMkPCqZN3xx/5GqHov9NwxM6A6M3m6n2Vg+gNAoN98t7bTij5/UEA==",
|
"integrity": "sha512-MHho9EOhLCTY3ZF+dd0wHv0VlY2FtpBcopMRsvj0kPra4TAwBFh2pik/s4WbX56cIfCE+VzfHIHy4xvqp3g1+Q==",
|
||||||
"license": "MIT",
|
"license": "MIT",
|
||||||
"dependencies": {
|
"dependencies": {
|
||||||
"cron-parser": "^4.6.0",
|
"cron-parser": "^4.9.0",
|
||||||
"ioredis": "^5.4.1",
|
"ioredis": "^5.4.1",
|
||||||
"msgpackr": "^1.11.2",
|
"msgpackr": "^1.11.2",
|
||||||
"node-abort-controller": "^3.1.1",
|
"node-abort-controller": "^3.1.1",
|
||||||
@@ -2357,22 +2405,6 @@
|
|||||||
"integrity": "sha512-oIPzksmTg4/MriiaYGO+okXDT7ztn/w3Eptv/+gSIdMdKsJo0u4CfYNFJPy+4SKMuCqGw2wxnA+URMg3t8a/bQ==",
|
"integrity": "sha512-oIPzksmTg4/MriiaYGO+okXDT7ztn/w3Eptv/+gSIdMdKsJo0u4CfYNFJPy+4SKMuCqGw2wxnA+URMg3t8a/bQ==",
|
||||||
"dev": true
|
"dev": true
|
||||||
},
|
},
|
||||||
"node_modules/define-data-property": {
|
|
||||||
"version": "1.1.4",
|
|
||||||
"resolved": "https://registry.npmjs.org/define-data-property/-/define-data-property-1.1.4.tgz",
|
|
||||||
"integrity": "sha512-rBMvIzlpA8v6E+SJZoo++HAYqsLrkg7MSfIinMPFhmkorw7X+dOXVJQs+QT69zGkzMyfDnIMN2Wid1+NbL3T+A==",
|
|
||||||
"dependencies": {
|
|
||||||
"es-define-property": "^1.0.0",
|
|
||||||
"es-errors": "^1.3.0",
|
|
||||||
"gopd": "^1.0.1"
|
|
||||||
},
|
|
||||||
"engines": {
|
|
||||||
"node": ">= 0.4"
|
|
||||||
},
|
|
||||||
"funding": {
|
|
||||||
"url": "https://github.com/sponsors/ljharb"
|
|
||||||
}
|
|
||||||
},
|
|
||||||
"node_modules/delayed-stream": {
|
"node_modules/delayed-stream": {
|
||||||
"version": "1.0.0",
|
"version": "1.0.0",
|
||||||
"resolved": "https://registry.npmjs.org/delayed-stream/-/delayed-stream-1.0.0.tgz",
|
"resolved": "https://registry.npmjs.org/delayed-stream/-/delayed-stream-1.0.0.tgz",
|
||||||
@@ -2894,6 +2926,17 @@
|
|||||||
"url": "https://github.com/chalk/ansi-styles?sponsor=1"
|
"url": "https://github.com/chalk/ansi-styles?sponsor=1"
|
||||||
}
|
}
|
||||||
},
|
},
|
||||||
|
"node_modules/eslint/node_modules/brace-expansion": {
|
||||||
|
"version": "1.1.11",
|
||||||
|
"resolved": "https://registry.npmjs.org/brace-expansion/-/brace-expansion-1.1.11.tgz",
|
||||||
|
"integrity": "sha512-iCuPHDFgrHX7H2vEI/5xpz07zSHB00TpugqhmYtVmMO6518mCuRMoOYFldEBl0g187ufozdaHgWKcYFb61qGiA==",
|
||||||
|
"dev": true,
|
||||||
|
"license": "MIT",
|
||||||
|
"dependencies": {
|
||||||
|
"balanced-match": "^1.0.0",
|
||||||
|
"concat-map": "0.0.1"
|
||||||
|
}
|
||||||
|
},
|
||||||
"node_modules/eslint/node_modules/chalk": {
|
"node_modules/eslint/node_modules/chalk": {
|
||||||
"version": "4.1.2",
|
"version": "4.1.2",
|
||||||
"resolved": "https://registry.npmjs.org/chalk/-/chalk-4.1.2.tgz",
|
"resolved": "https://registry.npmjs.org/chalk/-/chalk-4.1.2.tgz",
|
||||||
@@ -2978,6 +3021,19 @@
|
|||||||
"node": ">=8"
|
"node": ">=8"
|
||||||
}
|
}
|
||||||
},
|
},
|
||||||
|
"node_modules/eslint/node_modules/minimatch": {
|
||||||
|
"version": "3.1.2",
|
||||||
|
"resolved": "https://registry.npmjs.org/minimatch/-/minimatch-3.1.2.tgz",
|
||||||
|
"integrity": "sha512-J7p63hRiAjw1NDEww1W7i37+ByIrOWO5XQQAzZ3VOcL0PNybwpfmV/N05zFAzwQ9USyEcX6t3UO+K5aqBQOIHw==",
|
||||||
|
"dev": true,
|
||||||
|
"license": "ISC",
|
||||||
|
"dependencies": {
|
||||||
|
"brace-expansion": "^1.1.7"
|
||||||
|
},
|
||||||
|
"engines": {
|
||||||
|
"node": "*"
|
||||||
|
}
|
||||||
|
},
|
||||||
"node_modules/eslint/node_modules/ms": {
|
"node_modules/eslint/node_modules/ms": {
|
||||||
"version": "2.1.3",
|
"version": "2.1.3",
|
||||||
"resolved": "https://registry.npmjs.org/ms/-/ms-2.1.3.tgz",
|
"resolved": "https://registry.npmjs.org/ms/-/ms-2.1.3.tgz",
|
||||||
@@ -8051,6 +8107,12 @@
|
|||||||
"node": ">=0.10.0"
|
"node": ">=0.10.0"
|
||||||
}
|
}
|
||||||
},
|
},
|
||||||
|
"node_modules/wordwrap": {
|
||||||
|
"version": "1.0.0",
|
||||||
|
"resolved": "https://registry.npmjs.org/wordwrap/-/wordwrap-1.0.0.tgz",
|
||||||
|
"integrity": "sha512-gvVzJFlPycKc5dZN4yPkP8w7Dc37BtP1yczEneOb4uq34pXZcvrtRTmWV8W+Ume+XCxKgbjM+nevkyFPMybd4Q==",
|
||||||
|
"license": "MIT"
|
||||||
|
},
|
||||||
"node_modules/workerpool": {
|
"node_modules/workerpool": {
|
||||||
"version": "6.5.1",
|
"version": "6.5.1",
|
||||||
"resolved": "https://registry.npmjs.org/workerpool/-/workerpool-6.5.1.tgz",
|
"resolved": "https://registry.npmjs.org/workerpool/-/workerpool-6.5.1.tgz",
|
||||||
|
|||||||
+1
-1
@@ -18,7 +18,7 @@
|
|||||||
"dependencies": {
|
"dependencies": {
|
||||||
"axios": "^1.7.2",
|
"axios": "^1.7.2",
|
||||||
"bcrypt": "5.1.1",
|
"bcrypt": "5.1.1",
|
||||||
"bullmq": "5.34.4",
|
"bullmq": "5.34.5",
|
||||||
"cors": "^2.8.5",
|
"cors": "^2.8.5",
|
||||||
"dockerode": "4.0.2",
|
"dockerode": "4.0.2",
|
||||||
"dotenv": "^16.4.5",
|
"dotenv": "^16.4.5",
|
||||||
|
|||||||
+48
-26
@@ -5,34 +5,56 @@ import { isAllowed } from "../middleware/isAllowed.js";
|
|||||||
import multer from "multer";
|
import multer from "multer";
|
||||||
import User from "../db/models/User.js";
|
import User from "../db/models/User.js";
|
||||||
|
|
||||||
const router = Router();
|
|
||||||
const upload = multer();
|
const upload = multer();
|
||||||
|
|
||||||
import {
|
class AuthRoutes {
|
||||||
registerUser,
|
constructor(authController) {
|
||||||
loginUser,
|
this.router = Router();
|
||||||
refreshAuthToken,
|
this.authController = authController;
|
||||||
editUser,
|
this.initRoutes();
|
||||||
requestRecovery,
|
}
|
||||||
validateRecovery,
|
|
||||||
resetPassword,
|
|
||||||
checkSuperadminExists,
|
|
||||||
getAllUsers,
|
|
||||||
deleteUser,
|
|
||||||
} from "../controllers/authController.js";
|
|
||||||
|
|
||||||
//Auth routes
|
initRoutes() {
|
||||||
router.post("/register", upload.single("profileImage"), registerUser);
|
this.router.post(
|
||||||
router.post("/login", loginUser);
|
"/register",
|
||||||
router.post("/refresh", refreshAuthToken);
|
upload.single("profileImage"),
|
||||||
router.put("/user/:userId", upload.single("profileImage"), verifyJWT, editUser);
|
this.authController.registerUser
|
||||||
router.get("/users/superadmin", checkSuperadminExists);
|
);
|
||||||
router.get("/users", verifyJWT, isAllowed(["admin", "superadmin"]), getAllUsers);
|
this.router.post("/login", this.authController.loginUser);
|
||||||
router.delete("/user/:userId", verifyJWT, verifyOwnership(User, "userId"), deleteUser);
|
this.router.post("/refresh", this.authController.refreshAuthToken);
|
||||||
|
|
||||||
//Recovery routes
|
this.router.put(
|
||||||
router.post("/recovery/request", requestRecovery);
|
"/user/:userId",
|
||||||
router.post("/recovery/validate", validateRecovery);
|
upload.single("profileImage"),
|
||||||
router.post("/recovery/reset/", resetPassword);
|
verifyJWT,
|
||||||
|
this.authController.editUser
|
||||||
|
);
|
||||||
|
|
||||||
export default router;
|
this.router.get("/users/superadmin", this.authController.checkSuperadminExists);
|
||||||
|
|
||||||
|
this.router.get(
|
||||||
|
"/users",
|
||||||
|
verifyJWT,
|
||||||
|
isAllowed(["admin", "superadmin"]),
|
||||||
|
this.authController.getAllUsers
|
||||||
|
);
|
||||||
|
|
||||||
|
this.router.delete(
|
||||||
|
"/user/:userId",
|
||||||
|
verifyJWT,
|
||||||
|
verifyOwnership(User, "userId"),
|
||||||
|
this.authController.deleteUser
|
||||||
|
);
|
||||||
|
|
||||||
|
// Recovery routes
|
||||||
|
this.router.post("/recovery/request", this.authController.requestRecovery);
|
||||||
|
this.router.post("/recovery/validate", this.authController.validateRecovery);
|
||||||
|
this.router.post("/recovery/reset/", this.authController.resetPassword);
|
||||||
|
}
|
||||||
|
|
||||||
|
getRouter() {
|
||||||
|
return this.router;
|
||||||
|
}
|
||||||
|
}
|
||||||
|
|
||||||
|
export default AuthRoutes;
|
||||||
+36
-16
@@ -1,26 +1,46 @@
|
|||||||
import { Router } from "express";
|
import { Router } from "express";
|
||||||
import {
|
|
||||||
createCheck,
|
|
||||||
getChecks,
|
|
||||||
deleteChecks,
|
|
||||||
getTeamChecks,
|
|
||||||
deleteChecksByTeamId,
|
|
||||||
updateChecksTTL,
|
|
||||||
} from "../controllers/checkController.js";
|
|
||||||
import { verifyOwnership } from "../middleware/verifyOwnership.js";
|
import { verifyOwnership } from "../middleware/verifyOwnership.js";
|
||||||
import { isAllowed } from "../middleware/isAllowed.js";
|
import { isAllowed } from "../middleware/isAllowed.js";
|
||||||
import Monitor from "../db/models/Monitor.js";
|
import Monitor from "../db/models/Monitor.js";
|
||||||
|
|
||||||
const router = Router();
|
class CheckRoutes {
|
||||||
|
constructor(checkController) {
|
||||||
|
this.router = Router();
|
||||||
|
this.checkController = checkController;
|
||||||
|
this.initRoutes();
|
||||||
|
}
|
||||||
|
|
||||||
router.get("/:monitorId", getChecks);
|
initRoutes() {
|
||||||
router.post("/:monitorId", verifyOwnership(Monitor, "monitorId"), createCheck);
|
this.router.get("/:monitorId", this.checkController.getChecks);
|
||||||
router.delete("/:monitorId", verifyOwnership(Monitor, "monitorId"), deleteChecks);
|
this.router.post(
|
||||||
|
"/:monitorId",
|
||||||
|
verifyOwnership(Monitor, "monitorId"),
|
||||||
|
this.checkController.createCheck
|
||||||
|
);
|
||||||
|
this.router.delete(
|
||||||
|
"/:monitorId",
|
||||||
|
verifyOwnership(Monitor, "monitorId"),
|
||||||
|
this.checkController.deleteChecks
|
||||||
|
);
|
||||||
|
|
||||||
router.get("/team/:teamId", getTeamChecks);
|
this.router.get("/team/:teamId", this.checkController.getTeamChecks);
|
||||||
|
|
||||||
router.delete("/team/:teamId", isAllowed(["admin", "superadmin"]), deleteChecksByTeamId);
|
this.router.delete(
|
||||||
|
"/team/:teamId",
|
||||||
|
isAllowed(["admin", "superadmin"]),
|
||||||
|
this.checkController.deleteChecksByTeamId
|
||||||
|
);
|
||||||
|
|
||||||
router.put("/team/ttl", isAllowed(["admin", "superadmin"]), updateChecksTTL);
|
this.router.put(
|
||||||
|
"/team/ttl",
|
||||||
|
isAllowed(["admin", "superadmin"]),
|
||||||
|
this.checkController.updateChecksTTL
|
||||||
|
);
|
||||||
|
}
|
||||||
|
|
||||||
export default router;
|
getRouter() {
|
||||||
|
return this.router;
|
||||||
|
}
|
||||||
|
}
|
||||||
|
|
||||||
|
export default CheckRoutes;
|
||||||
@@ -1,14 +1,27 @@
|
|||||||
import { Router } from "express";
|
import { Router } from "express";
|
||||||
import { verifyJWT } from "../middleware/verifyJWT.js";
|
import { verifyJWT } from "../middleware/verifyJWT.js";
|
||||||
import { isAllowed } from "../middleware/isAllowed.js";
|
import { isAllowed } from "../middleware/isAllowed.js";
|
||||||
import {
|
|
||||||
issueInvitation,
|
|
||||||
inviteVerifyController,
|
|
||||||
} from "../controllers/inviteController.js";
|
|
||||||
|
|
||||||
const router = Router();
|
class InviteRoutes {
|
||||||
|
constructor(inviteController) {
|
||||||
|
this.router = Router();
|
||||||
|
this.inviteController = inviteController;
|
||||||
|
this.initRoutes();
|
||||||
|
}
|
||||||
|
|
||||||
router.post("/", isAllowed(["admin", "superadmin"]), verifyJWT, issueInvitation);
|
initRoutes() {
|
||||||
router.post("/verify", inviteVerifyController);
|
this.router.post(
|
||||||
|
"/",
|
||||||
|
isAllowed(["admin", "superadmin"]),
|
||||||
|
verifyJWT,
|
||||||
|
this.inviteController.issueInvitation
|
||||||
|
);
|
||||||
|
this.router.post("/verify", this.inviteController.inviteVerifyController);
|
||||||
|
}
|
||||||
|
|
||||||
export default router;
|
getRouter() {
|
||||||
|
return this.router;
|
||||||
|
}
|
||||||
|
}
|
||||||
|
|
||||||
|
export default InviteRoutes;
|
||||||
@@ -1,31 +1,37 @@
|
|||||||
import { Router } from "express";
|
import { Router } from "express";
|
||||||
import {
|
|
||||||
createMaintenanceWindows,
|
|
||||||
getMaintenanceWindowById,
|
|
||||||
getMaintenanceWindowsByTeamId,
|
|
||||||
getMaintenanceWindowsByMonitorId,
|
|
||||||
deleteMaintenanceWindow,
|
|
||||||
editMaintenanceWindow,
|
|
||||||
} from "../controllers/maintenanceWindowController.js";
|
|
||||||
import { verifyOwnership } from "../middleware/verifyOwnership.js";
|
import { verifyOwnership } from "../middleware/verifyOwnership.js";
|
||||||
import Monitor from "../db/models/Monitor.js";
|
import Monitor from "../db/models/Monitor.js";
|
||||||
|
|
||||||
const router = Router();
|
class MaintenanceWindowRoutes {
|
||||||
|
constructor(maintenanceWindowController) {
|
||||||
|
this.router = Router();
|
||||||
|
this.maintenanceWindowController = maintenanceWindowController;
|
||||||
|
this.initRoutes();
|
||||||
|
}
|
||||||
|
initRoutes() {
|
||||||
|
this.router.post("/", this.maintenanceWindowController.createMaintenanceWindows);
|
||||||
|
|
||||||
router.post("/", createMaintenanceWindows);
|
this.router.get(
|
||||||
|
"/monitor/:monitorId",
|
||||||
|
verifyOwnership(Monitor, "monitorId"),
|
||||||
|
this.maintenanceWindowController.getMaintenanceWindowsByMonitorId
|
||||||
|
);
|
||||||
|
|
||||||
router.get(
|
this.router.get(
|
||||||
"/monitor/:monitorId",
|
"/team/",
|
||||||
verifyOwnership(Monitor, "monitorId"),
|
this.maintenanceWindowController.getMaintenanceWindowsByTeamId
|
||||||
getMaintenanceWindowsByMonitorId
|
);
|
||||||
);
|
|
||||||
|
|
||||||
router.get("/team/", getMaintenanceWindowsByTeamId);
|
this.router.get("/:id", this.maintenanceWindowController.getMaintenanceWindowById);
|
||||||
|
|
||||||
router.get("/:id", getMaintenanceWindowById);
|
this.router.put("/:id", this.maintenanceWindowController.editMaintenanceWindow);
|
||||||
|
|
||||||
router.put("/:id", editMaintenanceWindow);
|
this.router.delete("/:id", this.maintenanceWindowController.deleteMaintenanceWindow);
|
||||||
|
}
|
||||||
|
|
||||||
router.delete("/:id", deleteMaintenanceWindow);
|
getRouter() {
|
||||||
|
return this.router;
|
||||||
|
}
|
||||||
|
}
|
||||||
|
|
||||||
export default router;
|
export default MaintenanceWindowRoutes;
|
||||||
@@ -1,51 +1,79 @@
|
|||||||
import { Router } from "express";
|
import { Router } from "express";
|
||||||
import {
|
|
||||||
getAllMonitors,
|
|
||||||
getAllMonitorsWithUptimeStats,
|
|
||||||
getMonitorStatsById,
|
|
||||||
getMonitorCertificate,
|
|
||||||
getMonitorById,
|
|
||||||
getMonitorsAndSummaryByTeamId,
|
|
||||||
getMonitorsByTeamId,
|
|
||||||
createMonitor,
|
|
||||||
checkEndpointResolution,
|
|
||||||
deleteMonitor,
|
|
||||||
deleteAllMonitors,
|
|
||||||
editMonitor,
|
|
||||||
pauseMonitor,
|
|
||||||
addDemoMonitors,
|
|
||||||
} from "../controllers/monitorController.js";
|
|
||||||
import { isAllowed } from "../middleware/isAllowed.js";
|
import { isAllowed } from "../middleware/isAllowed.js";
|
||||||
import { fetchMonitorCertificate } from "../controllers/controllerUtils.js";
|
import { fetchMonitorCertificate } from "../controllers/controllerUtils.js";
|
||||||
|
|
||||||
const router = Router();
|
class MonitorRoutes {
|
||||||
|
constructor(monitorController) {
|
||||||
|
this.router = Router();
|
||||||
|
this.monitorController = monitorController;
|
||||||
|
this.initRoutes();
|
||||||
|
}
|
||||||
|
|
||||||
router.get("/", getAllMonitors);
|
initRoutes() {
|
||||||
router.get("/uptime", getAllMonitorsWithUptimeStats);
|
this.router.get("/", this.monitorController.getAllMonitors);
|
||||||
router.get("/stats/:monitorId", getMonitorStatsById);
|
this.router.get("/uptime", this.monitorController.getAllMonitorsWithUptimeStats);
|
||||||
router.get("/certificate/:monitorId", (req, res, next) => {
|
this.router.get("/stats/:monitorId", this.monitorController.getMonitorStatsById);
|
||||||
getMonitorCertificate(req, res, next, fetchMonitorCertificate);
|
this.router.get("/certificate/:monitorId", (req, res, next) => {
|
||||||
});
|
this.monitorController.getMonitorCertificate(
|
||||||
router.get("/:monitorId", getMonitorById);
|
req,
|
||||||
router.get("/team/summary/:teamId", getMonitorsAndSummaryByTeamId);
|
res,
|
||||||
router.get("/team/:teamId", getMonitorsByTeamId);
|
next,
|
||||||
|
fetchMonitorCertificate
|
||||||
|
);
|
||||||
|
});
|
||||||
|
this.router.get("/:monitorId", this.monitorController.getMonitorById);
|
||||||
|
this.router.get(
|
||||||
|
"/team/summary/:teamId",
|
||||||
|
this.monitorController.getMonitorsAndSummaryByTeamId
|
||||||
|
);
|
||||||
|
this.router.get("/team/:teamId", this.monitorController.getMonitorsByTeamId);
|
||||||
|
|
||||||
router.get(
|
this.router.get(
|
||||||
"/resolution/url",
|
"/resolution/url",
|
||||||
isAllowed(["admin", "superadmin"]),
|
isAllowed(["admin", "superadmin"]),
|
||||||
checkEndpointResolution
|
this.monitorController.checkEndpointResolution
|
||||||
);
|
);
|
||||||
|
|
||||||
router.delete("/:monitorId", isAllowed(["admin", "superadmin"]), deleteMonitor);
|
this.router.delete(
|
||||||
|
"/:monitorId",
|
||||||
|
isAllowed(["admin", "superadmin"]),
|
||||||
|
this.monitorController.deleteMonitor
|
||||||
|
);
|
||||||
|
|
||||||
router.post("/", isAllowed(["admin", "superadmin"]), createMonitor);
|
this.router.post(
|
||||||
|
"/",
|
||||||
|
isAllowed(["admin", "superadmin"]),
|
||||||
|
this.monitorController.createMonitor
|
||||||
|
);
|
||||||
|
|
||||||
router.put("/:monitorId", isAllowed(["admin", "superadmin"]), editMonitor);
|
this.router.put(
|
||||||
|
"/:monitorId",
|
||||||
|
isAllowed(["admin", "superadmin"]),
|
||||||
|
this.monitorController.editMonitor
|
||||||
|
);
|
||||||
|
|
||||||
router.delete("/", isAllowed(["superadmin"]), deleteAllMonitors);
|
this.router.delete(
|
||||||
|
"/",
|
||||||
|
isAllowed(["superadmin"]),
|
||||||
|
this.monitorController.deleteAllMonitors
|
||||||
|
);
|
||||||
|
|
||||||
router.post("/pause/:monitorId", isAllowed(["admin", "superadmin"]), pauseMonitor);
|
this.router.post(
|
||||||
|
"/pause/:monitorId",
|
||||||
|
isAllowed(["admin", "superadmin"]),
|
||||||
|
this.monitorController.pauseMonitor
|
||||||
|
);
|
||||||
|
|
||||||
router.post("/demo", isAllowed(["admin", "superadmin"]), addDemoMonitors);
|
this.router.post(
|
||||||
|
"/demo",
|
||||||
|
isAllowed(["admin", "superadmin"]),
|
||||||
|
this.monitorController.addDemoMonitors
|
||||||
|
);
|
||||||
|
}
|
||||||
|
|
||||||
export default router;
|
getRouter() {
|
||||||
|
return this.router;
|
||||||
|
}
|
||||||
|
}
|
||||||
|
|
||||||
|
export default MonitorRoutes;
|
||||||
+17
-17
@@ -1,21 +1,21 @@
|
|||||||
import { Router } from "express";
|
import { Router } from "express";
|
||||||
import {
|
|
||||||
getMetrics,
|
|
||||||
getJobs,
|
|
||||||
addJob,
|
|
||||||
obliterateQueue,
|
|
||||||
} from "../controllers/queueController.js";
|
|
||||||
|
|
||||||
const router = Router();
|
class QueueRoutes {
|
||||||
router.get("/metrics", getMetrics);
|
constructor(queueController) {
|
||||||
|
this.router = Router();
|
||||||
|
this.queueController = queueController;
|
||||||
|
this.initRoutes();
|
||||||
|
}
|
||||||
|
initRoutes() {
|
||||||
|
this.router.get("/metrics", this.queueController.getMetrics);
|
||||||
|
this.router.get("/jobs", this.queueController.getJobs);
|
||||||
|
this.router.post("/jobs", this.queueController.addJob);
|
||||||
|
this.router.post("/obliterate", this.queueController.obliterateQueue);
|
||||||
|
}
|
||||||
|
|
||||||
// Get Jobs
|
getRouter() {
|
||||||
router.get("/jobs", getJobs);
|
return this.router;
|
||||||
|
}
|
||||||
|
}
|
||||||
|
|
||||||
// Add Job
|
export default QueueRoutes;
|
||||||
router.post("/jobs", addJob);
|
|
||||||
|
|
||||||
// Obliterate Queue
|
|
||||||
router.post("/obliterate", obliterateQueue);
|
|
||||||
|
|
||||||
export default router;
|
|
||||||
@@ -1,10 +1,25 @@
|
|||||||
import { Router } from "express";
|
import { Router } from "express";
|
||||||
import { getAppSettings, updateAppSettings } from "../controllers/settingsController.js";
|
|
||||||
import { isAllowed } from "../middleware/isAllowed.js";
|
import { isAllowed } from "../middleware/isAllowed.js";
|
||||||
|
|
||||||
const router = Router();
|
class SettingsRoutes {
|
||||||
|
constructor(settingsController) {
|
||||||
|
this.router = Router();
|
||||||
|
this.settingsController = settingsController;
|
||||||
|
this.initRoutes();
|
||||||
|
}
|
||||||
|
|
||||||
router.get("/", getAppSettings);
|
initRoutes() {
|
||||||
router.put("/", isAllowed(["superadmin"]), updateAppSettings);
|
this.router.get("/", this.settingsController.getAppSettings);
|
||||||
|
this.router.put(
|
||||||
|
"/",
|
||||||
|
isAllowed(["superadmin"]),
|
||||||
|
this.settingsController.updateAppSettings
|
||||||
|
);
|
||||||
|
}
|
||||||
|
|
||||||
export default router;
|
getRouter() {
|
||||||
|
return this.router;
|
||||||
|
}
|
||||||
|
}
|
||||||
|
|
||||||
|
export default SettingsRoutes;
|
||||||
@@ -1,11 +1,22 @@
|
|||||||
import express from "express";
|
import { Router } from "express";
|
||||||
import { verifyJWT } from "../middleware/verifyJWT.js";
|
|
||||||
import {
|
|
||||||
createStatusPage,
|
|
||||||
getStatusPageByUrl,
|
|
||||||
} from "../controllers/statusPageController.js";
|
|
||||||
const router = express.Router();
|
|
||||||
|
|
||||||
router.get("/:url", getStatusPageByUrl);
|
import { verifyJWT } from "../middleware/verifyJWT.js";
|
||||||
router.post("/:url", verifyJWT, createStatusPage);
|
|
||||||
export default router;
|
class StatusPageRoutes {
|
||||||
|
constructor(statusPageController) {
|
||||||
|
this.router = Router();
|
||||||
|
this.statusPageController = statusPageController;
|
||||||
|
this.initRoutes();
|
||||||
|
}
|
||||||
|
|
||||||
|
initRoutes() {
|
||||||
|
this.router.get("/:url", this.statusPageController.getStatusPageByUrl);
|
||||||
|
this.router.post("/:url", verifyJWT, this.statusPageController.createStatusPage);
|
||||||
|
}
|
||||||
|
|
||||||
|
getRouter() {
|
||||||
|
return this.router;
|
||||||
|
}
|
||||||
|
}
|
||||||
|
|
||||||
|
export default StatusPageRoutes;
|
||||||
@@ -10,6 +10,7 @@ const SERVICE_NAME = "EmailService";
|
|||||||
* Represents an email service that can load templates, build, and send emails.
|
* Represents an email service that can load templates, build, and send emails.
|
||||||
*/
|
*/
|
||||||
class EmailService {
|
class EmailService {
|
||||||
|
static SERVICE_NAME = SERVICE_NAME;
|
||||||
/**
|
/**
|
||||||
* Constructs an instance of the EmailService, initializing template loaders and the email transporter.
|
* Constructs an instance of the EmailService, initializing template loaders and the email transporter.
|
||||||
* @param {Object} settingsService - The settings service to get email configuration.
|
* @param {Object} settingsService - The settings service to get email configuration.
|
||||||
|
|||||||
@@ -1,7 +1,8 @@
|
|||||||
const QUEUE_NAME = "monitors";
|
const QUEUE_NAME = "monitors";
|
||||||
const JOBS_PER_WORKER = 5;
|
const JOBS_PER_WORKER = 5;
|
||||||
import { errorMessages, successMessages } from "../utils/messages.js";
|
|
||||||
const SERVICE_NAME = "JobQueue";
|
const SERVICE_NAME = "JobQueue";
|
||||||
|
|
||||||
|
import { errorMessages, successMessages } from "../utils/messages.js";
|
||||||
/**
|
/**
|
||||||
* JobQueue
|
* JobQueue
|
||||||
*
|
*
|
||||||
@@ -10,6 +11,7 @@ const SERVICE_NAME = "JobQueue";
|
|||||||
* It scales the number of workers based on the number of jobs/worker
|
* It scales the number of workers based on the number of jobs/worker
|
||||||
*/
|
*/
|
||||||
class JobQueue {
|
class JobQueue {
|
||||||
|
static SERVICE_NAME = SERVICE_NAME;
|
||||||
/**
|
/**
|
||||||
* @class JobQueue
|
* @class JobQueue
|
||||||
* @classdesc Manages job queue and workers.
|
* @classdesc Manages job queue and workers.
|
||||||
@@ -88,11 +90,30 @@ class JobQueue {
|
|||||||
const monitors = await db.getAllMonitors();
|
const monitors = await db.getAllMonitors();
|
||||||
for (const monitor of monitors) {
|
for (const monitor of monitors) {
|
||||||
if (monitor.isActive) {
|
if (monitor.isActive) {
|
||||||
await queue.addJob(monitor.id, monitor);
|
queue.addJob(monitor.id, monitor).catch((error) => {
|
||||||
|
this.logger.error({
|
||||||
|
message: error.message,
|
||||||
|
service: SERVICE_NAME,
|
||||||
|
method: "createJobQueue",
|
||||||
|
stack: error.stack,
|
||||||
|
});
|
||||||
|
});
|
||||||
}
|
}
|
||||||
}
|
}
|
||||||
const workerStats = await queue.getWorkerStats();
|
|
||||||
await queue.scaleWorkers(workerStats);
|
queue
|
||||||
|
.getWorkerStats()
|
||||||
|
.then((workerStats) => {
|
||||||
|
queue.scaleWorkers(workerStats);
|
||||||
|
})
|
||||||
|
.catch((error) => {
|
||||||
|
this.logger.error({
|
||||||
|
message: error.message,
|
||||||
|
service: SERVICE_NAME,
|
||||||
|
method: "createJobQueue",
|
||||||
|
stack: error.stack,
|
||||||
|
});
|
||||||
|
});
|
||||||
return queue;
|
return queue;
|
||||||
} catch (error) {
|
} catch (error) {
|
||||||
error.service === undefined ? (error.service = SERVICE_NAME) : null;
|
error.service === undefined ? (error.service = SERVICE_NAME) : null;
|
||||||
|
|||||||
@@ -1,4 +1,6 @@
|
|||||||
import { errorMessages, successMessages } from "../utils/messages.js";
|
import { errorMessages, successMessages } from "../utils/messages.js";
|
||||||
|
const SERVICE_NAME = "NetworkService";
|
||||||
|
|
||||||
/**
|
/**
|
||||||
* Constructs a new NetworkService instance.
|
* Constructs a new NetworkService instance.
|
||||||
*
|
*
|
||||||
@@ -6,15 +8,18 @@ import { errorMessages, successMessages } from "../utils/messages.js";
|
|||||||
* @param {Object} ping - The ping utility for network checks.
|
* @param {Object} ping - The ping utility for network checks.
|
||||||
* @param {Object} logger - The logger instance for logging.
|
* @param {Object} logger - The logger instance for logging.
|
||||||
* @param {Object} http - The HTTP utility for network operations.
|
* @param {Object} http - The HTTP utility for network operations.
|
||||||
|
* @param {Object} net - The net utility for network operations.
|
||||||
*/
|
*/
|
||||||
class NetworkService {
|
class NetworkService {
|
||||||
constructor(axios, ping, logger, http, Docker) {
|
static SERVICE_NAME = SERVICE_NAME;
|
||||||
|
constructor(axios, ping, logger, http, Docker, net) {
|
||||||
this.TYPE_PING = "ping";
|
this.TYPE_PING = "ping";
|
||||||
this.TYPE_HTTP = "http";
|
this.TYPE_HTTP = "http";
|
||||||
this.TYPE_PAGESPEED = "pagespeed";
|
this.TYPE_PAGESPEED = "pagespeed";
|
||||||
this.TYPE_HARDWARE = "hardware";
|
this.TYPE_HARDWARE = "hardware";
|
||||||
this.TYPE_DOCKER = "docker";
|
this.TYPE_DOCKER = "docker";
|
||||||
this.SERVICE_NAME = "NetworkService";
|
this.TYPE_PORT = "port";
|
||||||
|
this.SERVICE_NAME = SERVICE_NAME;
|
||||||
this.NETWORK_ERROR = 5000;
|
this.NETWORK_ERROR = 5000;
|
||||||
this.PING_ERROR = 5001;
|
this.PING_ERROR = 5001;
|
||||||
this.axios = axios;
|
this.axios = axios;
|
||||||
@@ -22,6 +27,7 @@ class NetworkService {
|
|||||||
this.logger = logger;
|
this.logger = logger;
|
||||||
this.http = http;
|
this.http = http;
|
||||||
this.Docker = Docker;
|
this.Docker = Docker;
|
||||||
|
this.net = net;
|
||||||
}
|
}
|
||||||
|
|
||||||
/**
|
/**
|
||||||
@@ -262,6 +268,60 @@ class NetworkService {
|
|||||||
}
|
}
|
||||||
}
|
}
|
||||||
|
|
||||||
|
async requestPort(job) {
|
||||||
|
try {
|
||||||
|
const { url, port } = job.data;
|
||||||
|
const { response, responseTime, error } = await this.timeRequest(async () => {
|
||||||
|
return new Promise((resolve, reject) => {
|
||||||
|
const socket = this.net.createConnection(
|
||||||
|
{
|
||||||
|
host: url,
|
||||||
|
port,
|
||||||
|
},
|
||||||
|
() => {
|
||||||
|
socket.end();
|
||||||
|
socket.destroy();
|
||||||
|
resolve({ success: true });
|
||||||
|
}
|
||||||
|
);
|
||||||
|
|
||||||
|
socket.setTimeout(5000);
|
||||||
|
socket.on("timeout", () => {
|
||||||
|
socket.destroy();
|
||||||
|
reject(new Error("Connection timeout"));
|
||||||
|
});
|
||||||
|
|
||||||
|
socket.on("error", (err) => {
|
||||||
|
socket.destroy();
|
||||||
|
reject(err);
|
||||||
|
});
|
||||||
|
});
|
||||||
|
});
|
||||||
|
|
||||||
|
const portResponse = {
|
||||||
|
monitorId: job.data._id,
|
||||||
|
type: job.data.type,
|
||||||
|
responseTime,
|
||||||
|
};
|
||||||
|
|
||||||
|
if (error) {
|
||||||
|
portResponse.status = false;
|
||||||
|
portResponse.code = this.NETWORK_ERROR;
|
||||||
|
portResponse.message = errorMessages.PORT_FAIL;
|
||||||
|
return portResponse;
|
||||||
|
}
|
||||||
|
|
||||||
|
portResponse.status = response.success;
|
||||||
|
portResponse.code = 200;
|
||||||
|
portResponse.message = successMessages.PORT_SUCCESS;
|
||||||
|
return portResponse;
|
||||||
|
} catch (error) {
|
||||||
|
error.service = this.SERVICE_NAME;
|
||||||
|
error.method = "requestTCP";
|
||||||
|
throw error;
|
||||||
|
}
|
||||||
|
}
|
||||||
|
|
||||||
/**
|
/**
|
||||||
* Handles unsupported job types by throwing an error with details.
|
* Handles unsupported job types by throwing an error with details.
|
||||||
*
|
*
|
||||||
@@ -297,6 +357,9 @@ class NetworkService {
|
|||||||
return await this.requestHardware(job);
|
return await this.requestHardware(job);
|
||||||
case this.TYPE_DOCKER:
|
case this.TYPE_DOCKER:
|
||||||
return await this.requestDocker(job);
|
return await this.requestDocker(job);
|
||||||
|
case this.TYPE_PORT:
|
||||||
|
return await this.requestPort(job);
|
||||||
|
|
||||||
default:
|
default:
|
||||||
return this.handleUnsupportedType(type);
|
return this.handleUnsupportedType(type);
|
||||||
}
|
}
|
||||||
|
|||||||
@@ -1,4 +1,7 @@
|
|||||||
|
const SERVICE_NAME = "NotificationService";
|
||||||
|
|
||||||
class NotificationService {
|
class NotificationService {
|
||||||
|
static SERVICE_NAME = SERVICE_NAME;
|
||||||
/**
|
/**
|
||||||
* Creates an instance of NotificationService.
|
* Creates an instance of NotificationService.
|
||||||
*
|
*
|
||||||
@@ -7,7 +10,7 @@ class NotificationService {
|
|||||||
* @param {Object} logger - The logger instance for logging activities.
|
* @param {Object} logger - The logger instance for logging activities.
|
||||||
*/
|
*/
|
||||||
constructor(emailService, db, logger) {
|
constructor(emailService, db, logger) {
|
||||||
this.SERVICE_NAME = "NotificationService";
|
this.SERVICE_NAME = SERVICE_NAME;
|
||||||
this.emailService = emailService;
|
this.emailService = emailService;
|
||||||
this.db = db;
|
this.db = db;
|
||||||
this.logger = logger;
|
this.logger = logger;
|
||||||
|
|||||||
@@ -0,0 +1,35 @@
|
|||||||
|
const SERVICE_NAME = "ServiceRegistry";
|
||||||
|
import logger from "../utils/logger.js";
|
||||||
|
class ServiceRegistry {
|
||||||
|
static SERVICE_NAME = SERVICE_NAME;
|
||||||
|
constructor() {
|
||||||
|
this.services = {};
|
||||||
|
}
|
||||||
|
|
||||||
|
register(name, service) {
|
||||||
|
logger.info({
|
||||||
|
message: `Registering service ${name}`,
|
||||||
|
service: SERVICE_NAME,
|
||||||
|
method: "register",
|
||||||
|
});
|
||||||
|
this.services[name] = service;
|
||||||
|
}
|
||||||
|
|
||||||
|
get(name) {
|
||||||
|
if (!this.services[name]) {
|
||||||
|
logger.error({
|
||||||
|
message: `Service ${name} is not registered`,
|
||||||
|
service: SERVICE_NAME,
|
||||||
|
method: "get",
|
||||||
|
});
|
||||||
|
throw new Error(`Service ${name} is not registered`);
|
||||||
|
}
|
||||||
|
return this.services[name];
|
||||||
|
}
|
||||||
|
|
||||||
|
listServices() {
|
||||||
|
return Object.keys(this.services);
|
||||||
|
}
|
||||||
|
}
|
||||||
|
|
||||||
|
export default new ServiceRegistry();
|
||||||
@@ -25,6 +25,7 @@ const envConfig = {
|
|||||||
* from the database if they are not set in the environment.
|
* from the database if they are not set in the environment.
|
||||||
*/
|
*/
|
||||||
class SettingsService {
|
class SettingsService {
|
||||||
|
static SERVICE_NAME = SERVICE_NAME;
|
||||||
/**
|
/**
|
||||||
* Constructs a new SettingsService
|
* Constructs a new SettingsService
|
||||||
* @constructor
|
* @constructor
|
||||||
|
|||||||
@@ -1,4 +1,7 @@
|
|||||||
|
const SERVICE_NAME = "StatusService";
|
||||||
|
|
||||||
class StatusService {
|
class StatusService {
|
||||||
|
static SERVICE_NAME = SERVICE_NAME;
|
||||||
/**
|
/**
|
||||||
* Creates an instance of StatusService.
|
* Creates an instance of StatusService.
|
||||||
*
|
*
|
||||||
@@ -8,7 +11,7 @@ class StatusService {
|
|||||||
constructor(db, logger) {
|
constructor(db, logger) {
|
||||||
this.db = db;
|
this.db = db;
|
||||||
this.logger = logger;
|
this.logger = logger;
|
||||||
this.SERVICE_NAME = "StatusService";
|
this.SERVICE_NAME = SERVICE_NAME;
|
||||||
}
|
}
|
||||||
|
|
||||||
getStatusString = (status) => {
|
getStatusString = (status) => {
|
||||||
@@ -140,6 +143,7 @@ class StatusService {
|
|||||||
pagespeed: this.db.createPageSpeedCheck,
|
pagespeed: this.db.createPageSpeedCheck,
|
||||||
hardware: this.db.createHardwareCheck,
|
hardware: this.db.createHardwareCheck,
|
||||||
docker: this.db.createCheck,
|
docker: this.db.createCheck,
|
||||||
|
port: this.db.createCheck,
|
||||||
};
|
};
|
||||||
const operation = operationMap[networkResponse.type];
|
const operation = operationMap[networkResponse.type];
|
||||||
|
|
||||||
|
|||||||
@@ -59,6 +59,9 @@ const errorMessages = {
|
|||||||
// Docker
|
// Docker
|
||||||
DOCKER_FAIL: "Failed to fetch Docker container information",
|
DOCKER_FAIL: "Failed to fetch Docker container information",
|
||||||
DOCKER_NOT_FOUND: "Docker container not found",
|
DOCKER_NOT_FOUND: "Docker container not found",
|
||||||
|
|
||||||
|
// Port
|
||||||
|
PORT_FAIL: "Failed to connect to port",
|
||||||
};
|
};
|
||||||
|
|
||||||
const successMessages = {
|
const successMessages = {
|
||||||
@@ -129,6 +132,9 @@ const successMessages = {
|
|||||||
|
|
||||||
// Docker
|
// Docker
|
||||||
DOCKER_SUCCESS: "Docker container status fetched successfully",
|
DOCKER_SUCCESS: "Docker container status fetched successfully",
|
||||||
|
|
||||||
|
// Port
|
||||||
|
PORT_SUCCESS: "Port connected successfully",
|
||||||
};
|
};
|
||||||
|
|
||||||
export { errorMessages, successMessages };
|
export { errorMessages, successMessages };
|
||||||
@@ -144,10 +144,12 @@ const getMonitorsAndSummaryByTeamIdQueryValidation = joi.object({
|
|||||||
type: joi
|
type: joi
|
||||||
.alternatives()
|
.alternatives()
|
||||||
.try(
|
.try(
|
||||||
joi.string().valid("http", "ping", "pagespeed", "docker", "hardware"),
|
joi.string().valid("http", "ping", "pagespeed", "docker", "hardware", "port"),
|
||||||
joi
|
joi
|
||||||
.array()
|
.array()
|
||||||
.items(joi.string().valid("http", "ping", "pagespeed", "docker", "hardware"))
|
.items(
|
||||||
|
joi.string().valid("http", "ping", "pagespeed", "docker", "hardware", "port")
|
||||||
|
)
|
||||||
),
|
),
|
||||||
});
|
});
|
||||||
|
|
||||||
@@ -163,10 +165,12 @@ const getMonitorsByTeamIdQueryValidation = joi.object({
|
|||||||
type: joi
|
type: joi
|
||||||
.alternatives()
|
.alternatives()
|
||||||
.try(
|
.try(
|
||||||
joi.string().valid("http", "ping", "pagespeed", "docker", "hardware"),
|
joi.string().valid("http", "ping", "pagespeed", "docker", "hardware", "port"),
|
||||||
joi
|
joi
|
||||||
.array()
|
.array()
|
||||||
.items(joi.string().valid("http", "ping", "pagespeed", "docker", "hardware"))
|
.items(
|
||||||
|
joi.string().valid("http", "ping", "pagespeed", "docker", "hardware", "port")
|
||||||
|
)
|
||||||
),
|
),
|
||||||
page: joi.number(),
|
page: joi.number(),
|
||||||
rowsPerPage: joi.number(),
|
rowsPerPage: joi.number(),
|
||||||
@@ -199,6 +203,7 @@ const createMonitorBodyValidation = joi.object({
|
|||||||
description: joi.string().required(),
|
description: joi.string().required(),
|
||||||
type: joi.string().required(),
|
type: joi.string().required(),
|
||||||
url: joi.string().required(),
|
url: joi.string().required(),
|
||||||
|
port: joi.number(),
|
||||||
isActive: joi.boolean(),
|
isActive: joi.boolean(),
|
||||||
interval: joi.number(),
|
interval: joi.number(),
|
||||||
thresholds: joi.object().keys({
|
thresholds: joi.object().keys({
|
||||||
|
|||||||
Reference in new issue
Block a user